 Mobileeurope
Ericsson Demonstrates Drone Detection Technology in Poland
Article Content

- •Ericsson's ISAC technology can detect unauthorized drones using mobile networks.
- •The demonstration took place on October 15, 2026, at Ericsson's R&D Center in Kraków.
- •The event was attended by key stakeholders from the Polish government and defense sector.
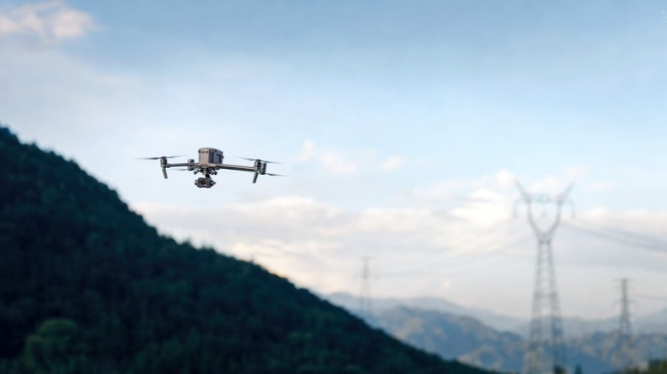
Ericsson, in collaboration with Play and Asseco, showcased its Integrated Sensing and Communication (ISAC) technology for drone detection in Poland on October 15, 2026. The demonstration highlighted the ability to detect and track unauthorized drones using mobile networks, particularly in sensitive areas like airports and borders. The ISAC technology utilizes radio signals to identify drones even when they are not connected to a network, while Asseco's PUSZCZYK platform integrates sound detection methods. The event attracted various stakeholders, including government representatives and military officials. The technology aims to enhance situational awareness and protect critical infrastructure in Poland. No specific vulnerabilities or active threats were reported in relation to this technology demonstration.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Play and Asseco Poland in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is ISAC technology?
Who attended the demonstration?
What areas are targeted for drone detection?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…