 Techspot
ESA Labels Anbernic Handhelds as 'Superfakes' Amid Piracy Concerns
Article Content

- •ESA targets Anbernic for selling devices preloaded with pirated games.
- •The term 'superfake' describes high-quality counterfeit goods that facilitate piracy.
- •Inclusion on the USTR's Notorious Market List could lead to increased enforcement actions.
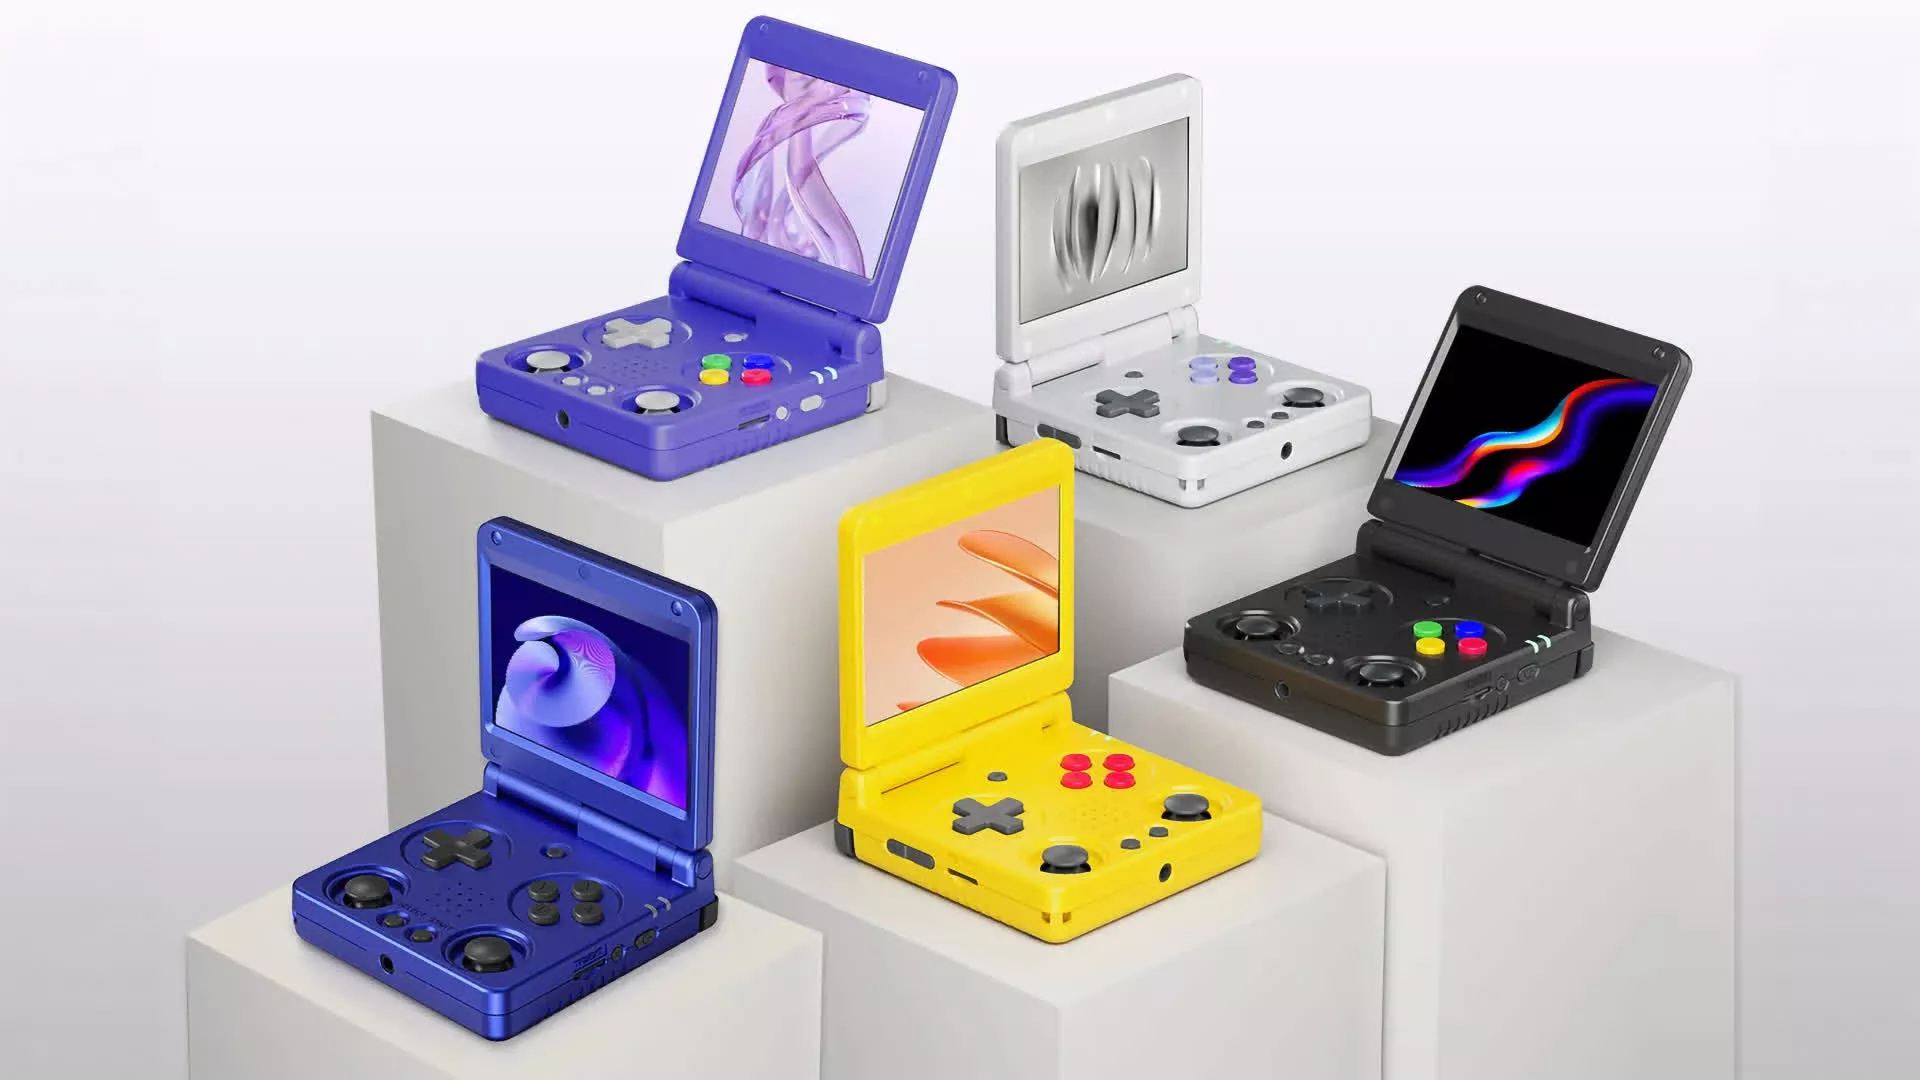
The Entertainment Software Association (ESA) has urged the U.S. Trade Representative (USTR) to classify Anbernic handheld gaming devices as 'superfakes' due to their association with piracy. These devices, which often come preloaded with unauthorized game ROMs, are said to normalize hardware-based piracy. The ESA's submission follows a significant enforcement operation in Italy that seized 12,000 Anbernic devices containing over 47 million pirated games. The ESA warns that these devices may also pose security risks, potentially harboring malicious software. While inclusion on the USTR's Notorious Market List does not guarantee immediate legal action, it could lead to increased scrutiny and enforcement against Anbernic and similar manufacturers. The ESA's recommendations highlight broader concerns about the impact of such piracy on the gaming industry and consumer safety.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Anbernic in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What are 'superfakes'?
What actions is the ESA proposing?
What risks do these devices pose?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…