 Omanobserver.Om
ETCO Space and Open Cosmos Sign Satellite Technology Agreement
Article Content

- •ETCO Space and Open Cosmos signed a cooperation agreement on satellite technology.
- •The partnership aims to enhance capabilities in Earth observation and geospatial services.
- •Applications include coastal monitoring, pollution tracking, and support for security and defense sectors.
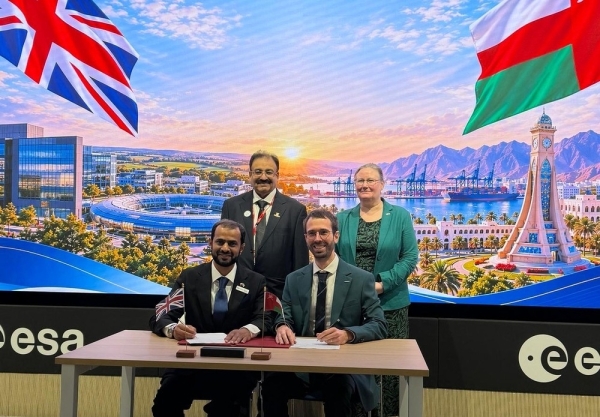
On October 25, 2026, Oman’s ETCO Space signed a cooperation agreement with Britain’s Open Cosmos to enhance satellite technology and Earth observation capabilities. The partnership aims to improve coastal monitoring, pollution tracking, and services for security, defense, energy, and minerals sectors. Dr. Abdulaziz bin Amer al Sawai, CEO of ETCO Space, and Jordi Barrera, CTO of Open Cosmos, signed the agreement to foster knowledge transfer and technical training. This collaboration is expected to strengthen Oman’s space sector and expand the use of satellite technologies across various industries. The agreement reflects growing ties between Oman and the UK, focusing on advanced technologies and geospatial services.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track ETCO Space in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What are the main goals of the agreement?
Who signed the agreement?
What sectors will benefit from this partnership?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…