 Radiomoldova.Md
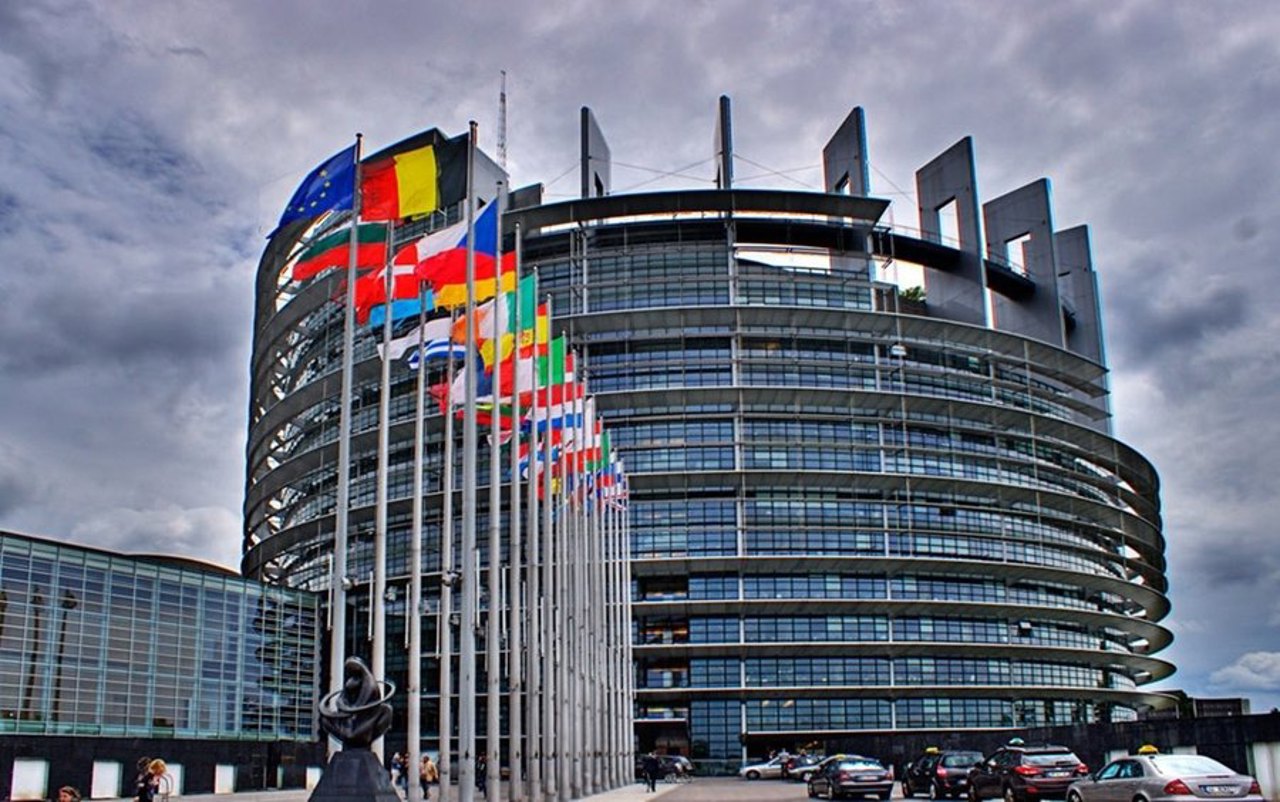
EU Parliament Supports Moldova's EU Accession Amid Russian Interference Concerns
Article Content

- •The European Parliament's Committee endorsed Moldova's EU accession with 58 votes.
- •MEPs warned of Russian interference threatening Moldova's democratic processes.
- •The report calls for enhanced support in cybersecurity and institutional resilience for Moldova.
On June 3, 2026, the European Parliament's Committee on Foreign Affairs endorsed a report supporting Moldova's EU accession efforts, urging immediate negotiations. The report, approved with 58 votes, emphasizes Moldova's progress in judicial reform and anti-corruption measures while warning against Russian interference. Rapporteur Sven Mikser highlighted the importance of rewarding Moldova's reforms and called for expedited negotiations ahead of the June 18-19 European summit. The committee also stressed the need for enhanced support for Moldova's cybersecurity and institutional resilience to counteract Russian malign influence. In a related report, the committee praised Ukraine's reform efforts amidst ongoing conflict. The committee's actions reflect a broader geopolitical strategy to strengthen ties with Eastern European nations in the face of Russian aggression.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…