 Themoscowtimes
EU Imposes New Sanctions on Russia Amid Ongoing Ukraine Conflict
Article Content

- •EU sanctions target over 80 individuals and entities linked to Russia's war in Ukraine.
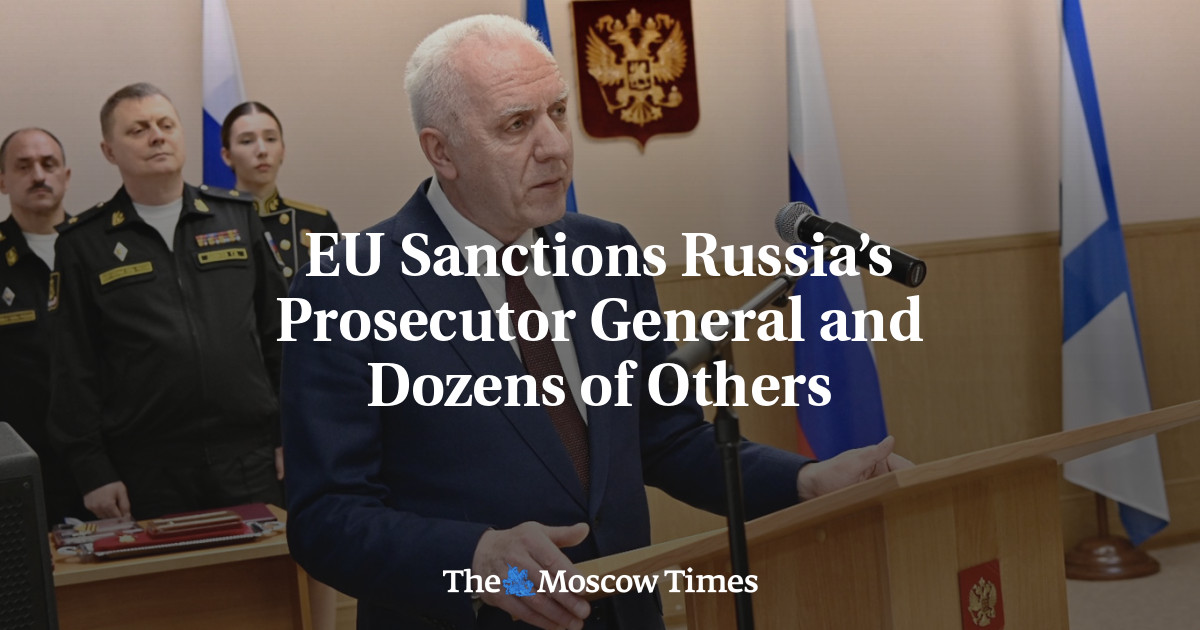
- •Key figures include Prosecutor General Alexander Gutsan and Metropolitan Tikhon, Putin's confessor.
- •Sanctions aim to disrupt Russia's military-industrial complex and oil export evasion efforts.
On June 15, 2026, the European Union sanctioned over 80 individuals and entities linked to Russia's military actions in Ukraine. Key figures targeted include Prosecutor General Alexander Gutsan and Metropolitan Tikhon, described as Putin's personal confessor, for their roles in supporting the war and spreading propaganda. The sanctions aim to disrupt Russia's military-industrial complex and its shadow fleet, which facilitates oil export evasion. The EU's foreign policy chief, Kaja Kallas, stated that these measures are designed to collapse the foundations of Russia's war economy, which has already incurred losses estimated between €1 trillion and €1.3 trillion. The sanctions also include asset freezes and travel bans, affecting individuals involved in the persecution of opposition figures like Alexei Navalny. This latest round of sanctions follows a recent missile attack by Russia on Ukrainian cities, prompting calls for increased pressure on Moscow from international leaders.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…