 Biometricupdate
EU Supports Libyan Border Management with Biometric Training
Article Content

- •Libyan officials received EU-backed training on biometrics and document security.
- •Training included practical exercises in live border checks at Ancona International Port.
- •The initiative aims to strengthen Libya's integrated border management amid migration challenges.
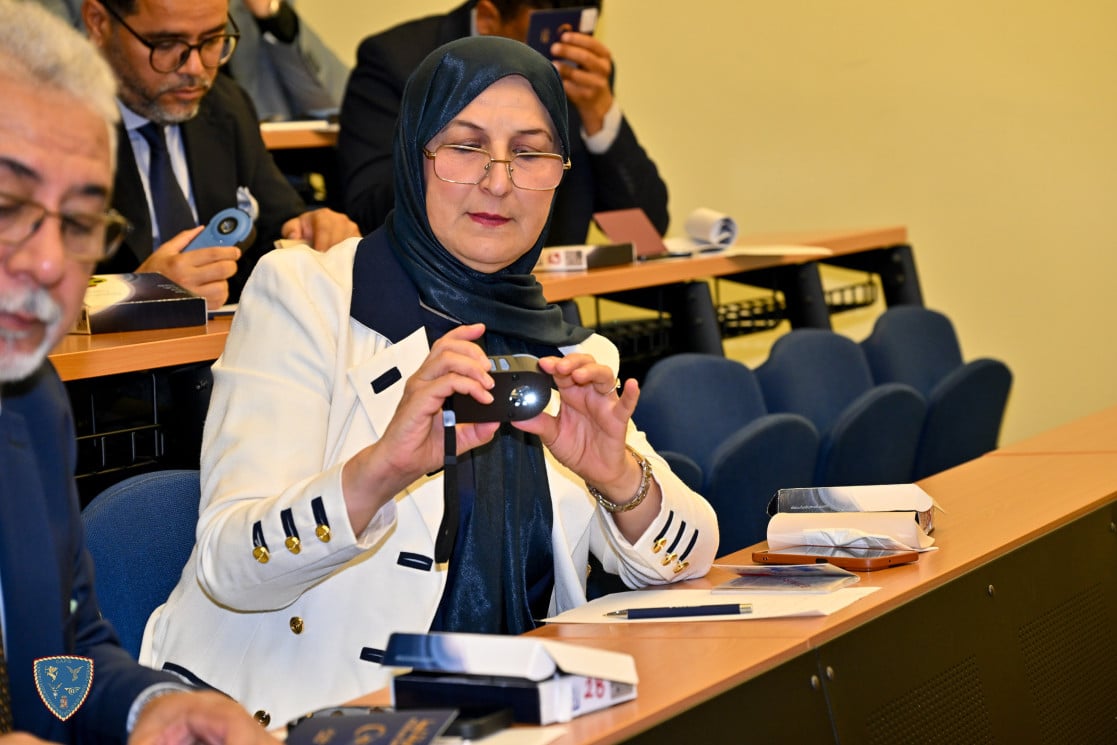
Officials from three Libyan ministries and the Customs Authority received training on biometrics and document security at the Italian State Police Academy as part of an EU initiative. The training focused on advanced document security, including the detection of fraudulent documents. Participants observed live border checks at Ancona International Port, where they learned about interoperability and risk-based inspections. This initiative aims to enhance Libya's integrated border management, especially as the country deals with migration issues. The training is part of the EU Border Assistance Mission in Libya, which has been operational since 2013. The discussions also included modernizing Libya's security infrastructure at various entry points.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Rapiscan Systems in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What was the focus of the training?
Which agencies were involved in the training?
What is the goal of this EU initiative?
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…