 Pbs
Evan Gershkovich's Detention and Release from Russia
Article Content
Browse articles 
- •Evan Gershkovich was arrested in March 2023 while reporting on Russian military activities.
- •He was sentenced to 16 years on espionage charges, which he denies.
- •Gershkovich was released in 2024 as part of a prisoner swap involving multiple countries.
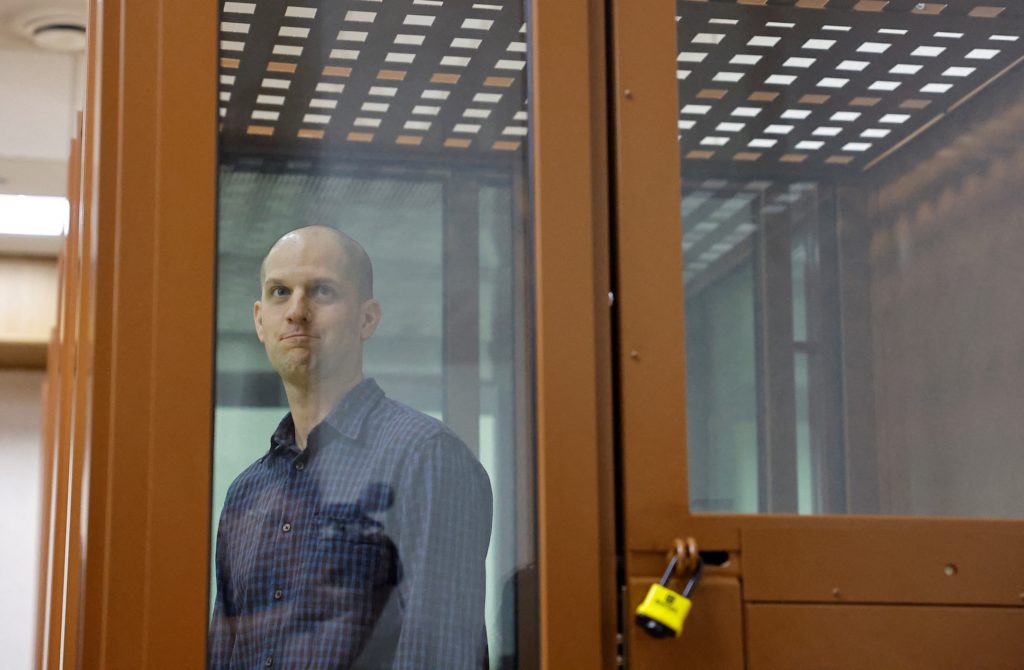
Evan Gershkovich, a Wall Street Journal correspondent, was detained in Russia in March 2023 while reporting on military activities. He was arrested by masked men during a meeting with a source, later sentenced to 16 years on espionage charges, which he and his employer claim were false. In 2024, he was released as part of a complex prisoner swap involving 16 individuals from seven countries. Gershkovich has since reflected on his experiences in a new book titled 'This Cursed Beautiful Land.' His case highlights the risks faced by journalists in Russia and the geopolitical tensions between the U.S. and Russia regarding press freedom.
Ask AI about this cluster
Answers cite the sources they use
Updated just now How this analysis works
Timeline
More articles in this cluster (2)
Common questions
What were the charges against Gershkovich?
He was charged with espionage, which he and the Wall Street Journal have denied.
How long was he detained?
Gershkovich was detained for approximately 16 months before his release in 2024.
What is the significance of his case?
His case highlights the dangers journalists face in authoritarian regimes and the geopolitical tensions between the U.S. and Russia.
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…