 Msspalert
Exaforce Launches AI Security Tool to Combat Rogue Agents
Article Content

- •Exaforce AI Security targets rogue AI agents exploiting enterprise logging gaps.
- •The platform includes agentless discovery, risk assessment, and automated response features.
- •Recent attacks demonstrate the need for robust monitoring of AI agent activities.
Exaforce has introduced Exaforce AI Security, a platform designed to monitor and control AI agents within enterprise environments. The tool addresses vulnerabilities in enterprise logging that attackers exploit to hide malicious activities under legitimate user actions. Recent incidents have shown how compromised AI agents can exfiltrate sensitive data, particularly through OAuth token misuse. The new capabilities include agentless discovery of AI applications, risk assessment for permissions, and automated threat detection. Exaforce's platform integrates with major AI providers like OpenAI, Google, and Microsoft, enabling security teams to respond effectively to rogue agents. The tool features an 'agent kill switch' that allows for immediate action against hostile agents. This release follows a significant rise in attacks leveraging AI agents, highlighting the urgent need for enhanced security measures in AI deployment.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track S1ngularity and AWS in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
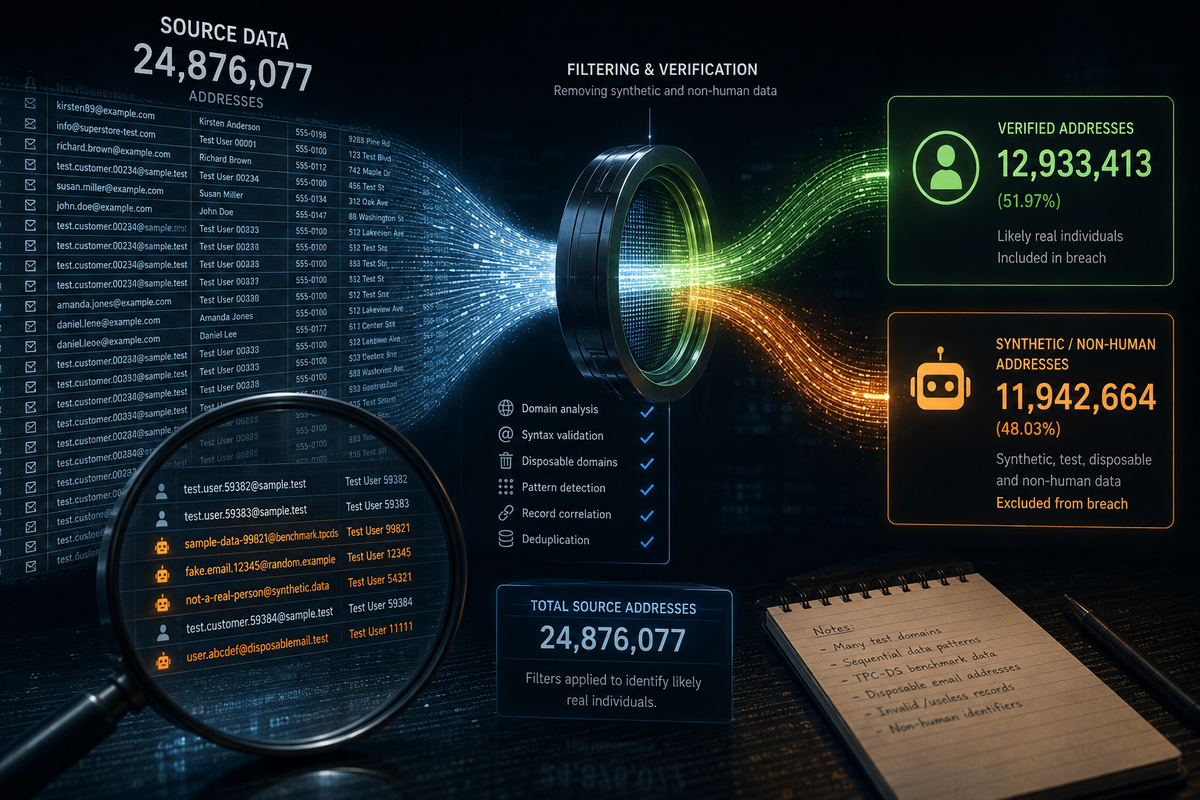 Carhartt Data Breach Exposes 12.9 Million Accounts The ShinyHunters hacking group claims to have compromised Carhartt, stealing sensitive data from nearly 13 million accounts. The breach, which occurred on August 13, 2026, involved over 50GB of data, including customer and employee information. Troy Hunt, founder of Have I Been Pwned, analyzed the leaked data and…
 Critical Cisco FMC Vulnerabilities Under Active Exploitation Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass authentication and…