 Taipeitimes
Executives Detained Over Use of Prohibited China-Made Drone Components
Article Content

- •Two executives from Jiin Ming Industry Co detained for using prohibited components.
- •Allegations involve China-made chips and camera lenses in military drones.
- •Prosecutors raided company offices and suppliers as part of the investigation.
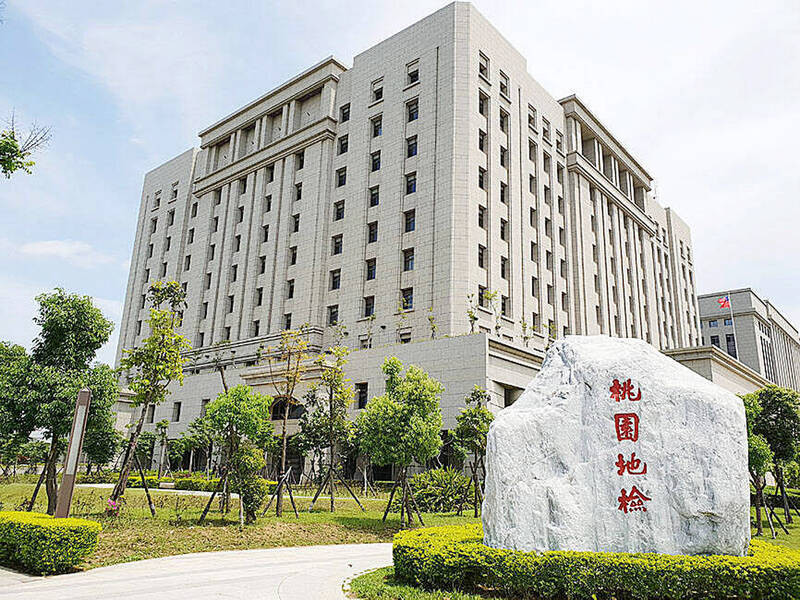
Two executives from Jiin Ming Industry Co have been detained by the Taoyuan District Prosecutors' Office for allegedly using prohibited China-made chips and camera lenses in military drones. The company is accused of breaching procurement contracts by incorporating these components into drones supplied to the military. Prosecutors conducted raids on the company's headquarters and its suppliers, following a report of the violations. The investigation is ongoing, and the executives are currently held incommunicado. This incident raises concerns about the integrity of military supply chains and compliance with procurement regulations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Jiin Ming Industry Co in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What specific components are involved?
What are the implications for military contracts?
What actions are being taken against Jiin Ming Industry Co?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…