 Today.Thefinancialexpress.Bd
Fake News Declared National Security Threat by Bangladesh Minister
Article Content

- •Fake news is now considered a national security threat in Bangladesh.
- •The rise of AI has made the creation and dissemination of misinformation easier.
- •The government seeks actionable policy recommendations from ICT experts to combat cyber risks.
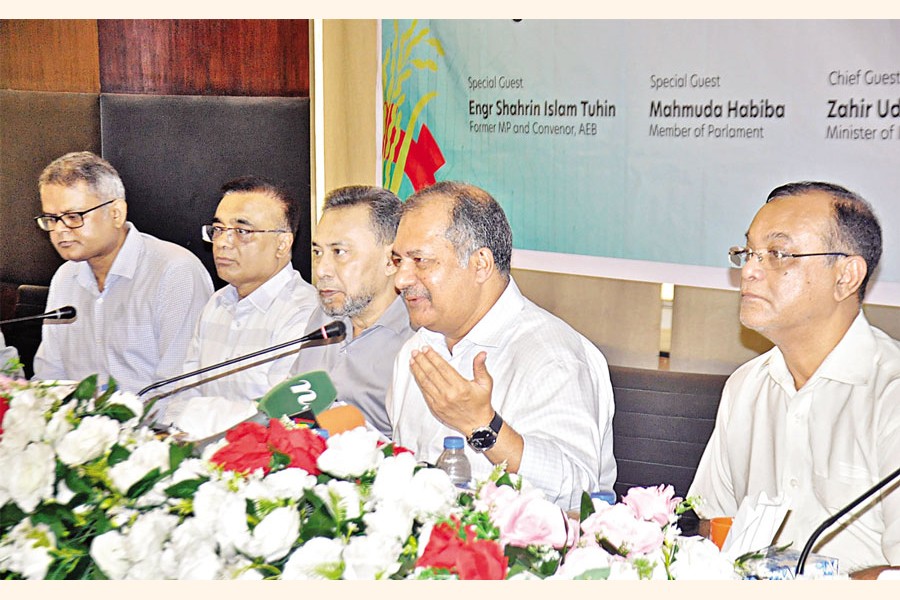
On June 6, 2026, Information and Broadcasting Minister Zahir Uddin Swapon stated that fake news has become a national security threat in Bangladesh. He urged ICT experts to draft a national action plan to combat cyber risks and ensure online safety. The minister highlighted that the rise of Artificial Intelligence (AI) has facilitated the creation and spread of misinformation, posing significant challenges to social stability and state interests. Swapon emphasized the need for realistic policy recommendations to address these issues effectively. He also pointed out the global trend of regulating technology giants like Meta Platforms and Google, which profit from content created by mainstream media without compensation. The discussion took place during a roundtable organized by the Nationalist ICT Forum (NICTF), where various experts shared insights on combating fake news and enhancing digital literacy.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (16)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…