 Foxnews
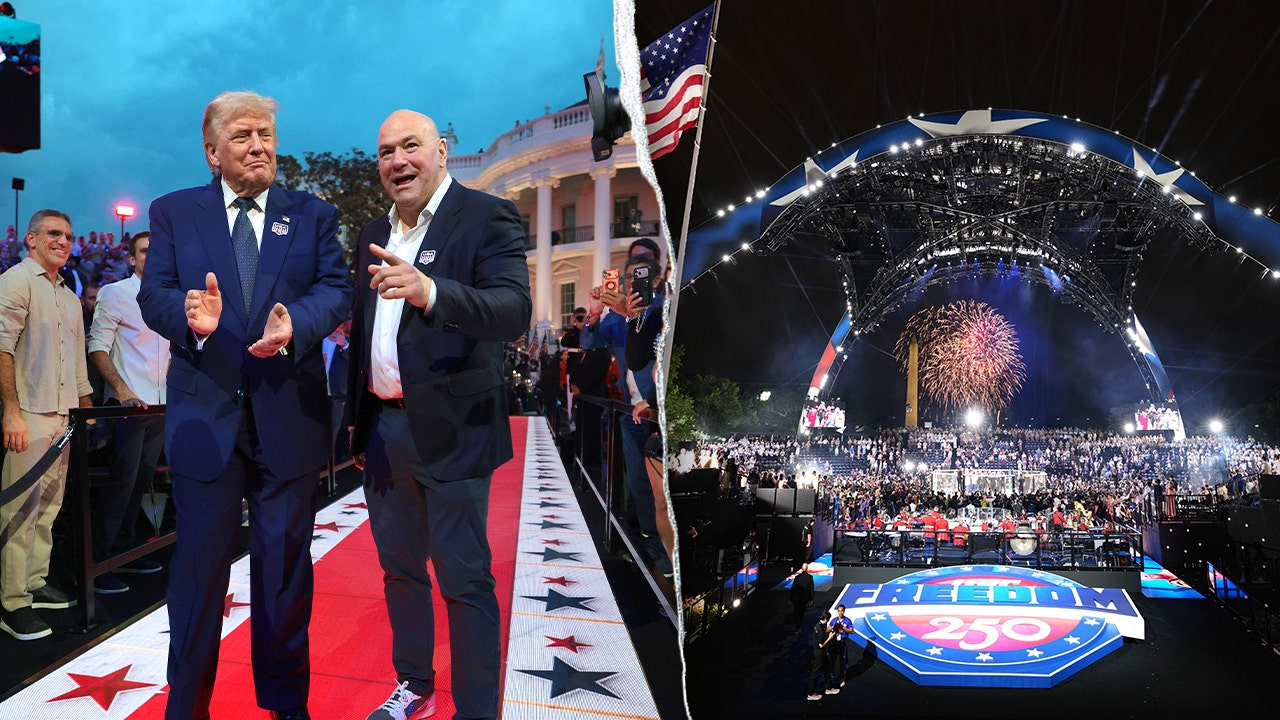
FBI Thwarts Explosive Drone Plot Targeting White House UFC Event
Article Content

- •Five suspects arrested in a multi-state operation targeting a UFC event at the White House.
- •The plot involved using explosive drones to create chaos and facilitate a sniper attack.
- •A total of 23 individuals are identified as part of the potential network of plotters.
On June 10, 2026, the FBI disrupted a plot involving five men who planned to attack the UFC Freedom 250 event at the White House using explosive-laden drones. The suspects aimed to create panic by targeting nearby buildings, prompting a mass evacuation, and then directing crowds toward a pre-staged sniper team. The investigation revealed a potential network of 23 individuals involved in the plot, with arrests made across multiple states including Ohio, California, Missouri, and Nebraska. Tycen Proper, a 19-year-old suspect, reportedly spent $3,000 of his graduation money on weapons and communicated with an anti-government group online. The FBI's swift action prevented what could have been a devastating attack during a high-profile event attended by President Trump and other officials. The investigation is ongoing, with more suspects potentially still at large.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (18)
Following this threat?
Track UFC in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…