 Bleepingcomputer
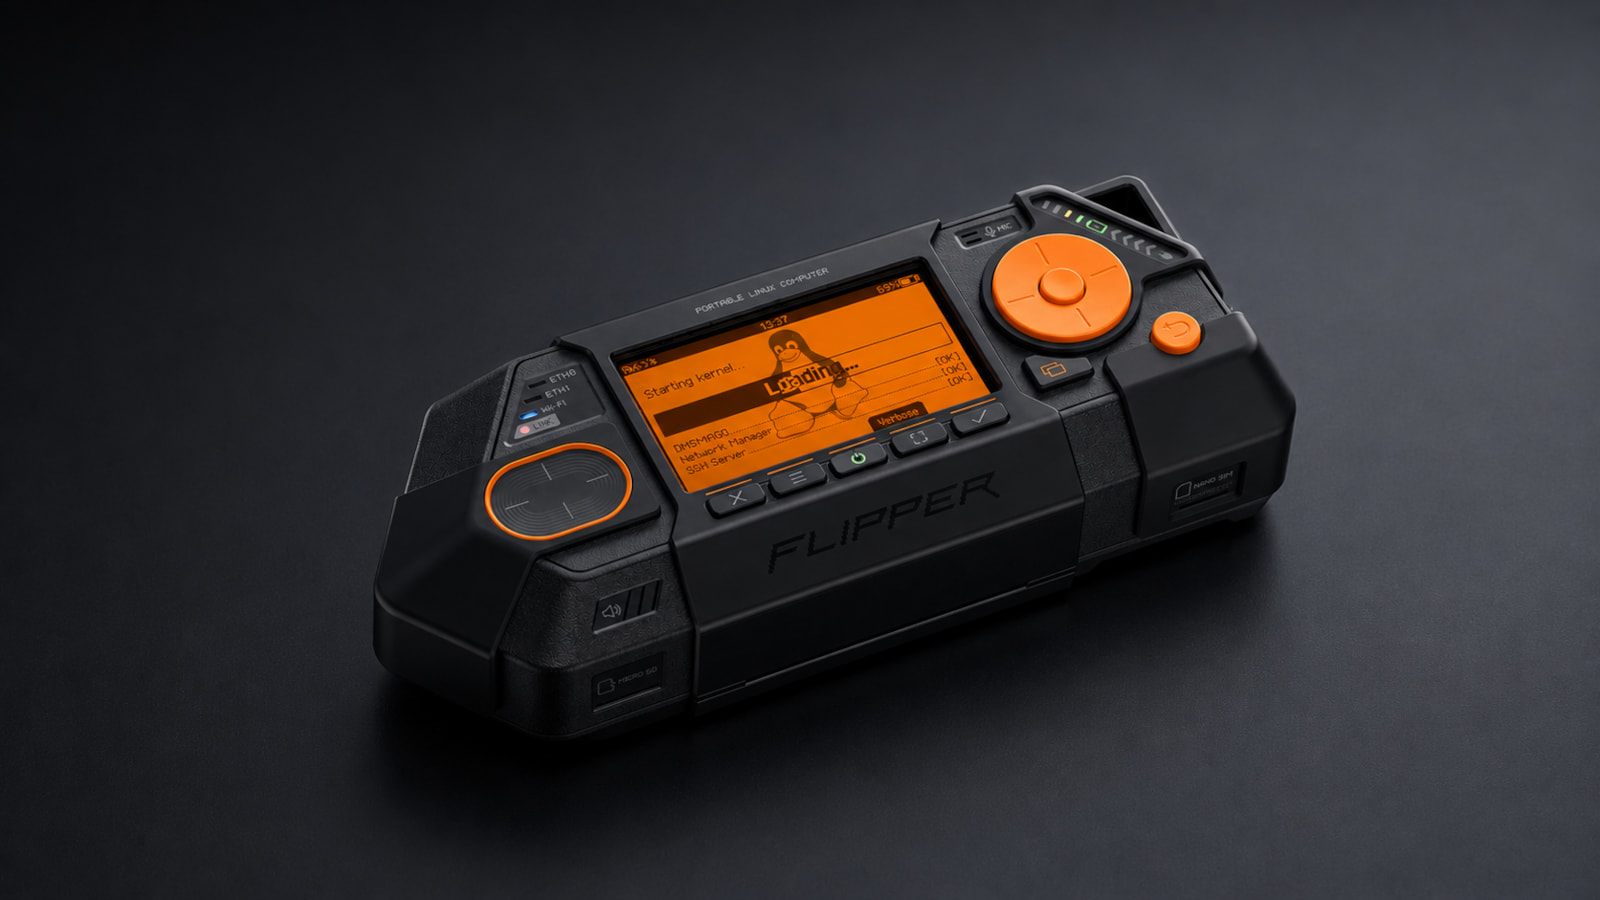
Flipper One: New Modular Linux Device for Hackers and Tinkerers Unveiled
Article Content

- •Flipper One is a new modular Linux computer aimed at hackers and tinkerers.
- •It features a Rockchip RK3576 CPU and supports various connectivity options.
- •The device is still in development, with community involvement encouraged for its open-source platform.
Flipper Devices has announced the Flipper One, a modular ARM-based Linux computer designed for networking and hardware experimentation. Unlike its predecessor, the Flipper Zero, which focused on hacking radio technologies, the Flipper One aims to provide a high-performance platform for various applications, including VPN gateways and portable Linux workstations. The device features a Rockchip RK3576 CPU, 8 GB of RAM, and multiple connectivity options, including Gigabit Ethernet and Wi-Fi 6E. It is not yet available for purchase, as the company is still developing the product and seeking community involvement for its open-source platform. The first prototypes have been completed, but challenges remain in software support and hardware integration. Flipper Devices is working with Collabora to ensure full mainline Linux kernel support for the device. The anticipated price is around $350, but this may fluctuate due to current chip market conditions.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…