 United24Media
Belarusian National Arrested for Spying on French Drone Production Facility
Article Content

- •A Belarusian man was arrested in France for allegedly spying on a drone factory.
- •The suspect filmed a prototype drone and sent the footage to Russia.
- •The incident is part of a larger pattern of Russian espionage targeting European defense industries.
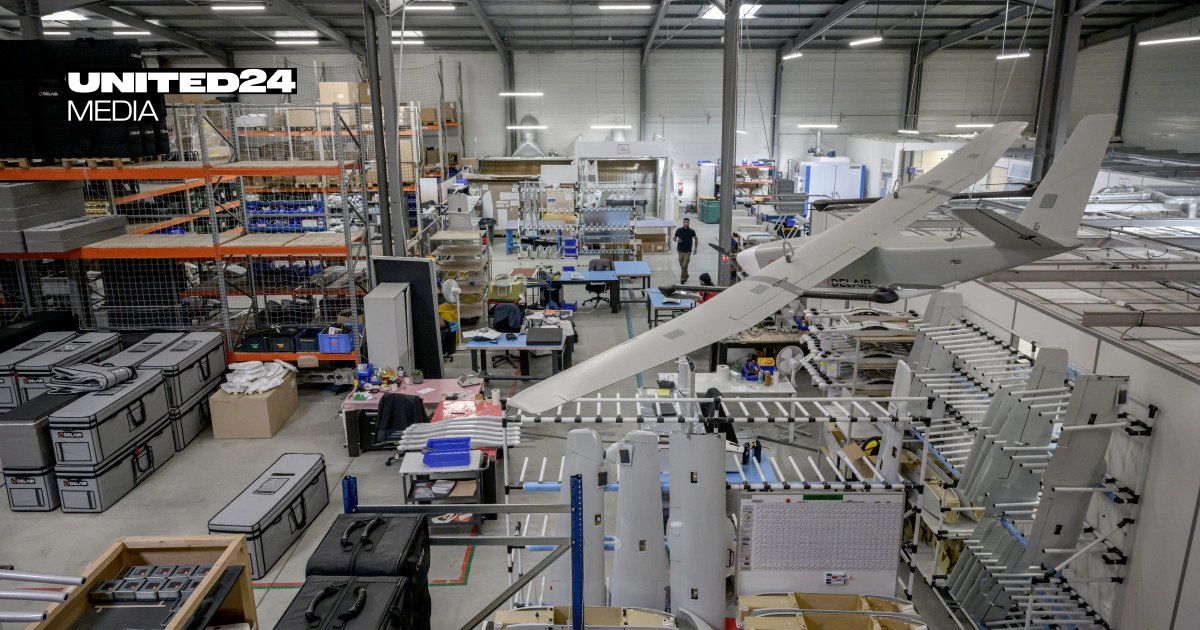
French authorities arrested a 48-year-old Belarusian man on June 3, 2026, for allegedly spying for Russia at a drone manufacturing facility in Labège, near Toulouse. The suspect was caught filming a prototype drone that supplies both the French and Ukrainian armed forces. He reportedly sent the footage to a contact in Russia. This incident follows an attack on the same facility involving Molotov cocktails just days prior, indicating a potential sabotage attempt. The man has been charged with providing information to a foreign power, facing a possible 15-year prison sentence. The case highlights a broader trend of Russian espionage targeting European industrial sectors, particularly in defense technology. France's General Directorate for Internal Security (DGSI) is leading the investigation, which is part of a growing concern over Russian intelligence activities in Europe.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (9)
Following this threat?
Track Delair in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…