 www.ebrd.com
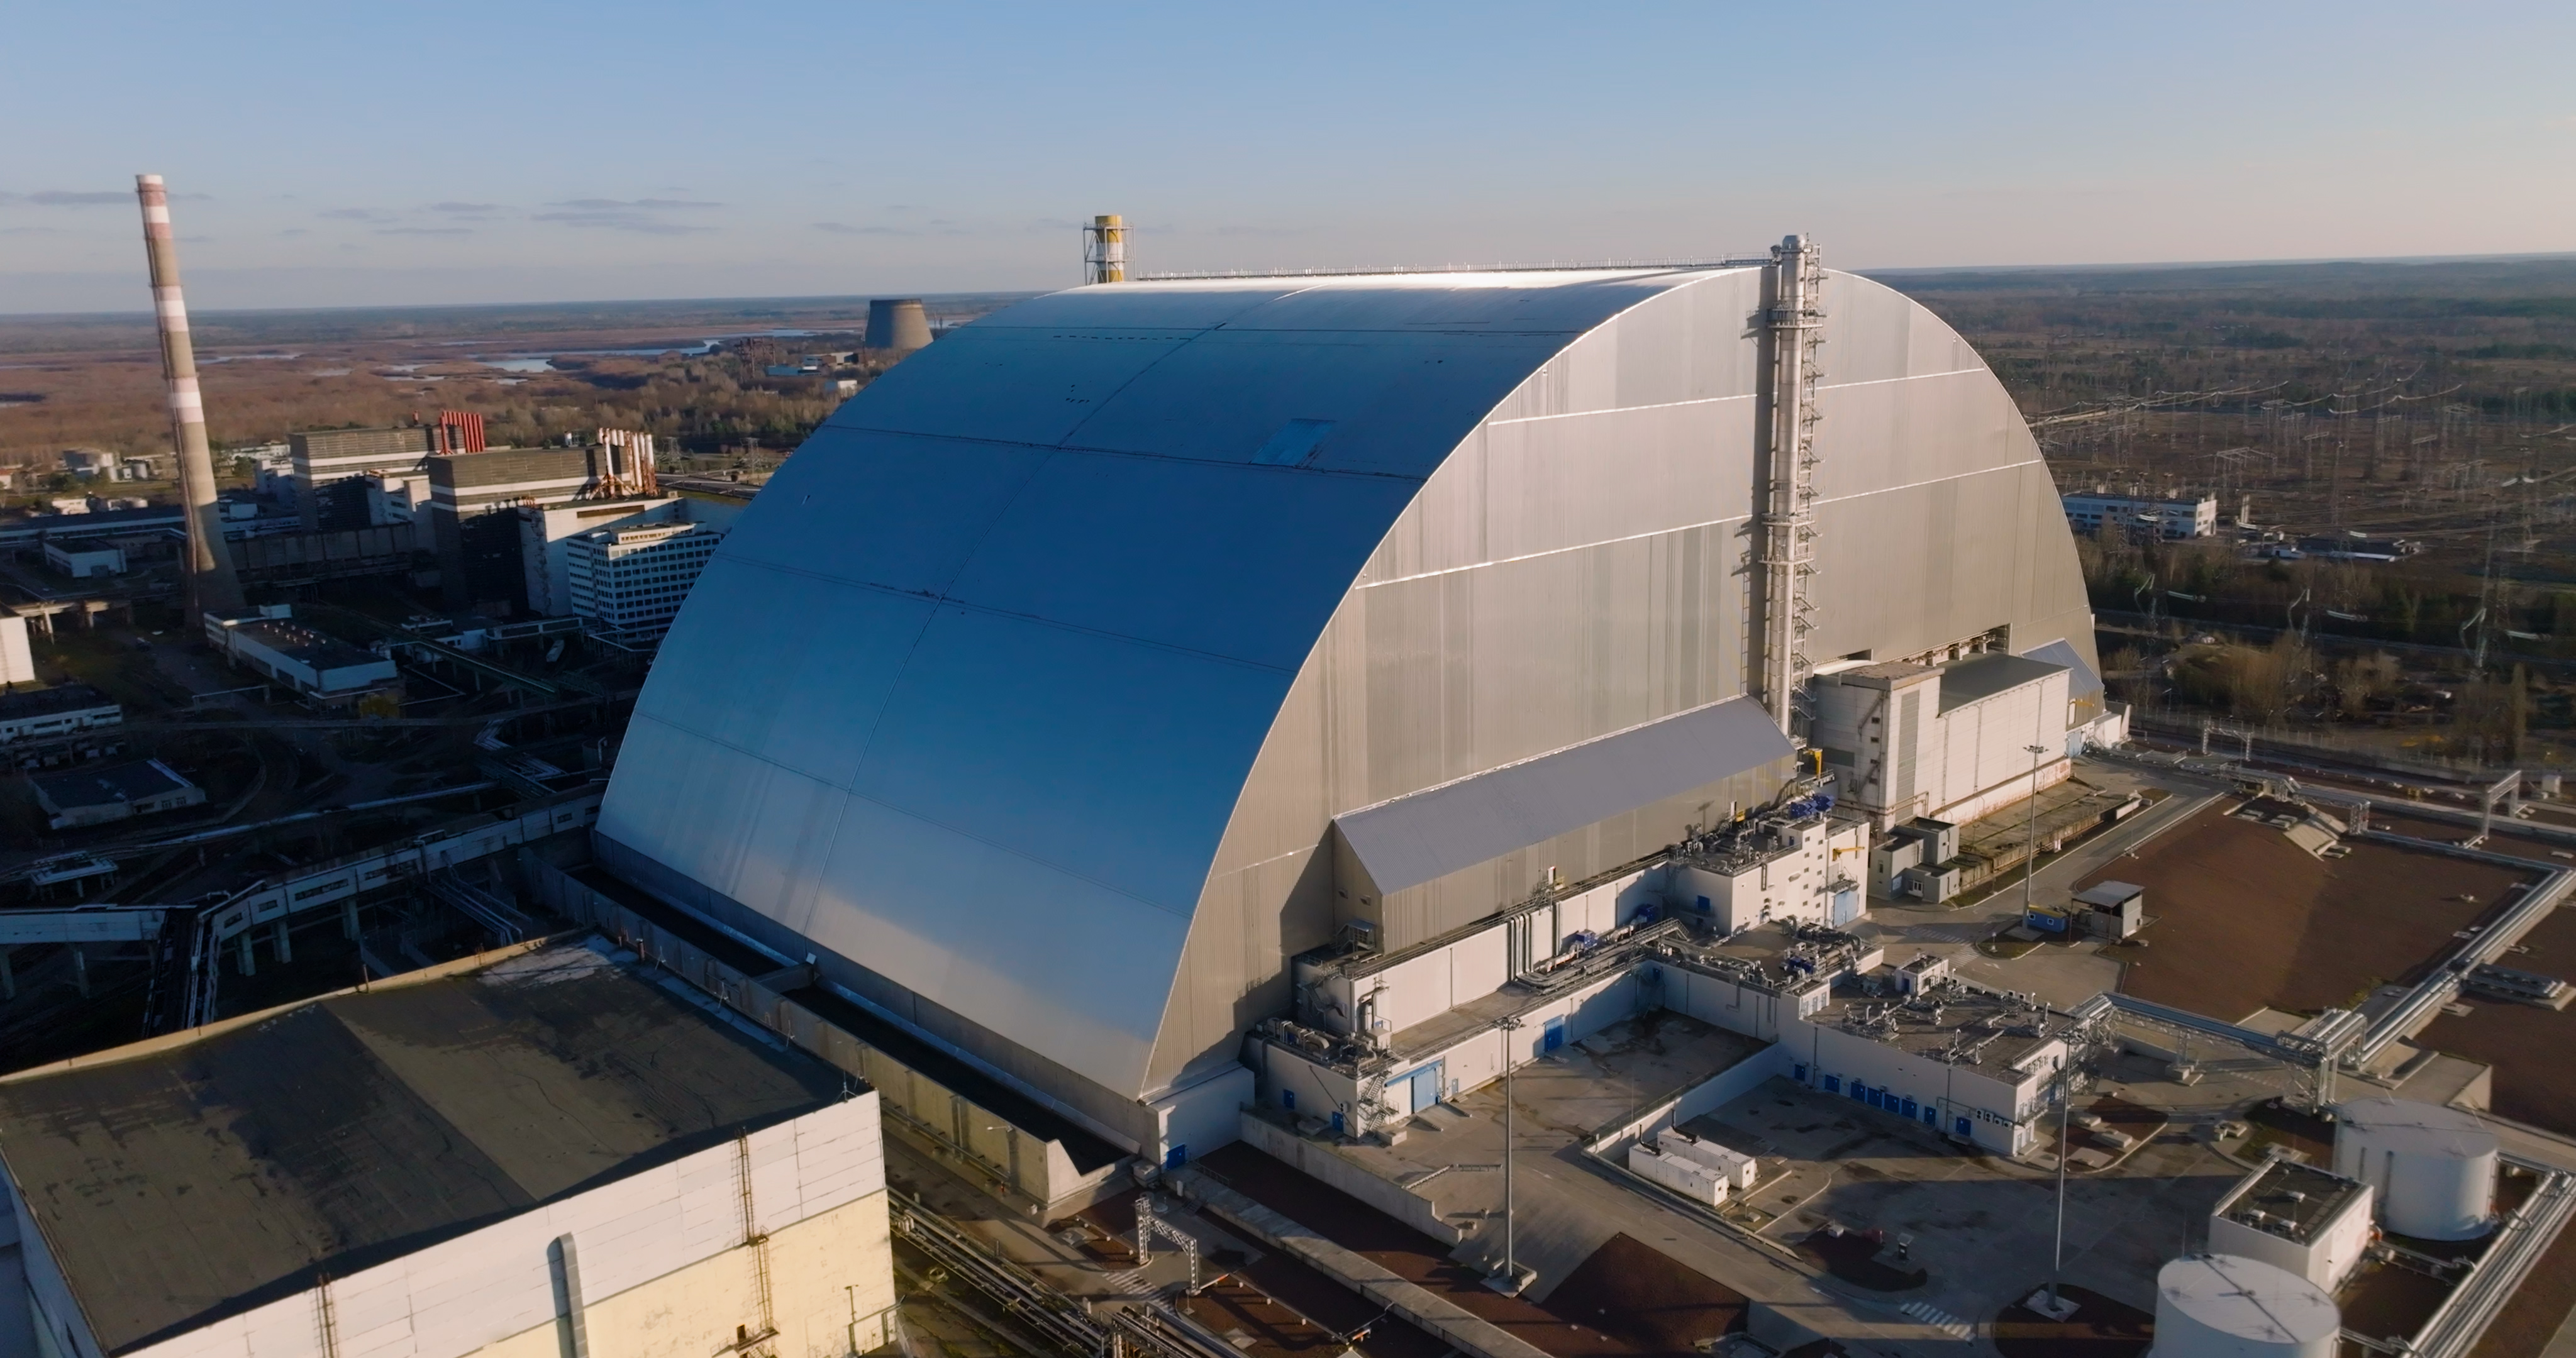
G7 Pledges €260M for Chornobyl Repairs After Drone Strike
Article Content

- •EBRD seeks €500 million for Chornobyl repairs after a Russian drone strike.
- •G7 nations pledged €260 million for urgent repairs to the New Safe Confinement.
- •Repairs must be completed by 2030 to prevent further environmental risks.
The European Bank for Reconstruction and Development (EBRD) is seeking €500 million to repair the New Safe Confinement at Chornobyl, which was damaged by a Russian drone strike in February 2025. The G7 nations have pledged €260 million to assist with these urgent repairs, highlighting the global concern over nuclear safety risks. EBRD President Odile Renaud-Basso emphasized that repairs must be completed by 2030 to prevent further deterioration. The donor conference in Paris aims to secure additional funding, although full financing is not expected immediately. The strike compromised containment systems designed to manage radioactive materials, raising alarms about potential environmental hazards. Renaud-Basso noted that the costs could be recouped through future war reparations from Russia, which is not expected to contribute to the repair costs. Major restoration work is anticipated to begin in 2028, with repairs projected to take around two years.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What is the total funding needed for repairs?
When is the donor conference taking place?
What are the consequences of the drone strike?
Continue Reading
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…
 GitLab Issues Emergency Patch for Critical RCE Vulnerability GitLab has released emergency patches for a critical remote code execution vulnerability, CVE-2026-97229, affecting its Community and Enterprise Editions. This flaw, stemming from an integer overflow in the CI/CD regular expression compiler, allows unauthenticated attackers to execute arbitrary code via specially…