 www.biometricupdate.com
German BSI Report Reveals Vulnerabilities in Windows Hello Biometric Security
Article Content

- •The BSI report highlights vulnerabilities in Windows Hello for Business biometric security.
- •Without Enhanced Sign-in Security, biometric data is inadequately protected against privileged attackers.
- •The system is susceptible to presentation attacks, allowing unauthorized access through masks.
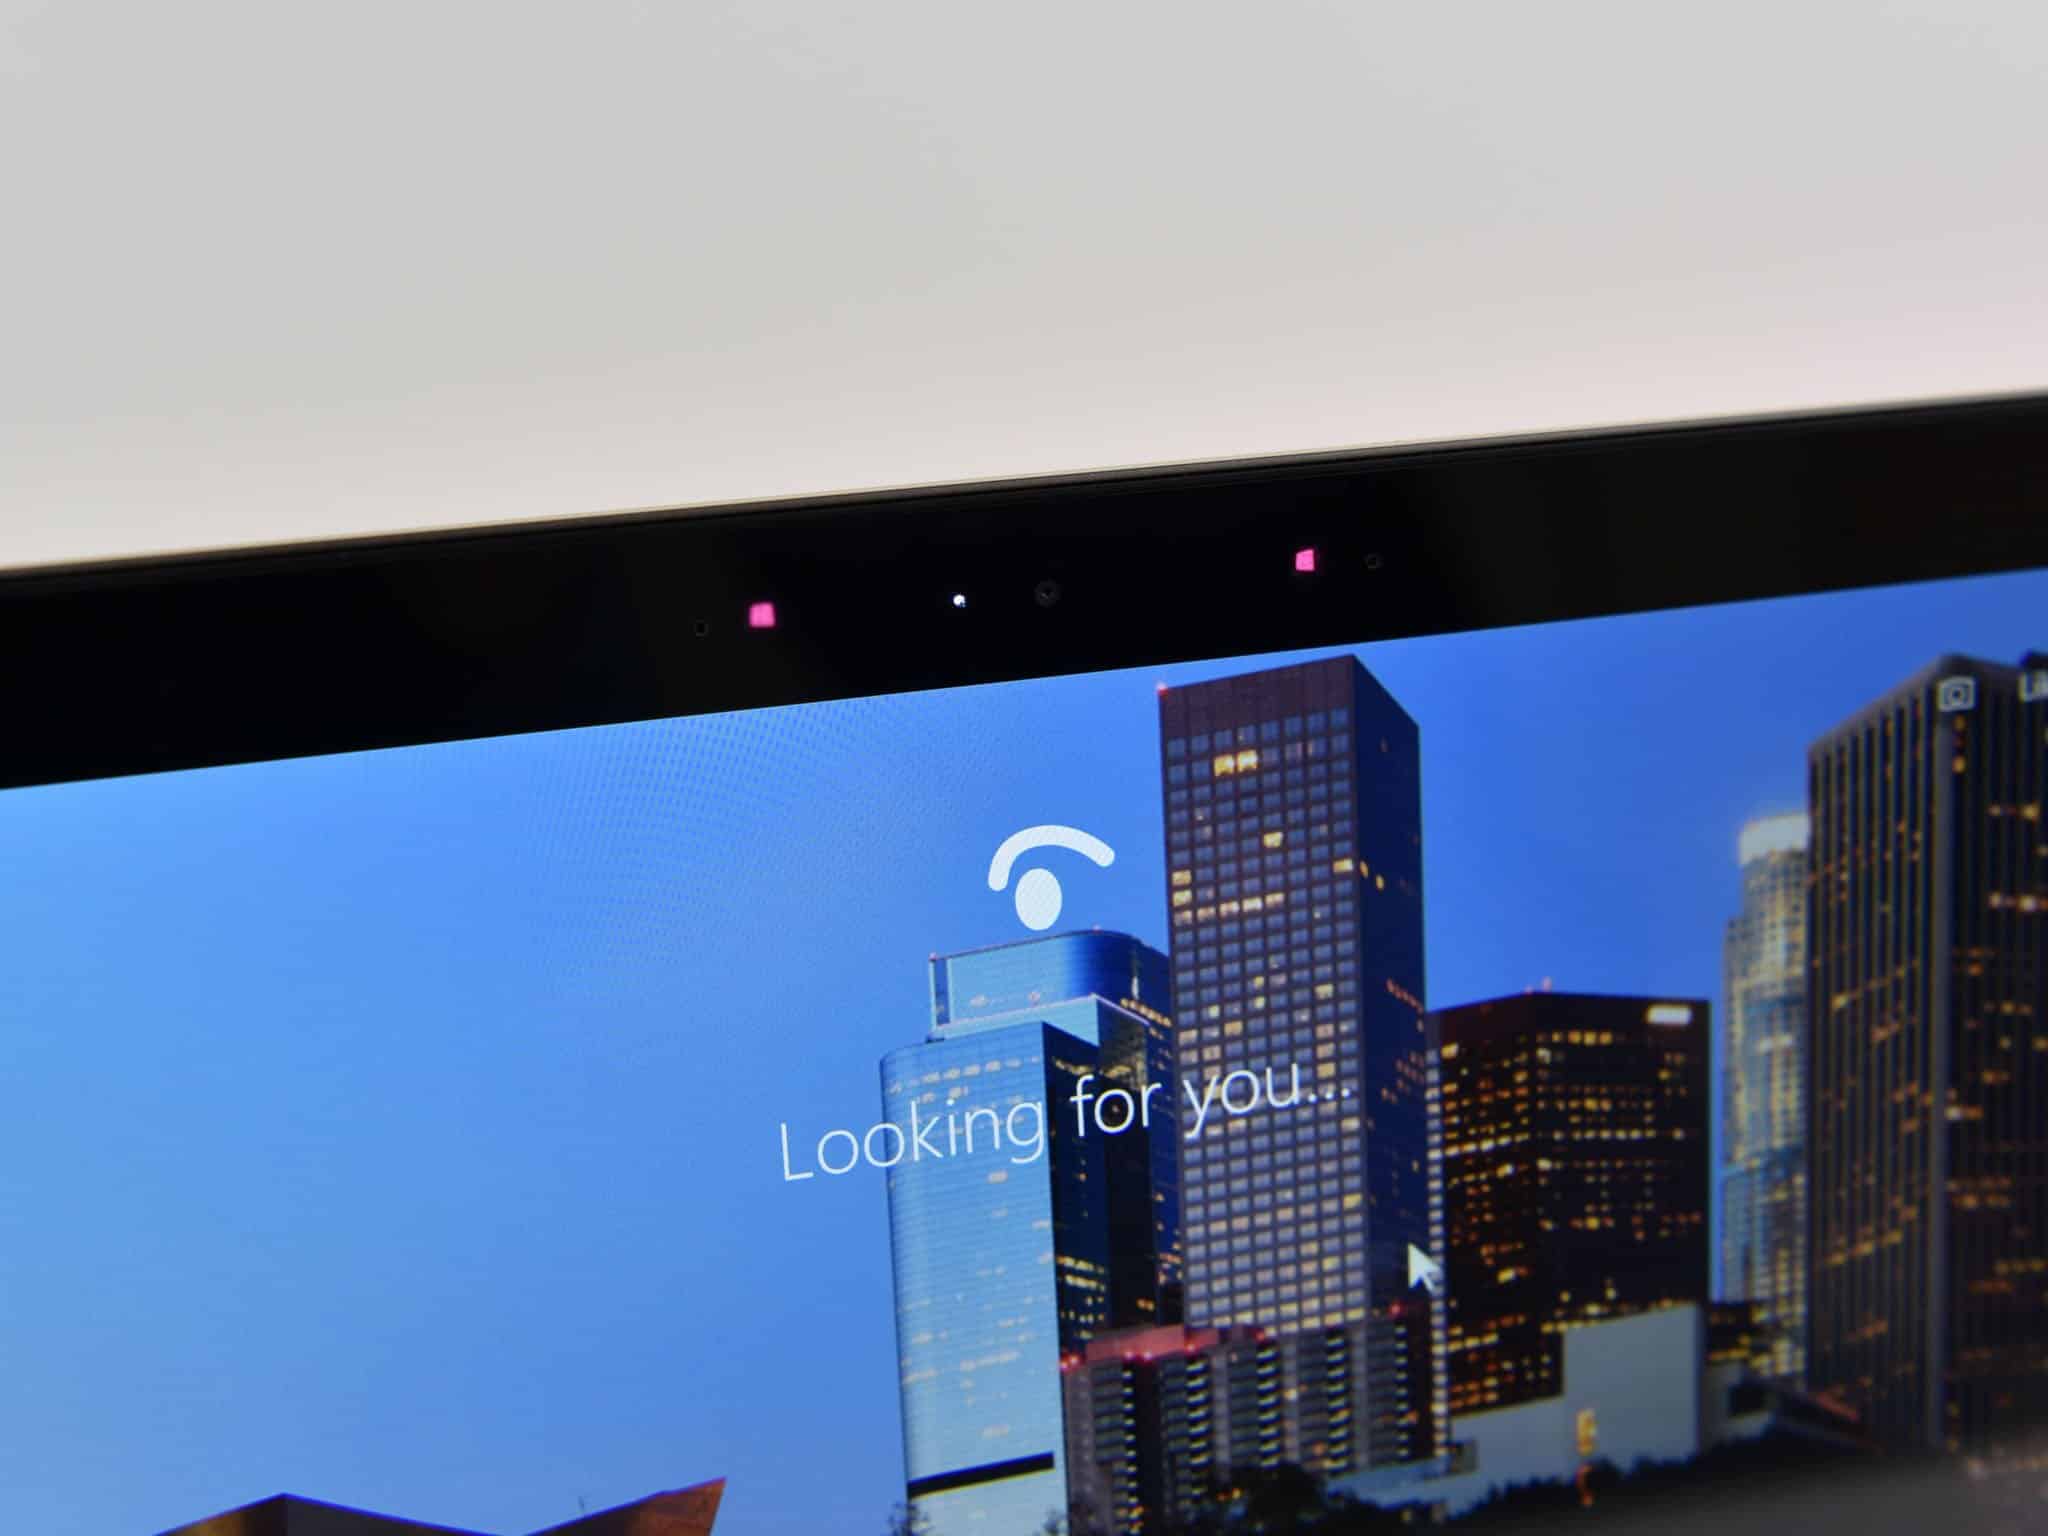
Germany's Federal Office for Information Security (BSI) published a report analyzing Windows Hello for Business, revealing significant security vulnerabilities in its biometric identification system. Conducted by ERNW, the study focused on Windows 10 Enterprise LTSC 2021, particularly facial recognition features. It found that without Enhanced Sign-in Security (ESS), the system's biometric data is inadequately protected, allowing potential attackers to modify enrollment records. This could enable an attacker to impersonate another user by associating their biometric data with a different identity. The report also noted vulnerabilities to presentation attacks, where facial masks could be used for unauthorized access. Overall, the security of biometric authentication is heavily dependent on device configuration and local access controls. The findings underscore the need for organizations to implement ESS for enhanced security.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical RCE Vulnerability in Confection WordPress Plugin (CVE-2026-115252) A critical vulnerability, CVE-2026-115252, has been identified in the Confection WordPress Cable plugin, affecting versions 0.4.0 to 0.4.7. This flaw allows unauthenticated attackers to execute arbitrary PHP code on the server by writing unmodified settings into a PHP file without proper checks. The vulnerability has…
 Critical Code Injection Vulnerability in Staggs Plugin for WordPress A critical code injection vulnerability, CVE-2026-78287, has been identified in the Staggs plugin for WordPress, affecting versions up to 3.3.0. This flaw allows unauthenticated attackers to execute arbitrary code remotely, posing severe risks to affected sites. The vulnerability stems from improper control over code…