 Yourgibraltartv
Gibraltar Government Conducts Cyber Security Tabletop Exercise Amid Ransomware Threat
Article Content

- •Around 50 participants from various sectors took part in the exercise.
- •The scenario simulated a ransomware attack affecting government IT systems.
- •The exercise aimed to test response coordination and business continuity arrangements.
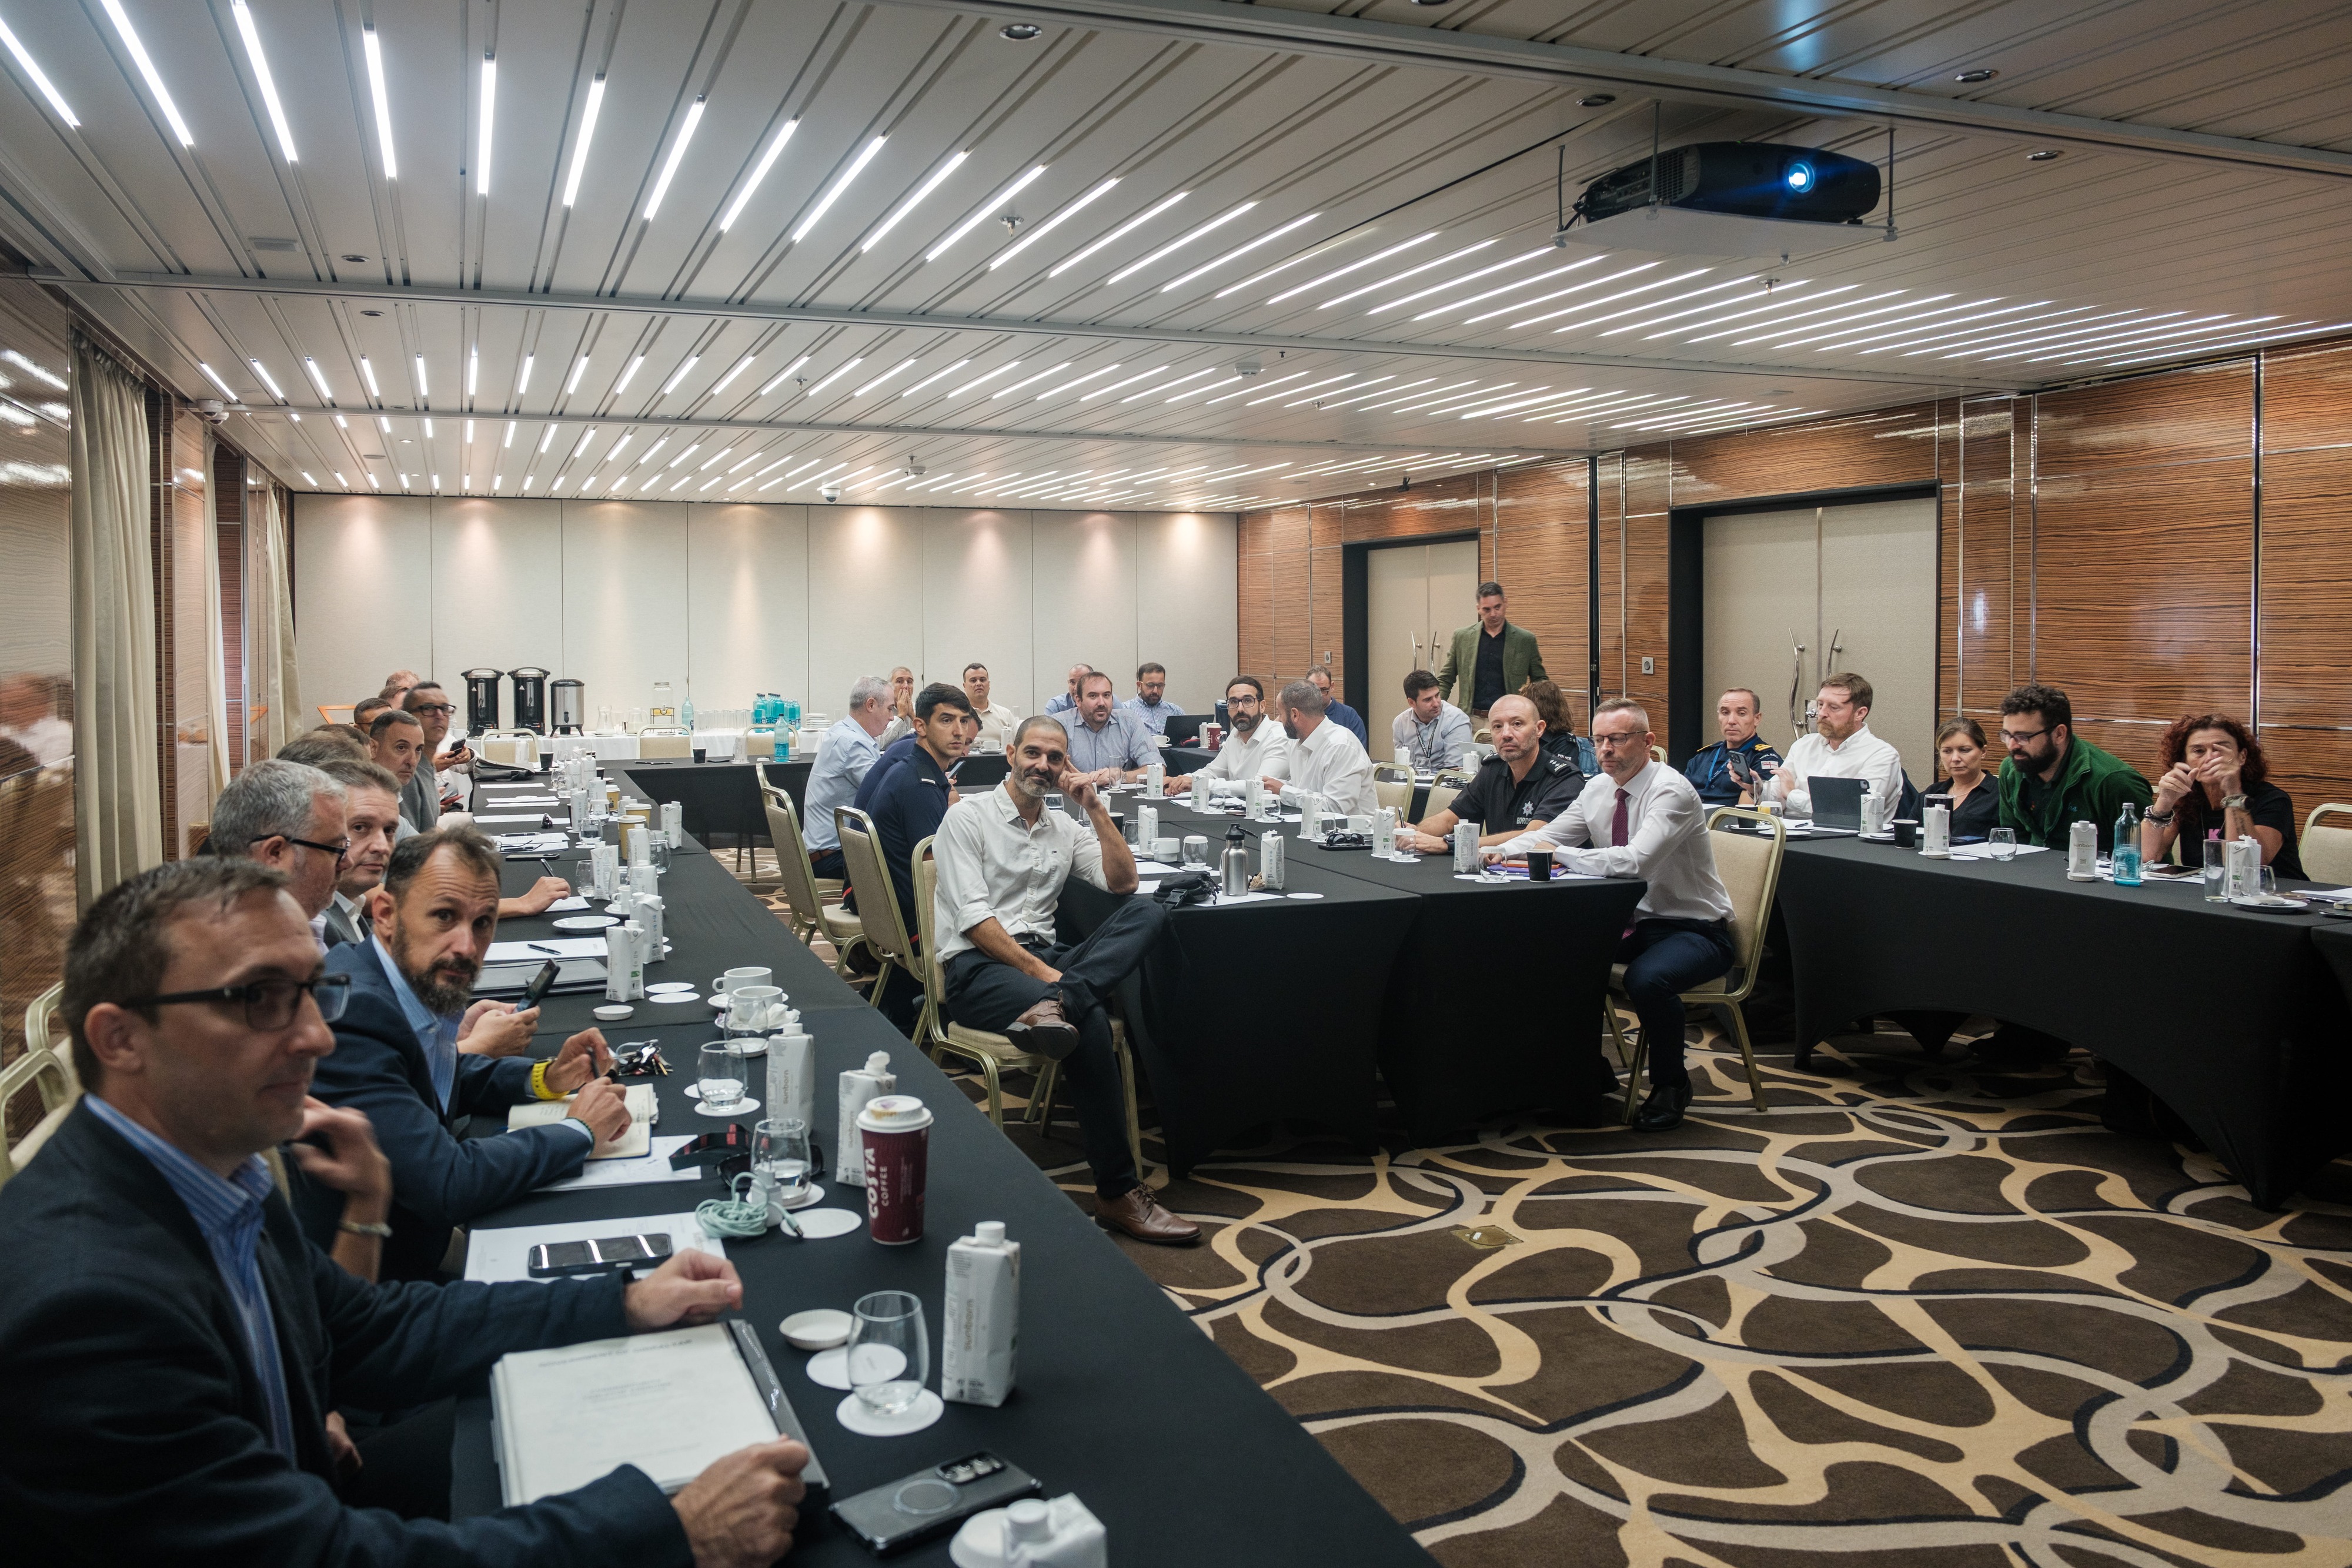
On October 14, 2026, around 50 representatives from various sectors participated in a cyber security tabletop exercise in Gibraltar, simulating a ransomware attack on government IT systems. The exercise aimed to evaluate the response of government IT teams, emergency services, and public agencies during a major cyber incident. It tested established procedures, decision-making structures, and coordination among participants, which included the Royal Gibraltar Police and Gibraltar Health Authority. The scenario highlighted the potential disruption to essential public services and the importance of maintaining business continuity. The exercise was organized by the Office of Civil Contingencies and the Cyber Division of the Information Technology & Logistics Department. The UK’s National Cyber Security Centre had previously warned about the increasing real-world consequences of cyberattacks, emphasizing the need for preparedness. This exercise reflects ongoing efforts to enhance cyber resilience within the community.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Gibraltar Health Authority in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What was the purpose of the exercise?
Who participated in the exercise?
What were the key areas tested during the exercise?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…