 github.blog
GitHub Actions Lockfiles Now Enforced to Mitigate Supply Chain Risks
Article Content

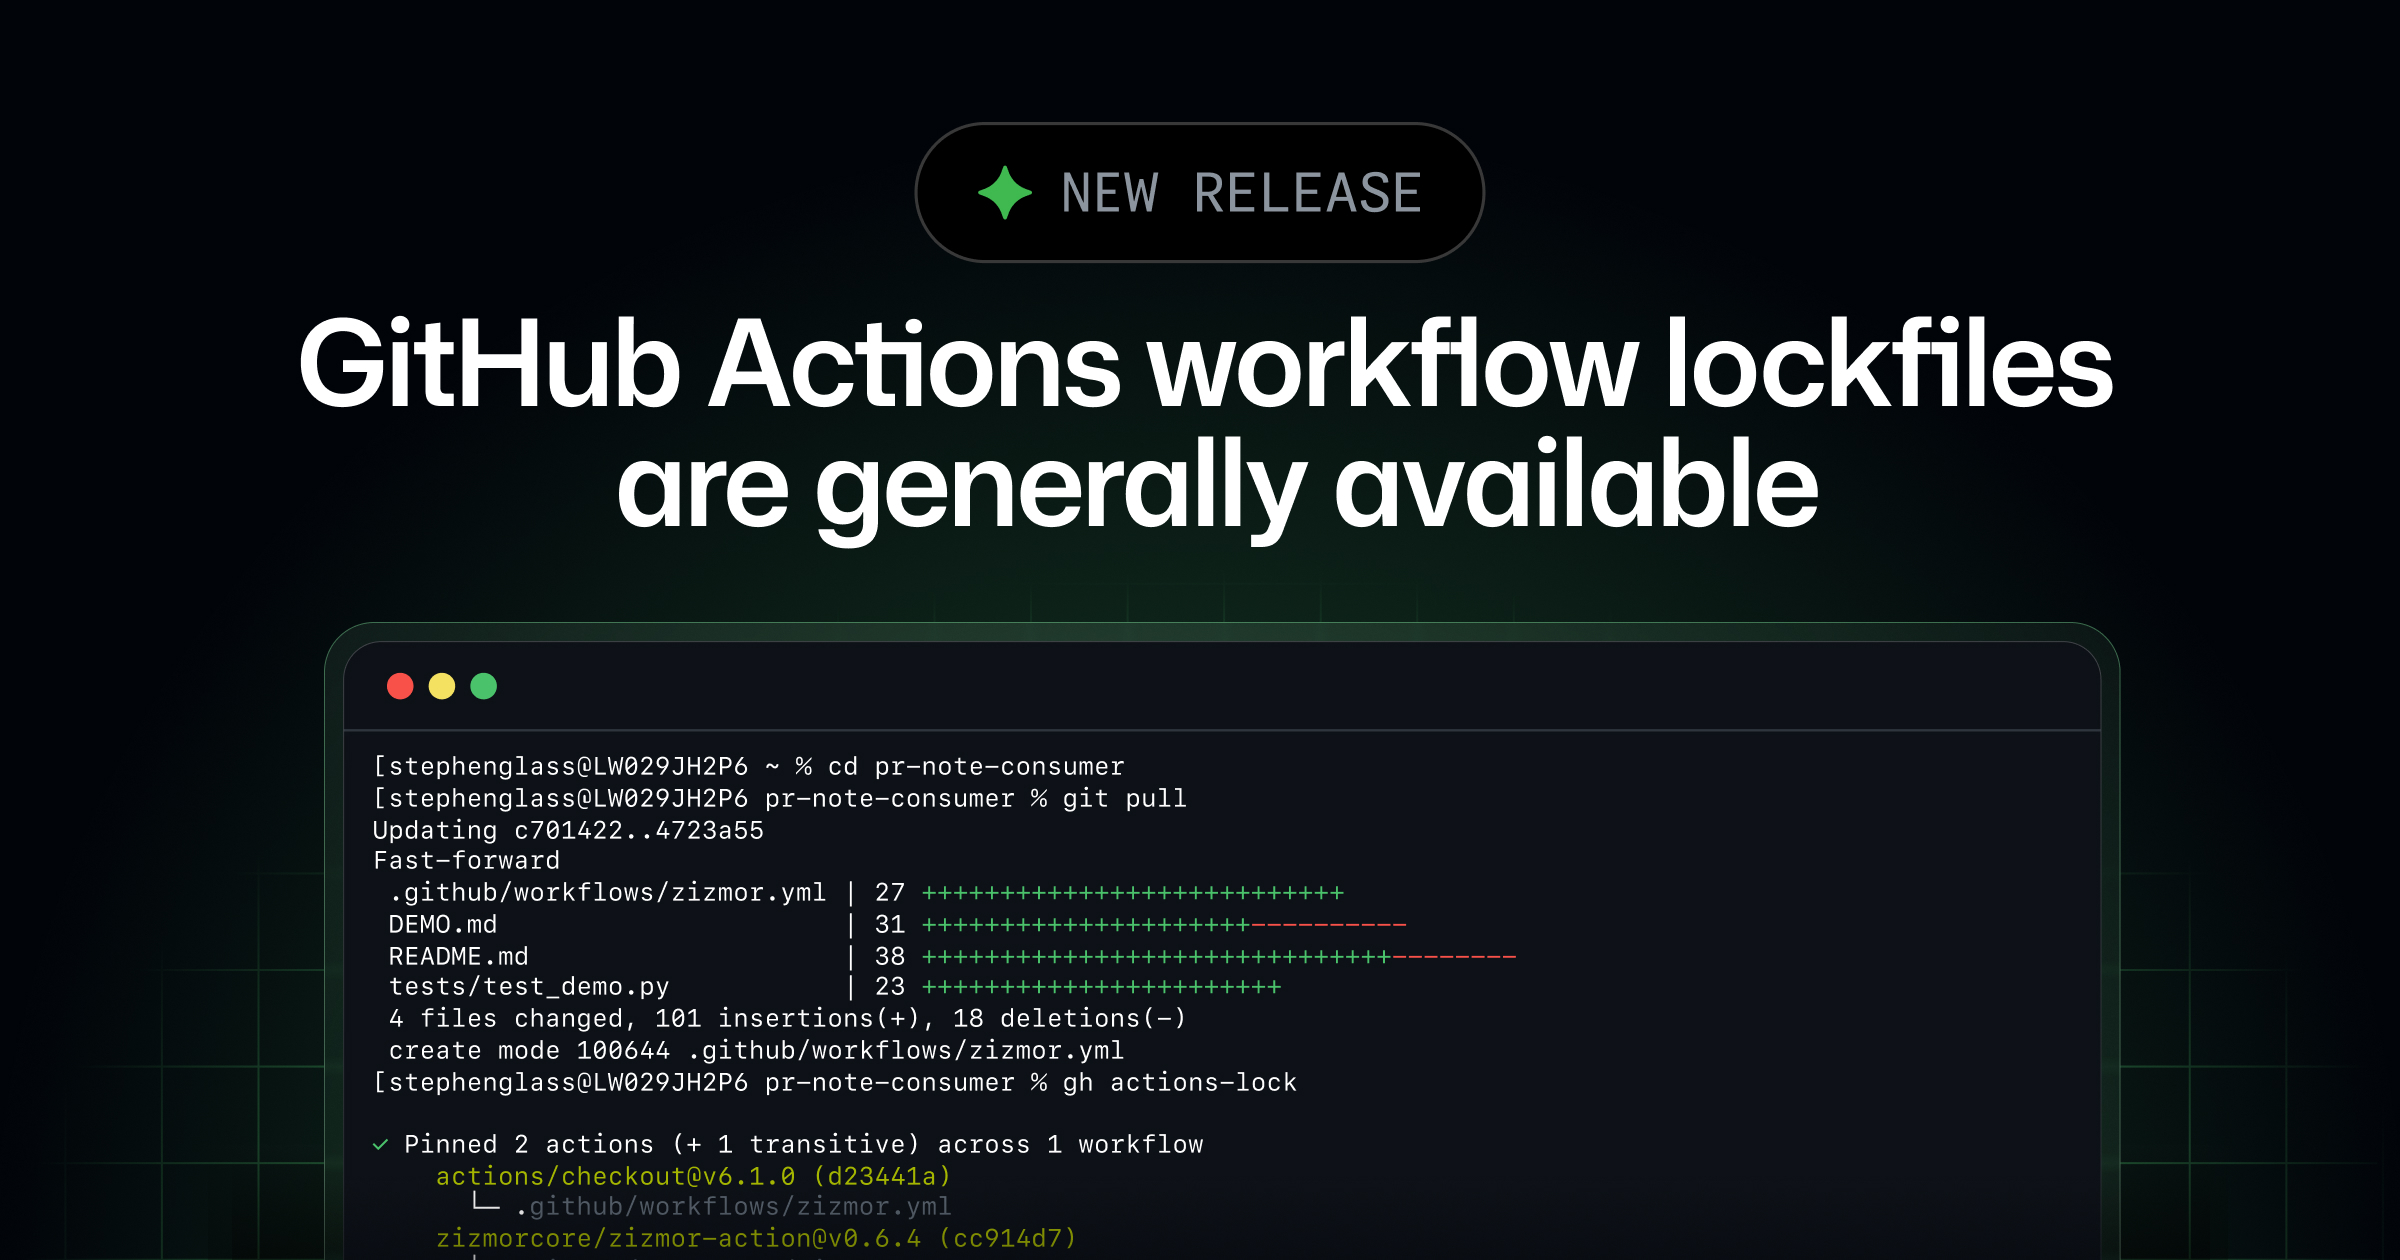
- •GitHub Actions lockfiles are now generally available to enhance security.
- •The 'gh actions-lock' CLI extension allows users to pin actions to specific commits.
- •Repository administrators can enforce lockfile policies for consistent security.
GitHub has announced the general availability of workflow dependency lockfiles, allowing users to pin actions to specific commits to prevent supply chain attacks. This feature is now accessible across various GitHub plans including Enterprise Cloud and Team. Users can utilize the 'gh actions-lock' CLI extension to create and manage lockfiles, which ensure that workflows run vetted code. The lockfiles help maintain the integrity of workflows by preventing unexpected changes in dependencies. GitHub encourages repository administrators to enforce lockfile policies to enhance security. The implementation of lockfiles is crucial as it mitigates risks associated with mutable tags that can be redirected to malicious code. The feature is designed to provide consistent and auditable assurance for developers without requiring individual teams to adopt the practice independently. As of now, there are no reports of related to this feature.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Common questions
How do I create a lockfile for my GitHub Actions?
What are the benefits of using lockfiles?
Who can enforce lockfile policies?
Continue Reading
 Critical RCE Vulnerability in Confection WordPress Plugin (CVE-2026-115252) A critical vulnerability, CVE-2026-115252, has been identified in the Confection WordPress Cable plugin, affecting versions 0.4.0 to 0.4.7. This flaw allows unauthenticated attackers to execute arbitrary PHP code on the server by writing unmodified settings into a PHP file without proper checks. The vulnerability has…
 Critical Code Injection Vulnerability in Staggs Plugin for WordPress A critical code injection vulnerability, CVE-2026-78287, has been identified in the Staggs plugin for WordPress, affecting versions up to 3.3.0. This flaw allows unauthenticated attackers to execute arbitrary code remotely, posing severe risks to affected sites. The vulnerability stems from improper control over code…