 Gbhackers
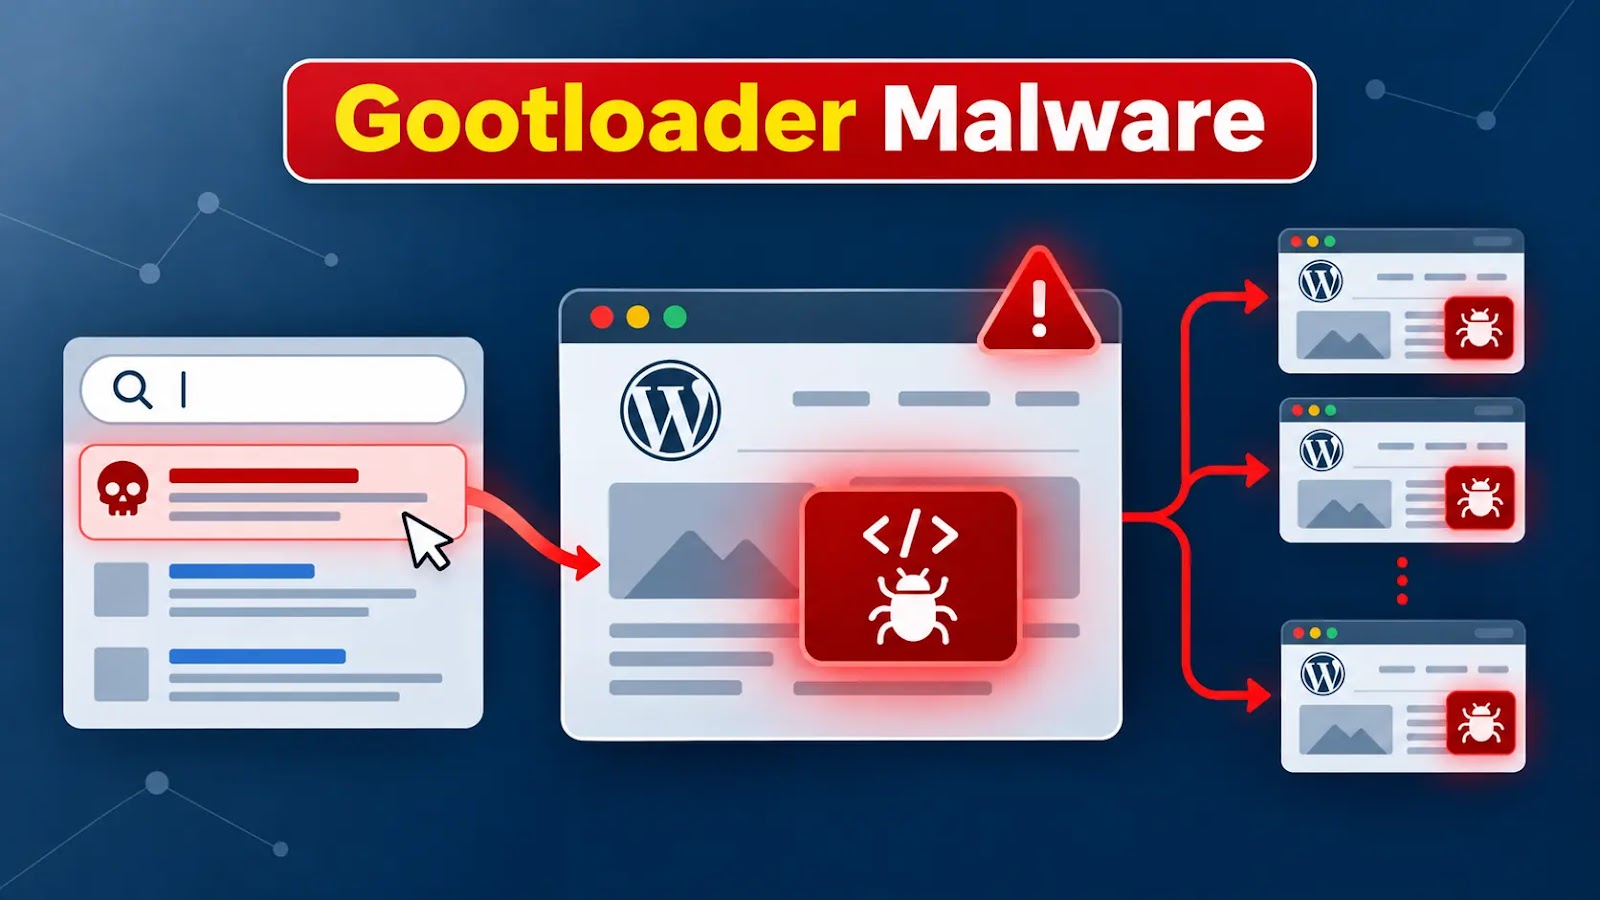
Gootloader Malware Infects 1,000+ WordPress Sites via SEO Poisoning
Article Content

- •Over 1,000 WordPress sites compromised to spread Gootloader malware.
- •Targets include legal professionals searching for specific documents.
- •The operation has led to over $28 million in ransomware payments.
Cybercriminals have compromised over 1,000 WordPress websites to distribute Gootloader malware, targeting legal professionals with manipulated search results. The FBI warns that these attacks exploit SEO poisoning to trick users into downloading malicious JavaScript files disguised as legal documents. The operation has reportedly resulted in over $28 million in ransomware payments. Attackers utilize stolen credentials and exposed components to maintain control over 216 domains. Malicious content is selectively served based on visitor characteristics, enhancing the likelihood of infection. The Gootloader malware establishes a foothold for further intrusions once executed. The campaign has evolved to include advanced techniques such as geofencing and traffic distribution. IBM X-Force has linked this activity to the Hive0127 group, also known as UNC2565.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Hive0127 and GootBot in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Who is primarily targeted by these attacks?
What is the method of infection?
What should organizations do to protect themselves?
Continue Reading
 Critical Code Injection Vulnerability in Staggs Plugin for WordPress A critical code injection vulnerability, CVE-2026-78287, has been identified in the Staggs plugin for WordPress, affecting versions up to 3.3.0. This flaw allows unauthenticated attackers to execute arbitrary code remotely, posing severe risks to affected sites. The vulnerability stems from improper control over code…
 Lazarus Group Targets 30 South Korean Servers Using PHP Vulnerabilities North Korea-linked Lazarus Group has targeted 30 servers in South Korea as part of a larger cyber operation involving 581 servers across 10 countries. The attacks exploit two critical remote code execution vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619), allowing unauthorized server command execution. The…