 nwr.eqs-cockpit.com
Graylog Launches Verascend Incident System to Combat AI-Driven Threats
Article Content

- •Graylog v7.2 introduces the Verascend Incident System for improved threat detection.
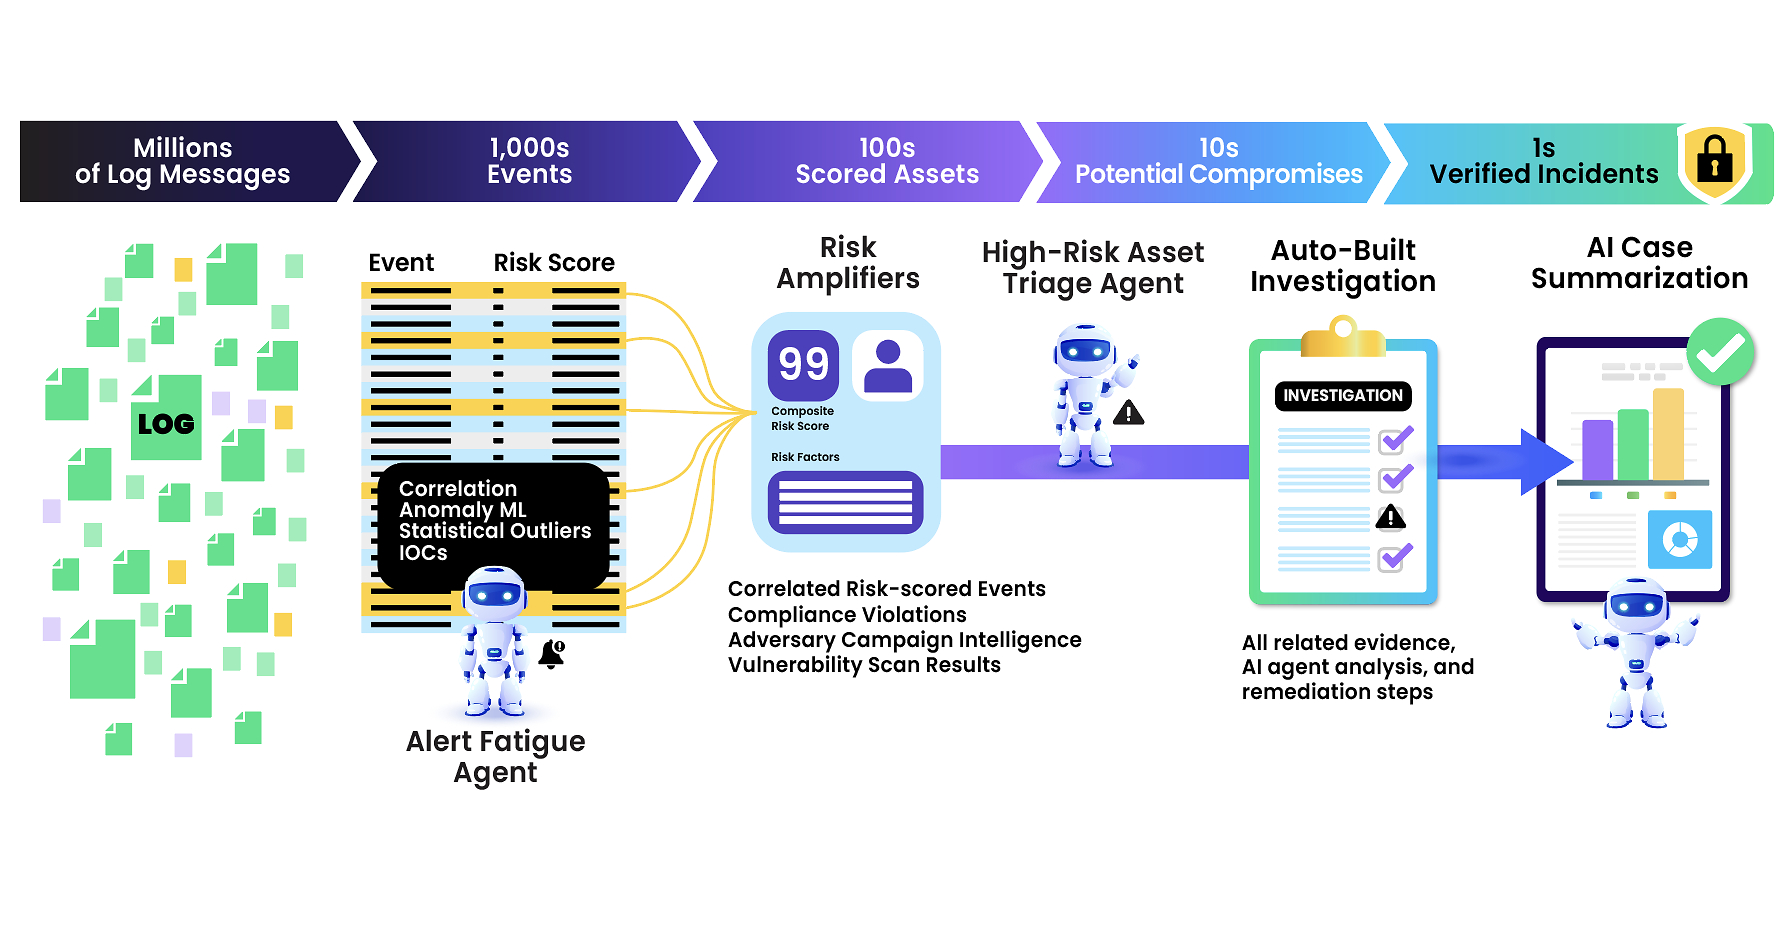
- •The system prioritizes verified incidents, reducing alert fatigue for security analysts.
- •ENISA reports increased AI usage by ransomware operators, highlighting the urgency for updated tools.
On October 13, 2026, Graylog launched the Verascend Incident System with Graylog v7.2, aimed at enhancing security teams' ability to detect and respond to threats. The system prioritizes verified incidents over individual alerts by correlating risk-scored events. This launch coincides with findings from ENISA, indicating that ransomware operators are increasingly using AI to expedite attacks, potentially leading to more sophisticated threats through 2026. Verascend integrates various detection capabilities, including Detection Chains and Sigma rules, alongside AI-assisted triage and reporting. The new version also provides enhanced visibility into pipeline performance and system health, allowing administrators to manage resources effectively. Graylog v7.2 is available immediately and is included in existing licenses for Graylog Security. The system is particularly beneficial for European organizations, as it supports local data residency with OVH and Secunet SysEleven.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What does the Verascend Incident System do?
How does this relate to AI in cybersecurity?
Is Verascend available for all users?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…