 insider-gaming.com
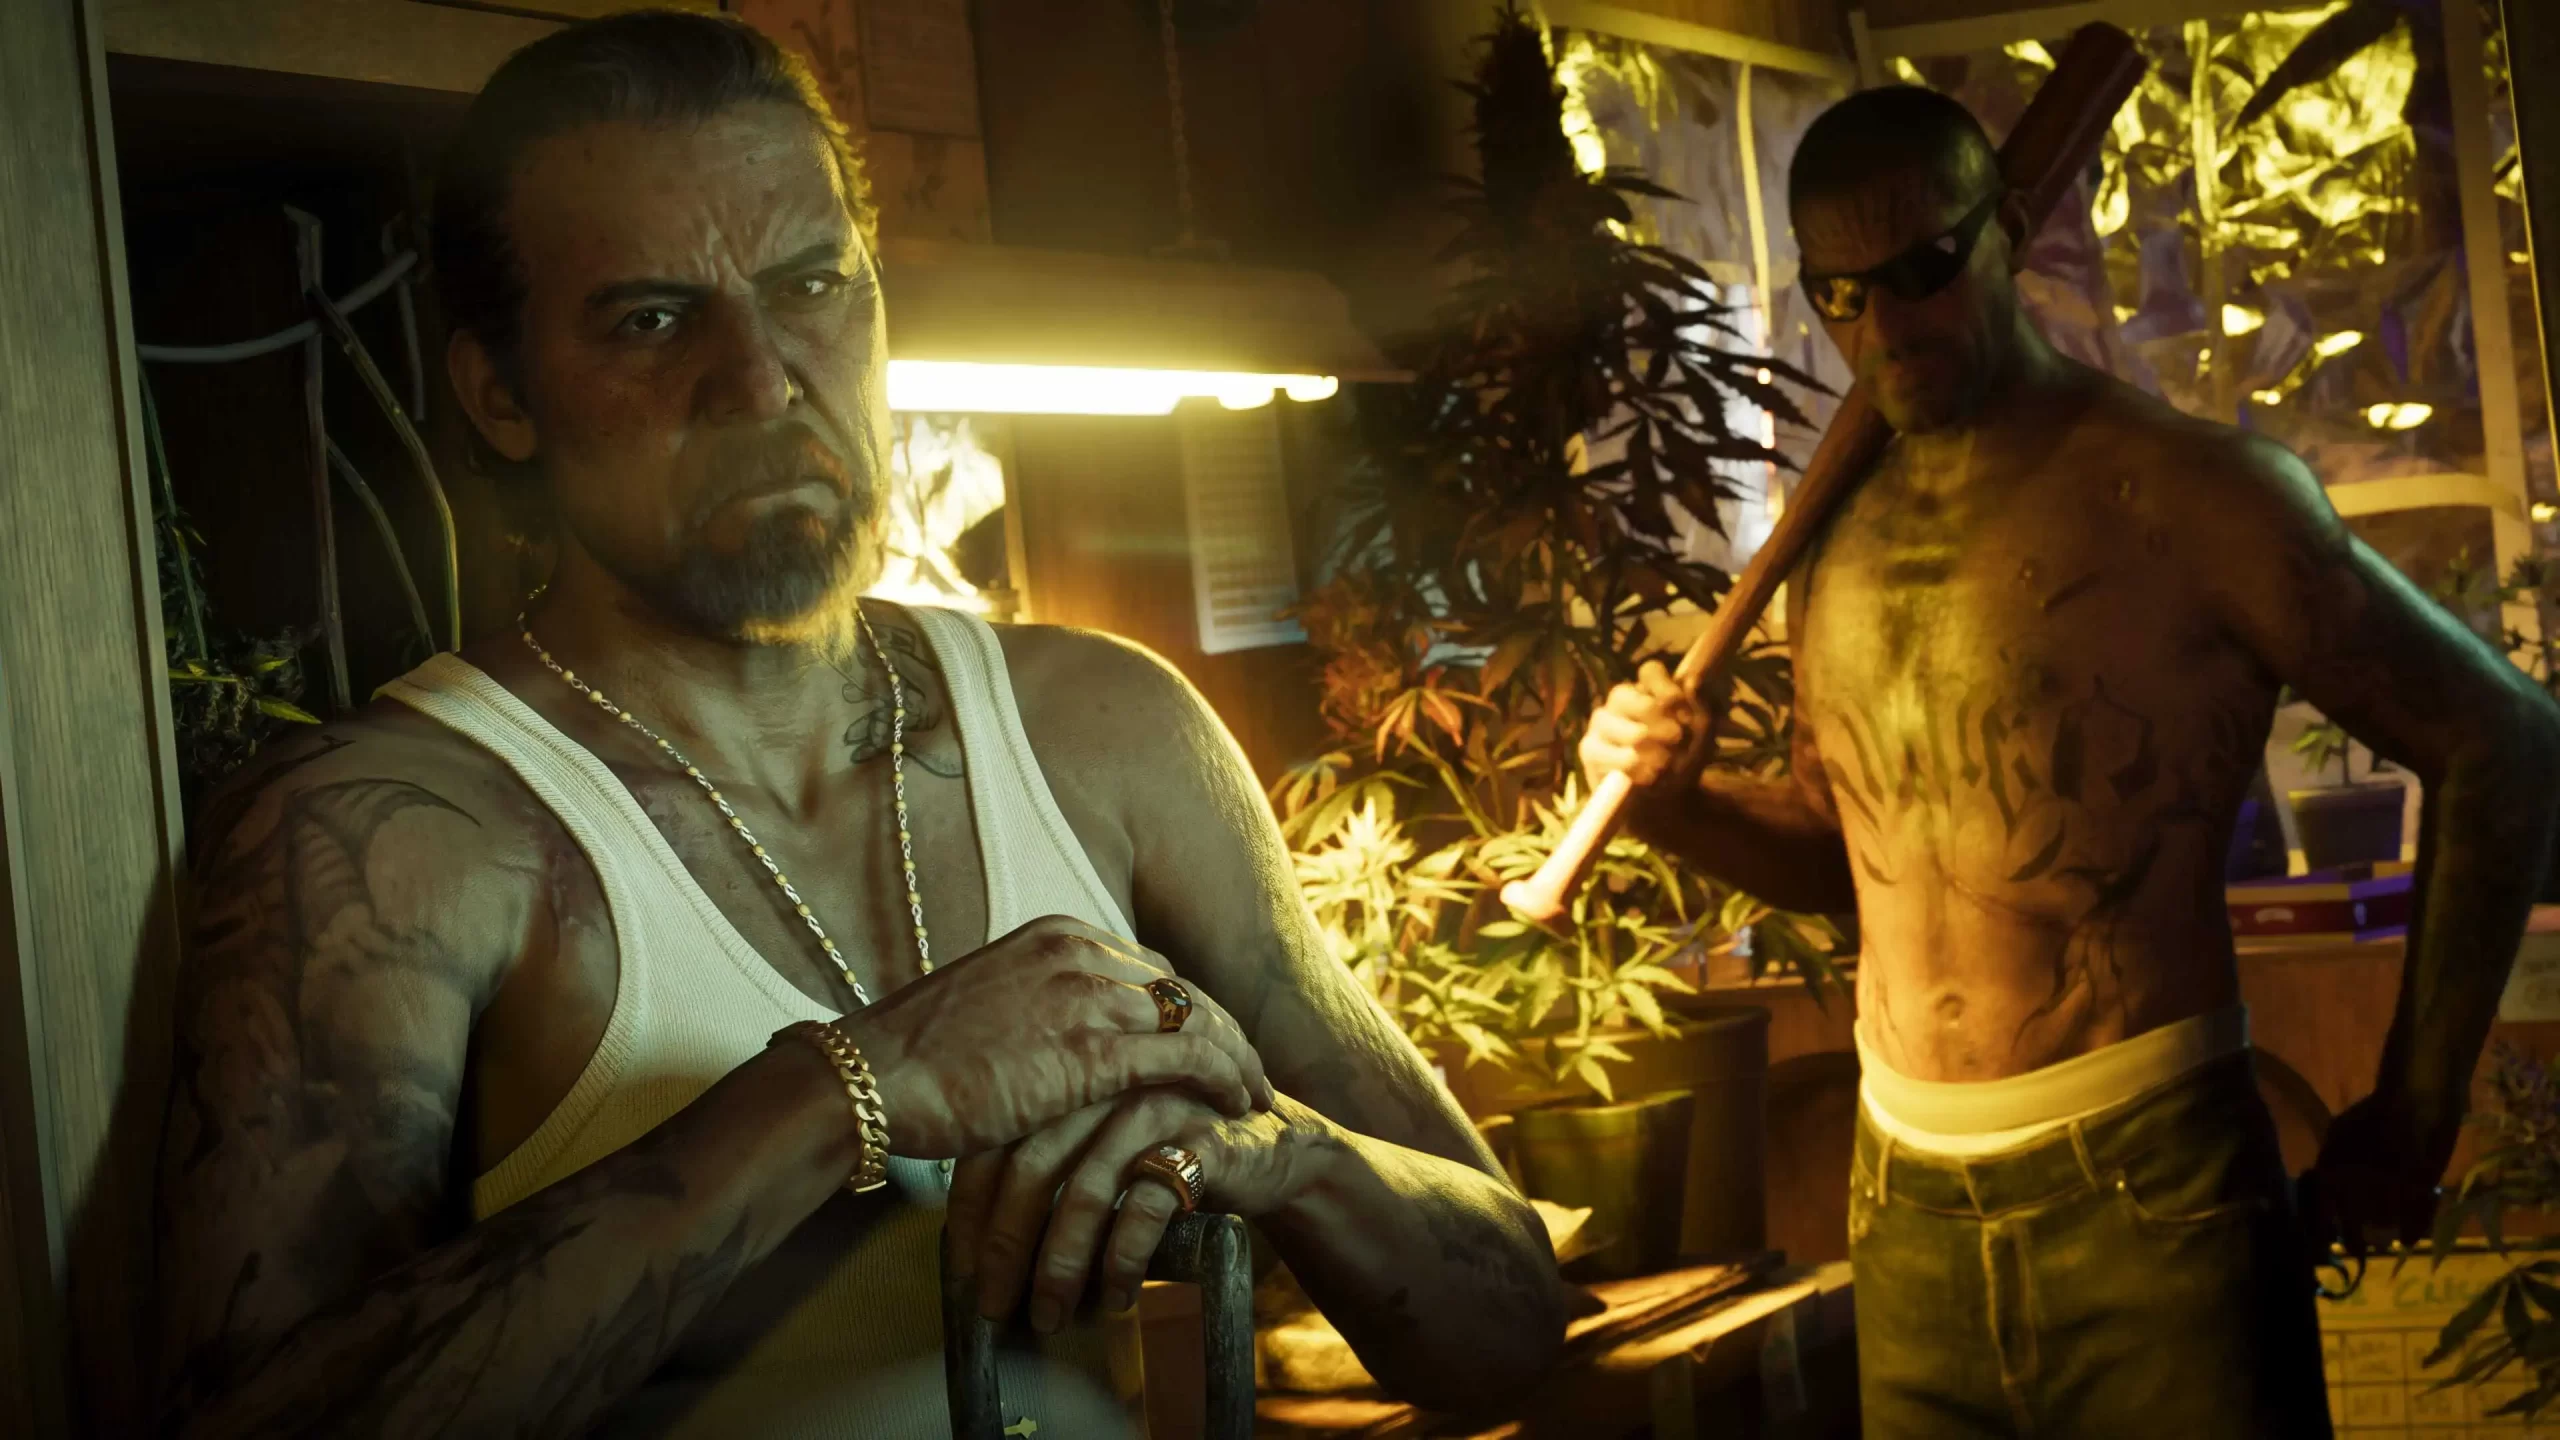
GTA 6 Leaker Threatens Full Playable Build Release
Article Content

- •Cyberleek threatens to release a full playable build of GTA 6 if conditions are met.
- •Take-Two Interactive has filed subpoenas against several companies to identify the leaker.
- •The authenticity of the claimed complete build remains unverified, with prior leaks being from older builds.
A hacker known as Cyberleek has threatened to release a complete, playable build of Grand Theft Auto 6, including the full story mode and ending credits, if their cryptocurrency token reaches a $30 million market cap or if Take-Two Interactive publicly apologizes for not releasing a physical version of the game. The game is set to launch on November 19, 2026. Recent leaks have included over an hour of gameplay footage, but the authenticity of a complete build remains unverified. Take-Two has filed subpoenas against Microsoft and Discord to identify the leaker, following earlier leaks that included gameplay clips and map screenshots. Cyberleek's threats come after a series of gameplay leaks that have raised concerns about malware risks associated with fake builds circulating online. The situation is ongoing, with no official comment from Rockstar Games or Take-Two on the latest threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Microsoft in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What are the conditions for the full build release?
Is there a risk of malware with GTA 6 builds?
What has Take-Two done in response to the leaks?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…