 www.newsweek.com
Cybersecurity Expert Warns Against Posting House Key Photos Online
Article Content
Browse articles 
- •Posting photos of house keys on social media can lead to home break-ins.
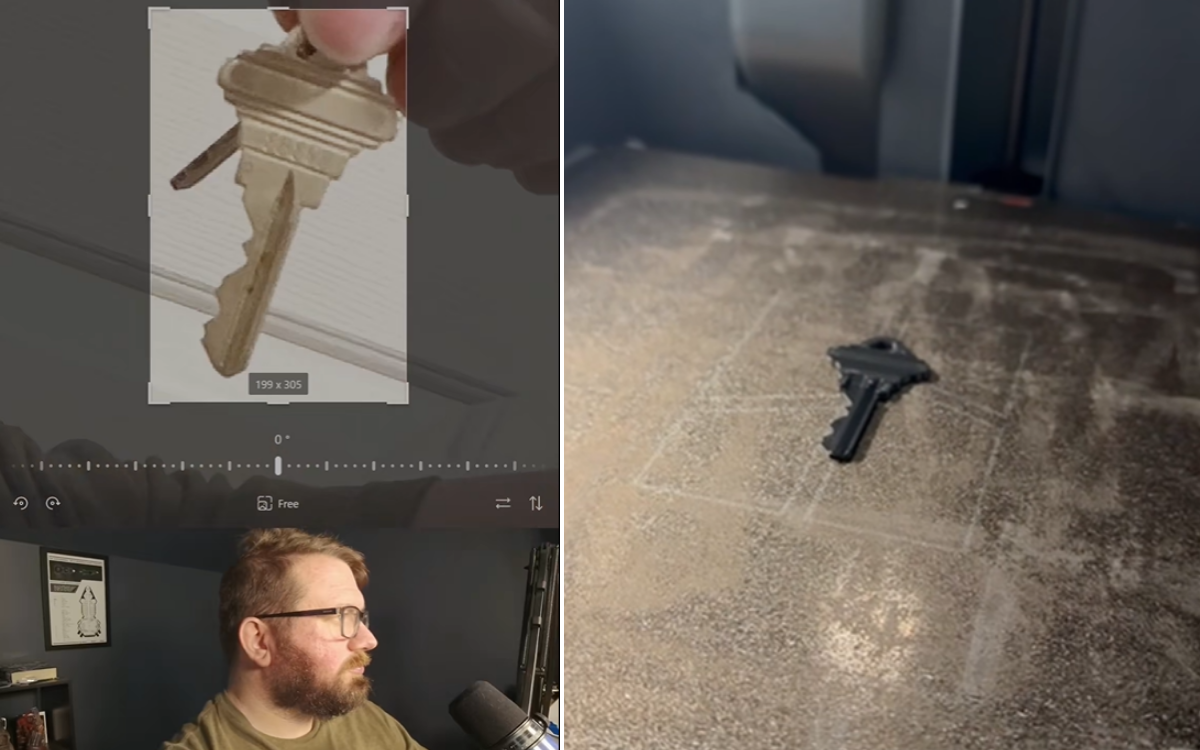
- •Evan Ottinger demonstrated key replication using 3D printing from a photo.
- •The tools and methods used for key replication are widely accessible.
Evan Ottinger, a cybersecurity expert, warns that posting photos of house keys on social media can lead to home break-ins. He demonstrated how hackers can use images of keys to create replicas using 3D printing technology. Ottinger's video, which has over 1.3 million views, shows him successfully replicating a key from a selfie. The process involves using key-decoding overlays and CAD tools to generate a digital model of the key. This method is accessible to anyone with the right tools, raising concerns about personal security. The incident highlights the risks associated with sharing personal information online, especially for new homeowners.
Ask AI about this cluster
Answers cite the sources they use
Updated 120d ago How this analysis works
Timeline
2024-01-01
Ottinger attends Red Team Alliance event
Evan Ottinger learned key replication techniques from expert Deviant Ollam, focusing on covert entry methods.
Newsweek2026-07-10
Ottinger's TikTok video goes viral
Evan Ottinger's video demonstrating key replication from a photo reached over 1.3 million views, alarming viewers about security risks.
Dailymail2026-07-11
Newsweek article published
Newsweek reported on Ottinger's warning about the dangers of posting key photos online, emphasizing the ease of key replication.
NewsweekMore articles in this cluster (6)
Continue Reading
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…
 GitLab Issues Emergency Patch for Critical RCE Vulnerability GitLab has released emergency patches for a critical remote code execution vulnerability, CVE-2026-97229, affecting its Community and Enterprise Editions. This flaw, stemming from an integer overflow in the CI/CD regular expression compiler, allows unauthenticated attackers to execute arbitrary code via specially…