 Mezha
Suno AI Music Startup Hacked, Exposing Massive Data Scraping Practices
Article Content

- •Suno's source code leak reveals unauthorized scraping of millions of songs from major platforms.
- •The breach was executed via a supply chain attack, compromising employee credentials.
- •Suno faces heightened legal risks amid ongoing copyright infringement lawsuits from record labels.
Suno, an AI music generation startup, was hacked, revealing unauthorized scraping of music data from platforms like YouTube Music, Deezer, and Genius. The breach occurred through a supply chain attack that compromised employee credentials, allowing access to Suno's source code and customer data. The leaked files show that Suno collected over 2 million music clips and tens of thousands of hours of audio from various sources, raising serious legal and ethical concerns amid ongoing copyright infringement lawsuits. Suno has faced criticism for not notifying customers about the breach, which included sensitive information like email addresses and partial credit card details. The incident highlights the growing scrutiny on AI companies regarding their data collection practices and the implications for copyright law. Suno claims the data used was publicly available and argues its practices fall under fair use, but the leaked evidence contradicts this position.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (30)
Following this threat?
Track Shai-hulud and Suno in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
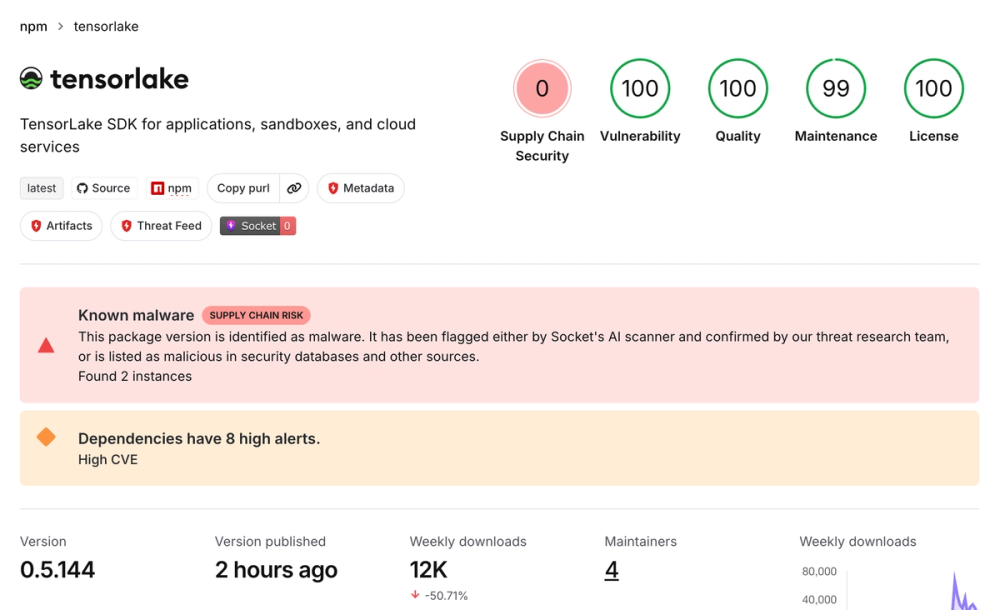 Tensorlake npm Package Compromised by Shai-Hulud Worm On October 8, 2026, the Tensorlake npm package version 0.5.144 was compromised, delivering a credential-stealing worm known as Shai-Hulud. The malware, which was published through a compromised maintainer account, executes a preinstall hook that runs an obfuscated loader to harvest credentials from local files and CI…
 Cisco Email Bug Exploited as Zero-Day by Unknown Actors A zero-day vulnerability in Cisco's email system has been by unknown criminals. The flaw, described as a 'make-me-root' bug, allows attackers to gain root access via email. Cisco has not disclosed specific details about the vulnerability or the affected systems. The exploit is reportedly being used in the wild…