 Newsbytes.Ph
Hackers Compromise DMW Network Amid Government Cybersecurity Investigations
Article Content

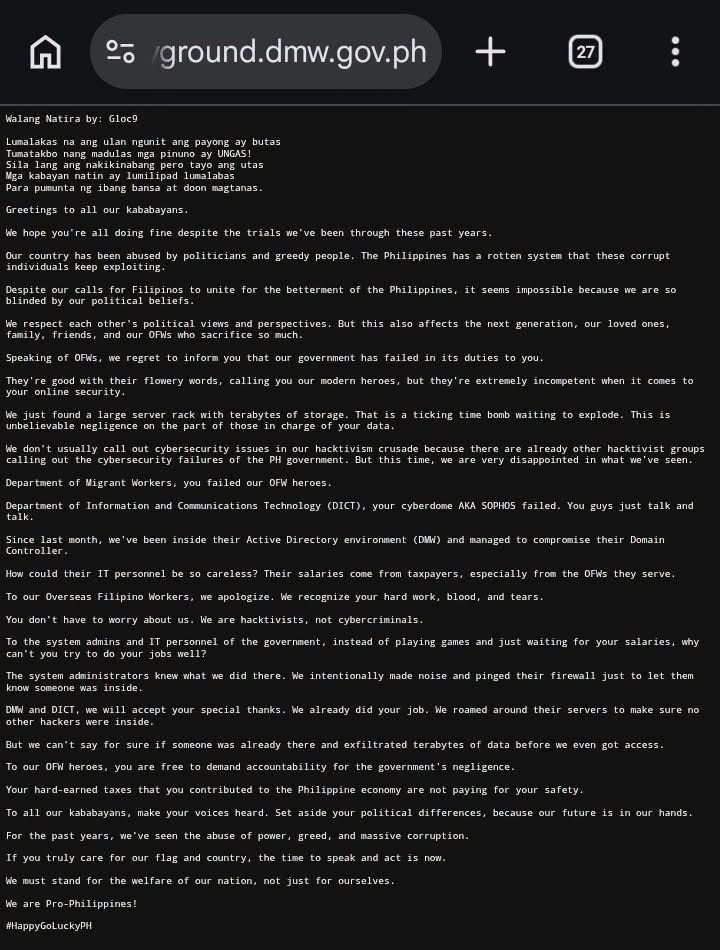
- •HappyGoLuckyPH claims access to DMW systems for over a month.
- •No sensitive data or PII confirmed compromised in the DOLE incident.
- •DICT is actively investigating multiple cyber threats across government agencies.
The Department of Information and Communications Technology (DICT) is investigating unauthorized access to the Department of Migrant Workers (DMW) website and a web defacement incident involving the Department of Labor and Employment (DOLE). The hacktivist group HappyGoLuckyPH claimed responsibility for the DMW breach, asserting they had access for over a month, potentially compromising sensitive data. The DICT confirmed that no Personally Identifiable Information (PII) was compromised in the DOLE incident. As a precaution, affected web services have been taken offline while forensic investigations are ongoing. The DICT is also addressing a false report of a ransomware attack against the Philippine Ports Authority (PPA), confirming no evidence of a breach. The agency is coordinating with affected departments to enhance security measures and restore services. Further updates will be provided as investigations progress.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Department Of Information And Communications Technology in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Korean-speaking Hackers Target PHP Vulnerabilities in Global Campaign A cybersecurity report from Cyfirma reveals that attackers, possibly linked to North Korea's Lazarus group, are preparing to exploit critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619). These vulnerabilities allow unauthenticated remote code execution, posing a significant threat to government…