 Securityaffairs.Co
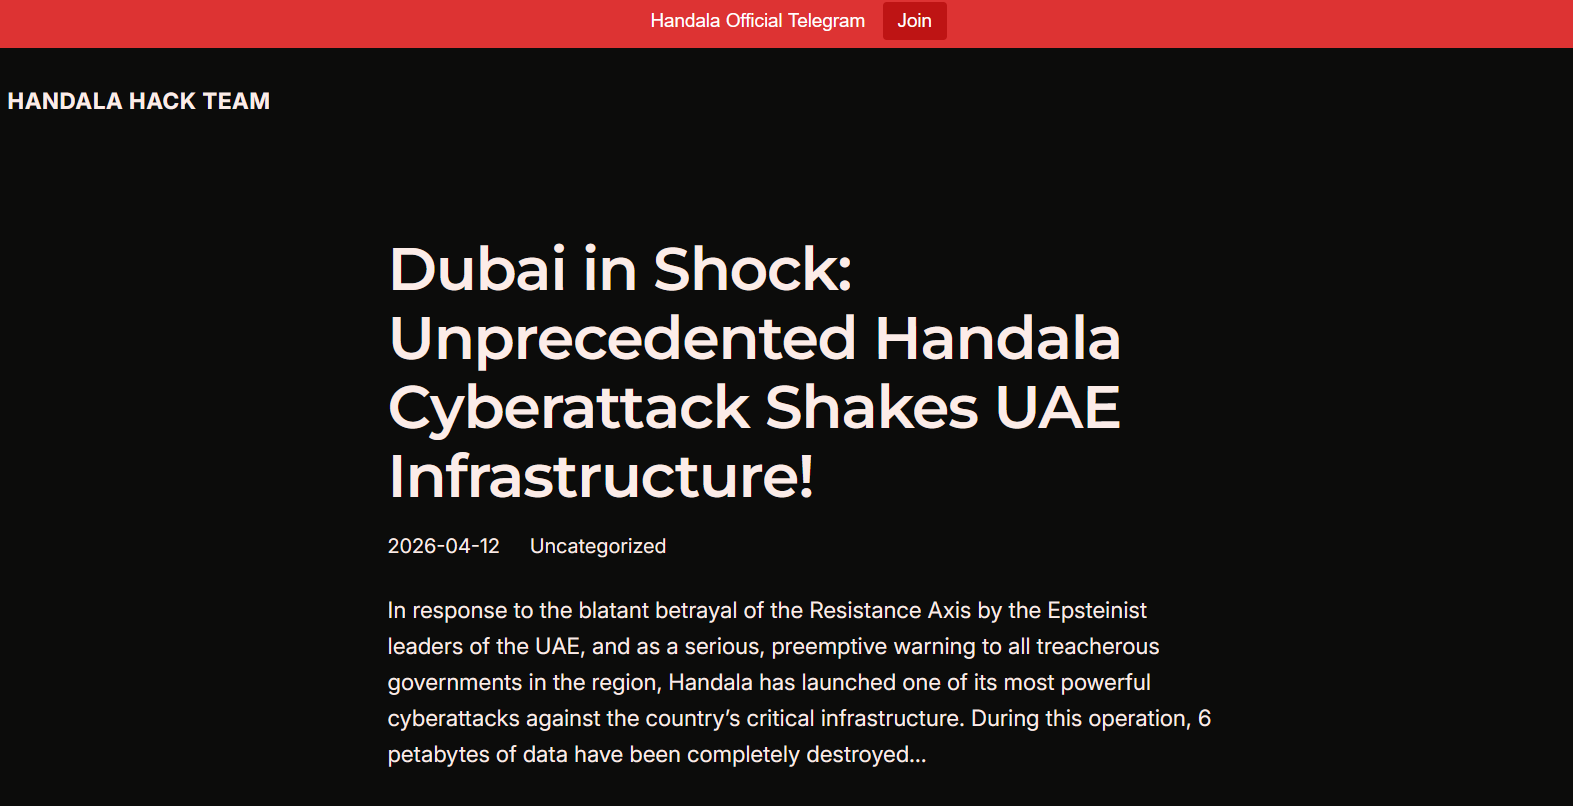
Handala Group Launches Major Cyberattack on UAE Critical Infrastructure
Article Content

- •Handala hacked UAE's critical infrastructure, destroying 6 petabytes of data.
- •149 terabytes of sensitive documents were extracted from key Dubai institutions.
- •The attack signifies vulnerabilities in UAE's cyber defenses against advanced threats.
The Handala hacking group executed a significant cyberattack on April 12, 2026, targeting critical infrastructure in the United Arab Emirates. The attack focused on three key institutions: the Dubai Courts Authority, the Dubai Land Authority, and the Dubai Roads and Transport Authority. During the operation, Handala claimed to have destroyed 6 petabytes of data and extracted 149 terabytes of sensitive documents. The group stated that this operation was a response to perceived betrayals by UAE leaders and serves as a warning to other regional governments. The attack has led to widespread disruptions within Dubai, impacting the operational integrity of the targeted institutions. Handala emphasized that they remain poised for further actions against any future perceived traitorous activities. This incident highlights vulnerabilities in the UAE's cyber defenses, raising concerns about the effectiveness of their security measures against sophisticated attacks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (15)
Following this threat?
Track Handala and Dubai Courts in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…