 Theguardian
Russian-Speaking Handler Directs Arson Attacks on UK Prime Minister's Properties
Article Content

- •Two men were convicted of arson linked to UK Prime Minister Keir Starmer's properties.
- •The attacks were directed by a Russian-speaking handler known as 'El Money' via Telegram.
- •Evidence indicates the operation is part of a broader Russian campaign to destabilize the UK.
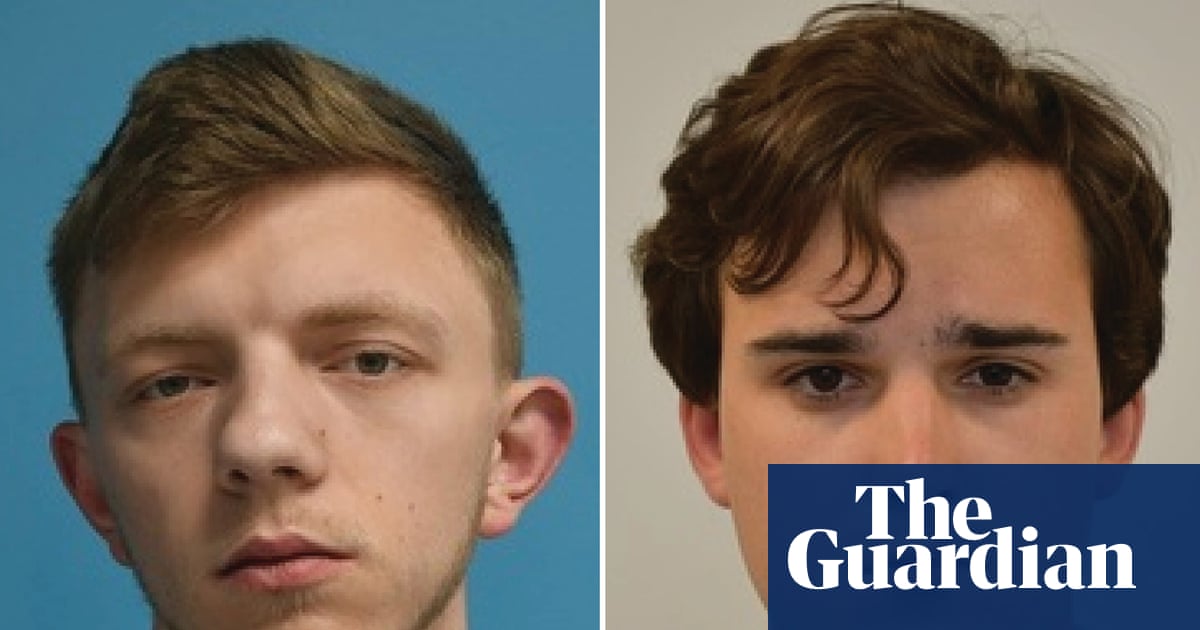
Two men, Roman Lavrynovych and Stanislav Carpiuc, were convicted of arson targeting properties linked to UK Prime Minister Keir Starmer. The attacks, occurring in May 2025, were allegedly orchestrated by a Russian-speaking handler known as 'El Money' via Telegram. Evidence suggests that Lavrynovych was recruited for escalating criminal tasks, culminating in the arson of a car and two houses associated with Starmer. The operation is part of a broader Russian disinformation and sabotage campaign aimed at destabilizing the UK. The investigation revealed that Lavrynovych had been promised payment in cryptocurrency for his actions. The Russian embassy has denied any involvement in the attacks. The case highlights the ongoing threats posed by Russian intelligence operations in Europe, particularly against nations supporting Ukraine.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (13)
Following this threat?
Track DHL in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…