 objective-see.org
Heartbreaker Ransomware Targets macOS Users with Self-Rebuilding Capabilities
Article Content

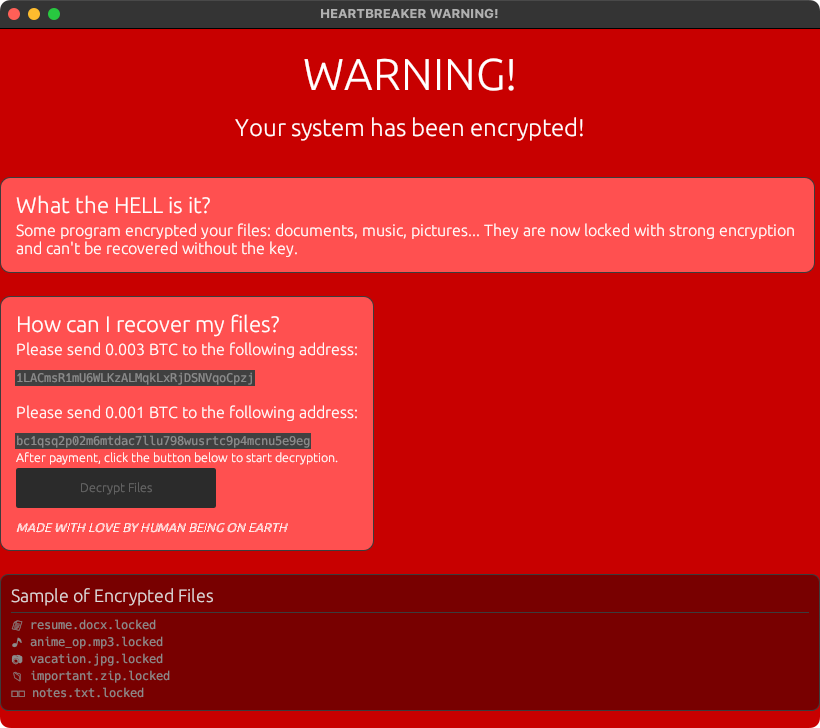
- •Heartbreaker ransomware targets macOS users, encrypting files in the Downloads folder.
- •The ransomware can rebuild itself, but uses a hardcoded AES key for encryption.
- •Research indicates that Heartbreaker is unlikely to pose a significant threat currently.
Heartbreaker is a Rust-based macOS ransomware sample that was uploaded to VirusTotal in May 2025 and remains undetected by antivirus engines. It encrypts files in the user's Downloads folder and attempts to persist by setting up a LaunchAgent. The ransomware can rebuild itself by randomizing its source code and recompiling, but it uses a hardcoded AES key, allowing for potential file recovery. Researcher Patrick Wardle believes the threat is limited due to its reliance on an outdated Rust framework. The ISO/IEC has also published a standard aimed at mitigating AI threats, highlighting the evolving landscape of cybersecurity. Current assessments suggest Heartbreaker is not a major threat at this time.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track APT28 and Heartbreaker in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How does Heartbreaker operate?
Is there a way to recover files encrypted by Heartbreaker?
What should macOS users do to protect against Heartbreaker?
Continue Reading
 APT28 Targets NATO Defense Firms with New Hookedge Backdoor The Russian espionage group APT28, also known as Swallowtail, has targeted defense contractors in two NATO countries, including a naval shipbuilder, a military aircraft engine manufacturer, and a law enforcement agency. The attacks utilized a new backdoor called Hookedge, which was first documented in August 2026.…
 Cyber Espionage Escalates in Europe Amid Geopolitical Tensions Cyberattacks on the public sector have surged by 114% in Europe over the past 30 months, with an average of 2,563 attacks per week per organization. This increase is attributed to rising geopolitical tensions, particularly related to the ongoing conflict between Russia and Ukraine. Check Point Research reports that…