 Breakingdefense
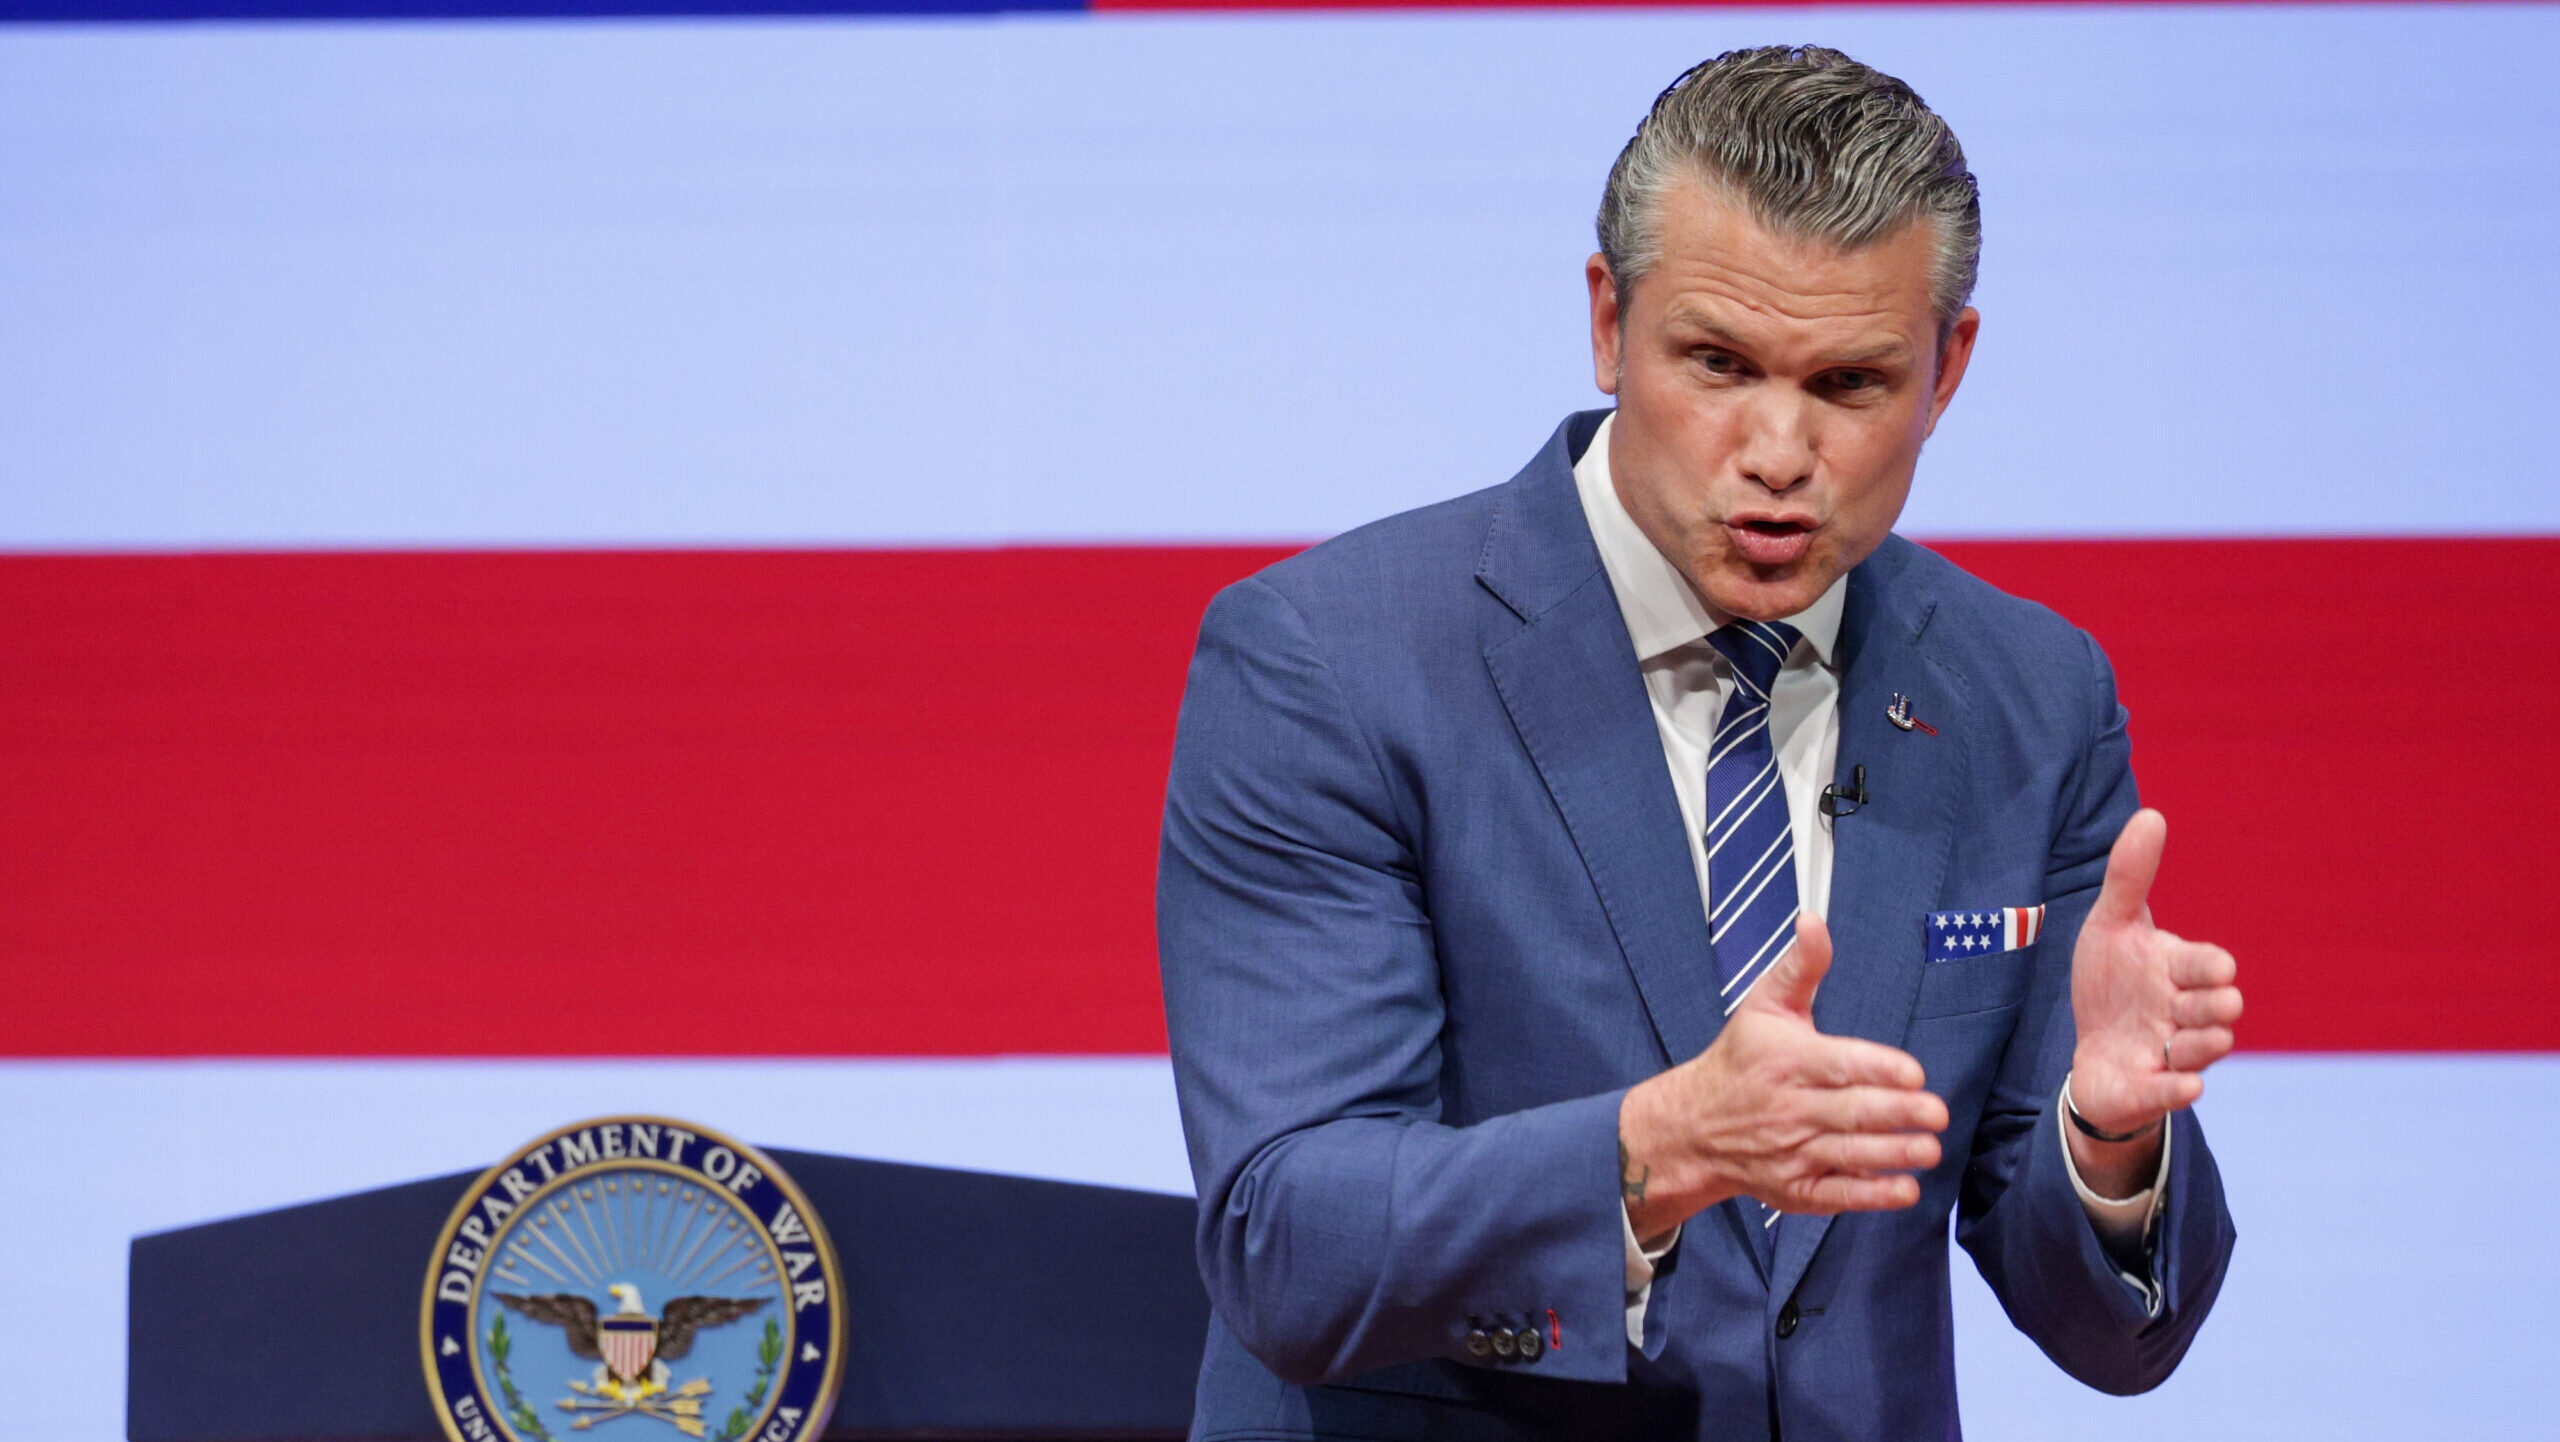
Hegseth Announces New Autonomous Warfare Command for Drones
Article Content

- •AUTOWARCOM will oversee military drone technology and operations.
- •The command is set to be functional by October 2027, pending Congressional approval.
- •Project Agincourt will lead initial efforts to integrate drone capabilities with military operations.
On September 30, 2026, Defense Secretary Pete Hegseth announced the establishment of the Autonomous Warfare Command (AUTOWARCOM) to enhance military drone capabilities. This new four-star command aims to streamline the acquisition and deployment of drones and robotics, marking a significant shift in military operations. Hegseth emphasized the need for a purpose-built system that allows for rapid adaptation and iteration in warfare. The command is expected to be operational by October 2027 and will require Congressional approval to grant acquisition authorities similar to those of Special Operations and Cyber commands. Additionally, Project Agincourt will lead the initial steps towards this command, focusing on integrating operators with entrepreneurs for effective warfighting acquisition. The initiative also includes collaboration with notable figures like Elon Musk and Palmer Luckey to explore future warfare strategies. The overall goal is to enhance the U.S. military's capabilities in autonomous warfare.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What is AUTOWARCOM?
When will AUTOWARCOM be operational?
Who is involved in Project Agincourt?
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…