 Securitybrief
Hetzner Enhances DDoS Protection with Nokia Deepfield Deployment
Article Content

- •Hetzner has deployed Nokia's Deepfield Defender for enhanced DDoS protection.
- •The system uses machine learning and real-time analytics to filter attack traffic.
- •The deployment covers Hetzner's European data centers and peering connections.
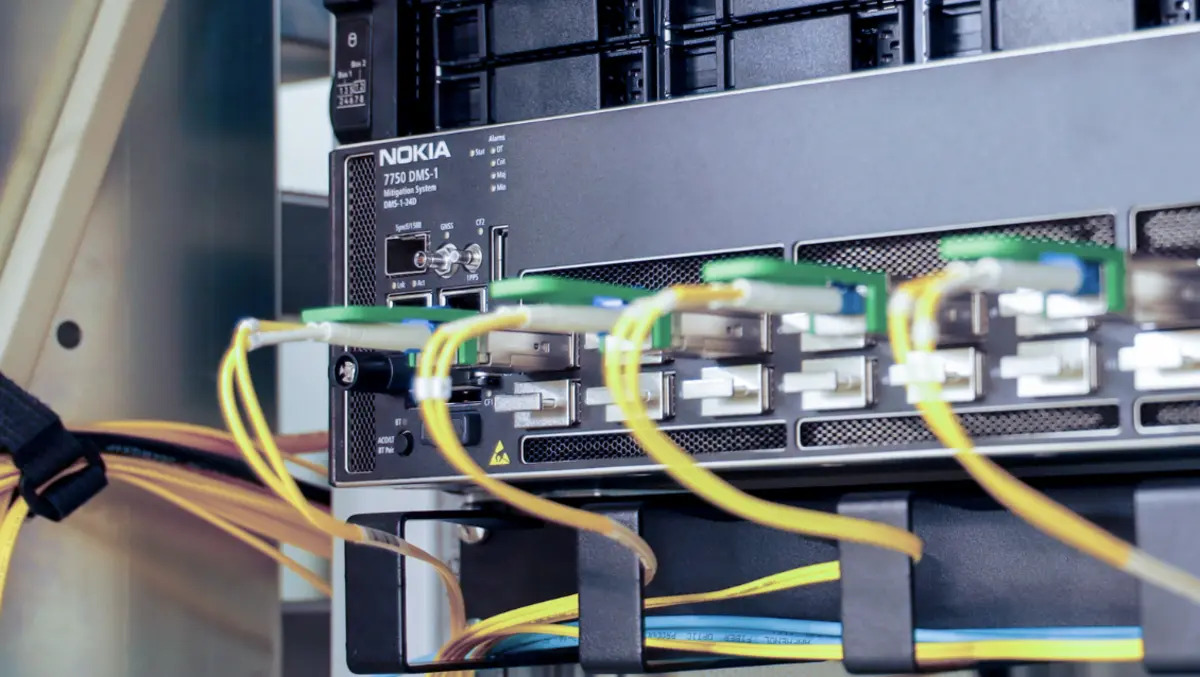
Hetzner, a German cloud provider, has implemented Nokia's Deepfield Defender across its European data centers to enhance its DDoS defense capabilities. This deployment aims to push mitigation closer to the network edge, effectively filtering attack traffic before it impacts deeper infrastructure. The system utilizes real-time traffic analytics and machine learning to identify and mitigate threats, reducing congestion during high-volume attacks. Hetzner's infrastructure includes data centers in Nuremberg, Falkenstein, and Helsinki, and the deployment covers both European sites and peering connections. The approach allows for automated and accurate defense against DDoS attacks while maintaining control over legitimate traffic. The Deepfield Defender integrates with Juniper routers and employs a multi-layered setup for effective traffic management. This initiative is particularly relevant as cloud platforms are frequent targets for DDoS attacks, which can disrupt services for multiple customers.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 PHP2Shell Vulnerabilities Exploited by AI-Driven Attackers Threat actors have exploited PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) to target a government entity in Europe, gaining access to sensitive data within two hours of the initial breach. The attackers utilized AI tools for reconnaissance and post-exploitation activities, including accessing…