 ecfr.eu
Houthi Attacks Disrupt Saudi Oil Infrastructure Amid Escalating Regional Tensions
Article Content

- •Houthi attacks have disrupted Saudi oil exports, impacting global supply.
- •The East-West pipeline has been targeted, highlighting vulnerabilities in oil transport routes.
- •Regional conflicts in the Horn of Africa are compounding security risks in the Red Sea.
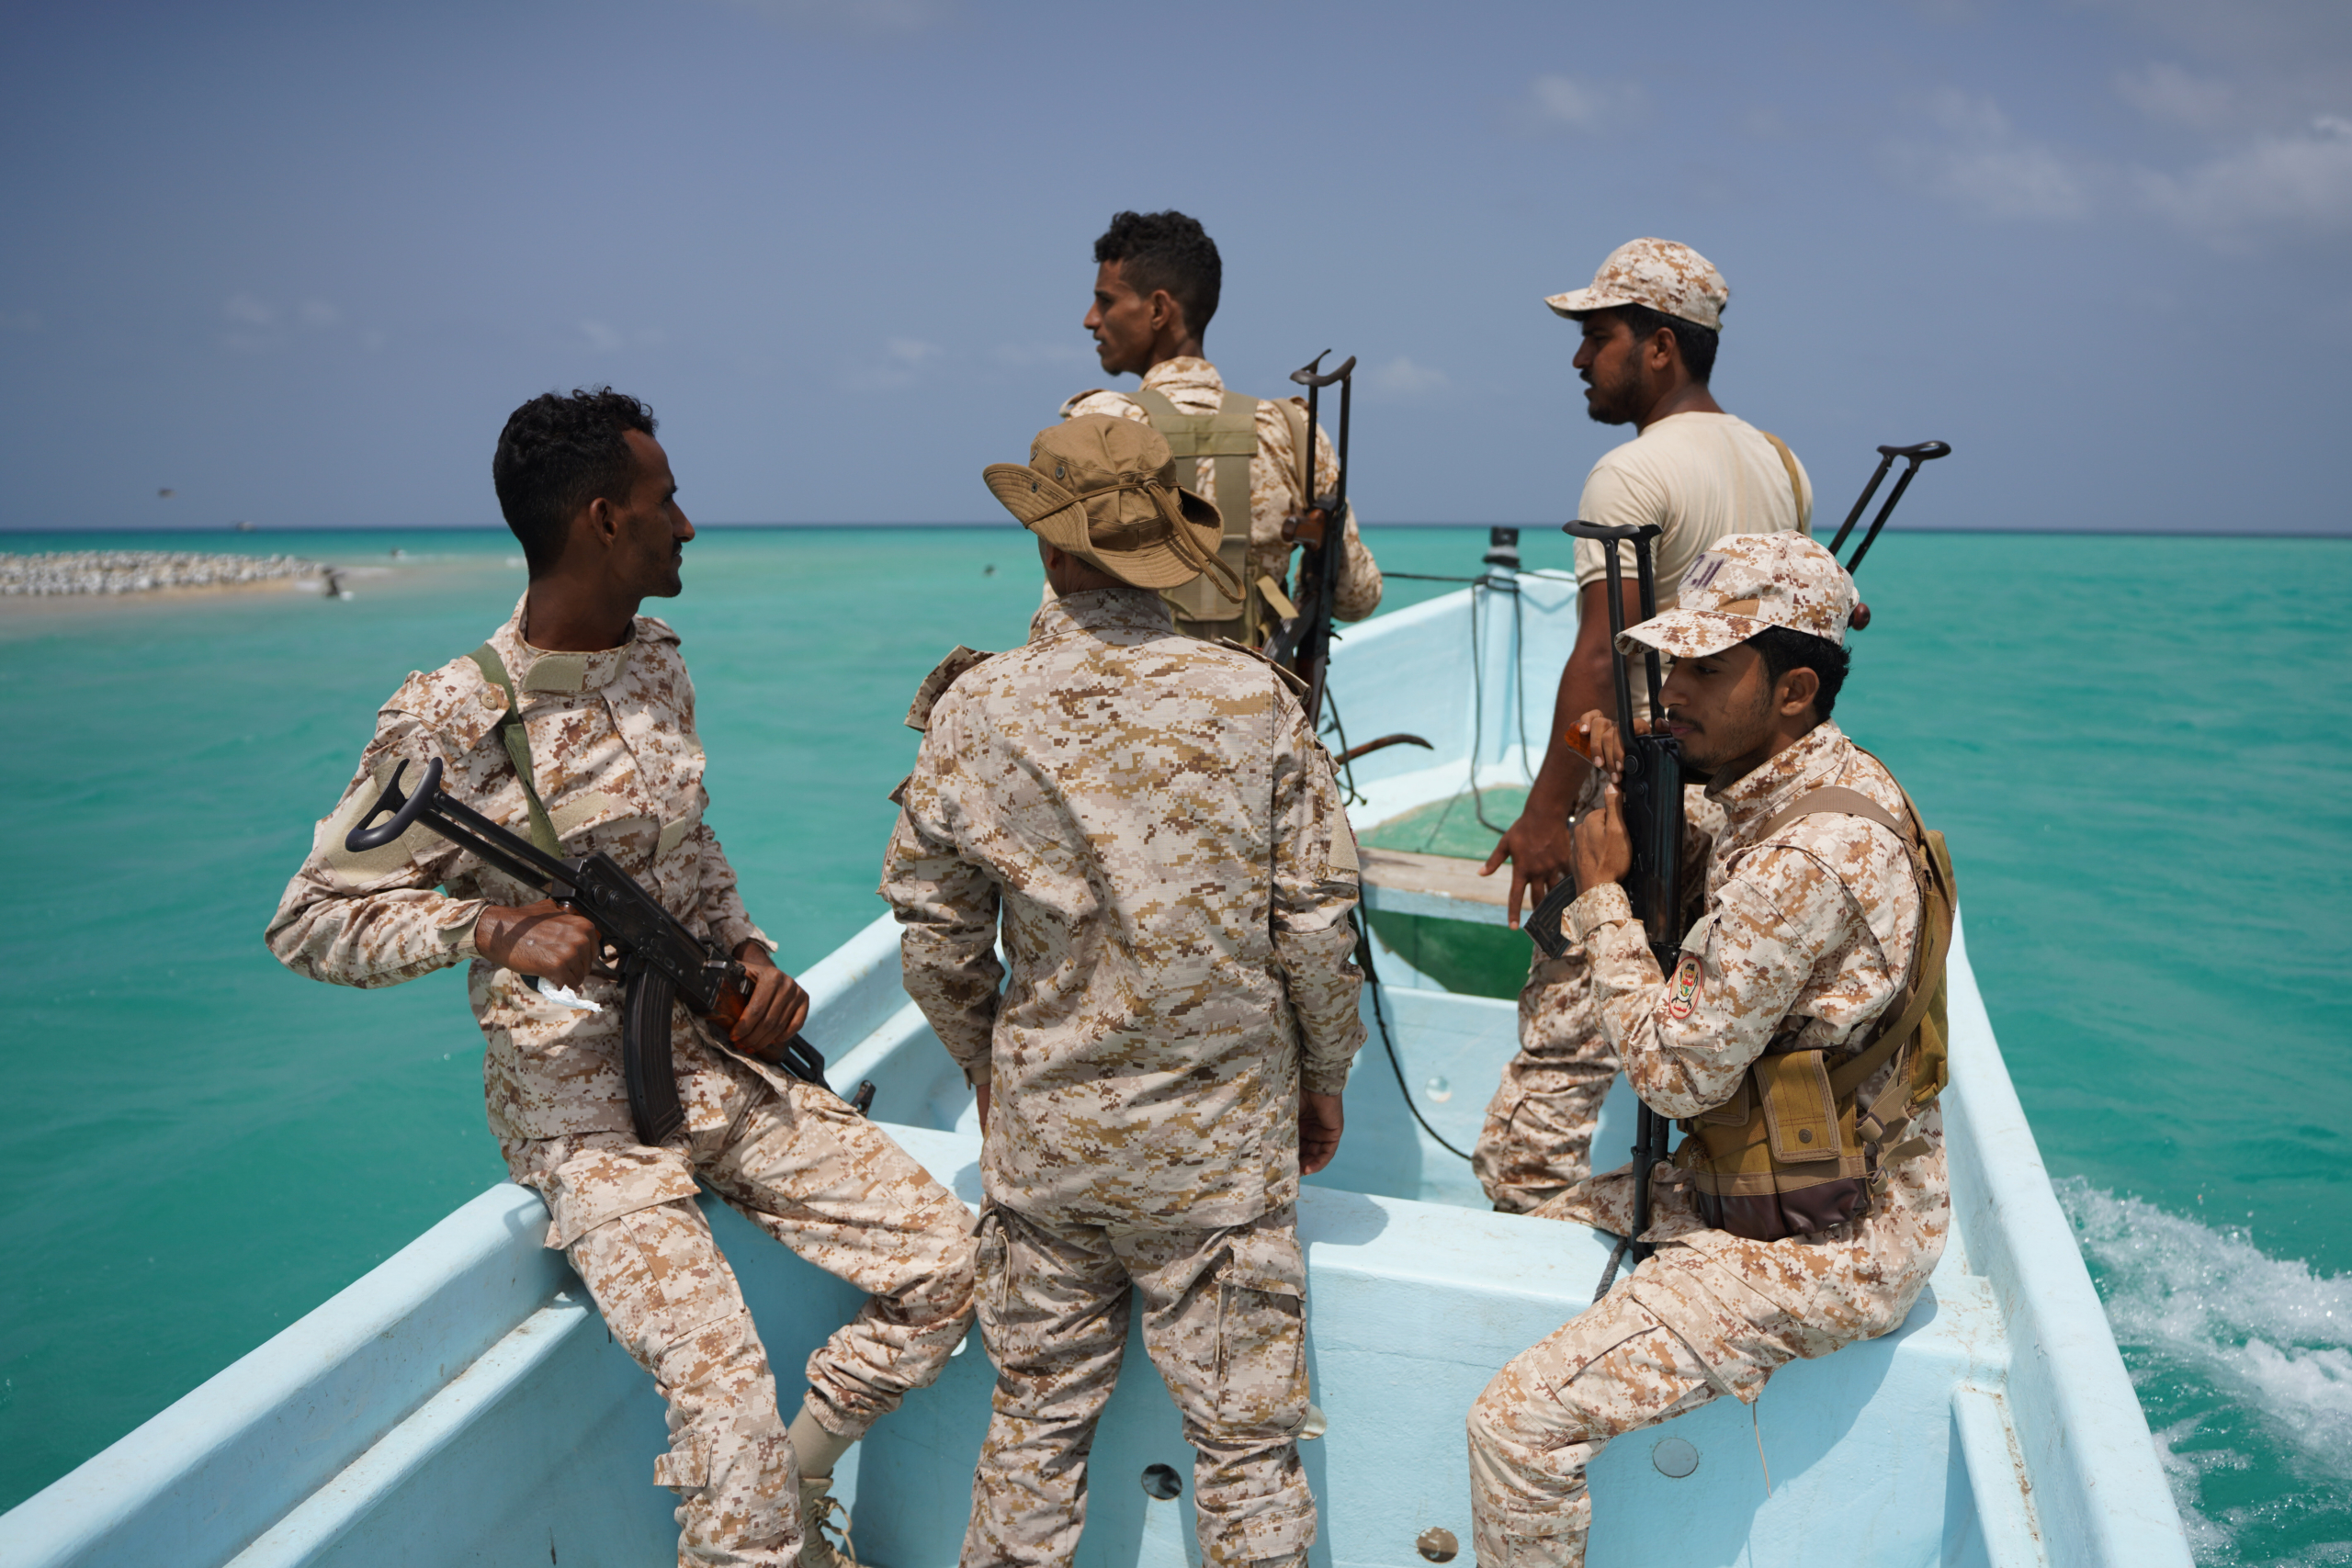
In recent months, Houthi militants have targeted Saudi oil tankers and facilities, significantly impacting oil exports through the Red Sea. The attacks, which include drone strikes on the Saudi East-West pipeline, have highlighted vulnerabilities in alternative oil routes as tensions rise due to the ongoing U.S.-Iran conflict. Saudi Arabia's reliance on the Red Sea for oil exports has increased, with shipments nearly doubling from previous years. The disruption has resulted in a global oil output decline of 11-12 million barrels per day, raising prices by approximately $30 per barrel since March 2026. The situation is exacerbated by instability in the Horn of Africa, where conflicts are merging and threatening maritime security. The Houthis are not the only threat, as piracy is resurging in the Gulf of Aden, further complicating the security landscape. The current status indicates a need for alternative energy export routes to mitigate risks associated with the Strait of Hormuz.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What areas are currently affected by the Houthi attacks?
How have these attacks impacted global oil prices?
What other threats exist in the region?
Continue Reading
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…