 South24
Houthi Militants Face Security Incident Amid AI-Enhanced Warfare
Article Content

- •Houthi forces reported thwarting a security incident in Sanaa involving drone activity.
- •The Houthis are developing advanced weaponry, including AI-guided systems, to enhance their military capabilities.
- •Tensions remain high as the Houthis threaten retaliation against Saudi Arabia for the alleged attacks.
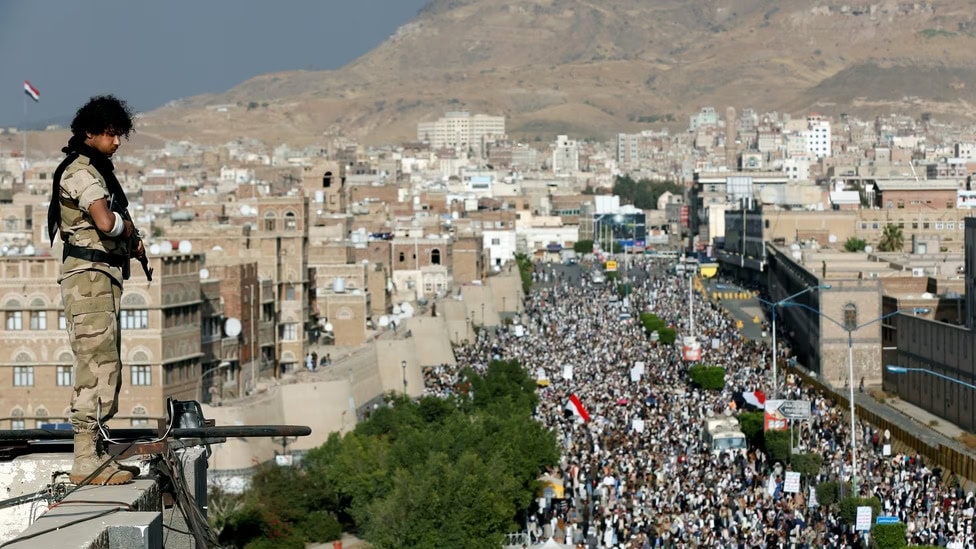
On September 18, 2026, Houthi militia acknowledged a security incident in Sanaa amid reports of drone activity and ground operations allegedly conducted by Saudi forces. Houthi spokesman Yahya Saree claimed their forces thwarted attempts by the 'Saudi enemy' using tactics reminiscent of ISIS. The Houthis have been enhancing their military capabilities, including the development of guided weapons using AI technology. Reports indicate that the incident involved drone strikes targeting Houthi command centers and weapons depots, with claims of casualties among Houthi leaders. The situation remains tense, with the Houthis threatening retaliation against Saudi targets. The incident highlights the ongoing conflict dynamics in Yemen, where the Houthis have been increasingly assertive in their military operations. The Houthis have controlled Sanaa since 2014 and continue to adapt their strategies amid external pressures.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Aramco in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…