 Foxnews
Houthis Launch Deadly Attacks on Saudi Airports, Prompting Global Security Concerns
Article Content

- •Houthis conducted missile and drone attacks on Saudi airports, killing 17 and injuring 333.
- •Former U.S. envoy warns of the Houthis operating independently from Iran, increasing their threat level.
- •UK Embassy advises against non-essential travel to several Saudi cities due to security risks.
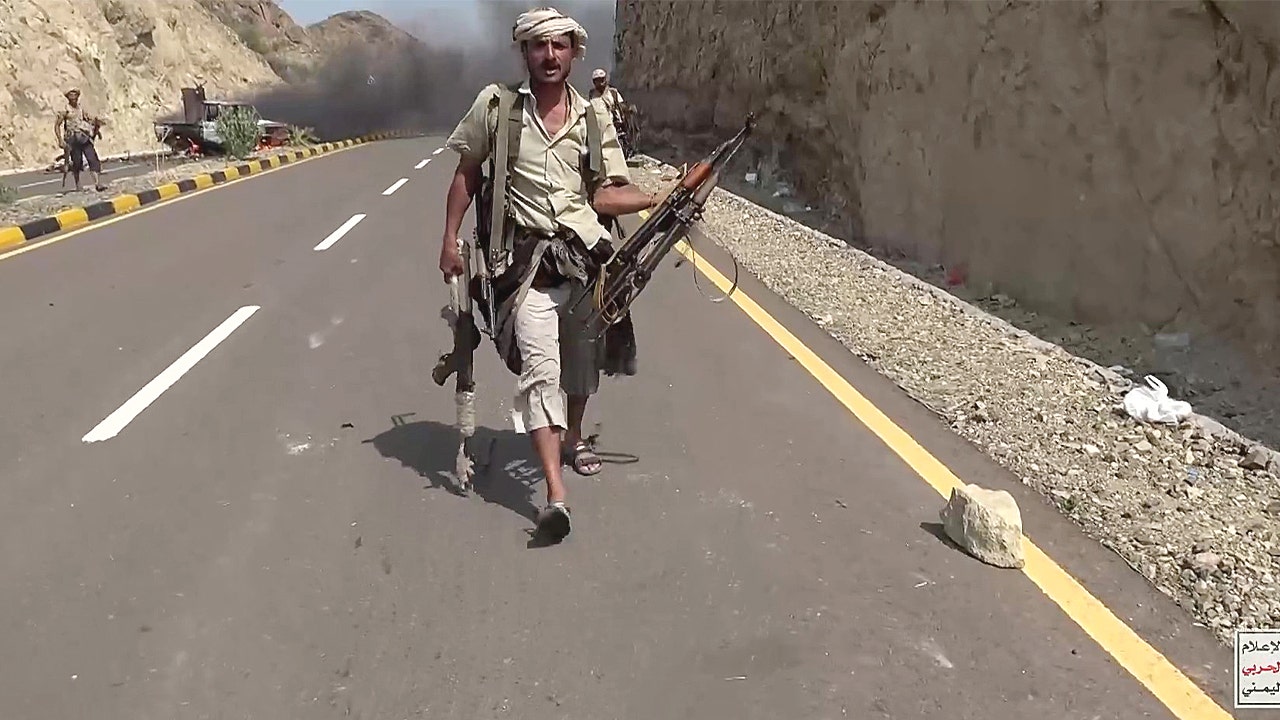
The Iran-backed Houthi group has intensified its missile and drone attacks on Saudi Arabia, notably targeting King Khalid International Airport in Riyadh, resulting in 17 fatalities and 333 injuries from October 7 to 11, 2026. Former U.S. envoy Tim Lenderking warns that the Houthis are increasingly operating independently of Iran, posing a significant threat to regional stability and global shipping routes. The Saudi-led coalition spokesperson, Turki al-Maliki, confirmed that the airport has faced 20 attacks since October 1. The UK Embassy in Saudi Arabia has issued travel advisories for British citizens, indicating heightened security risks in Jeddah, Dammam, and other airports. The situation raises concerns about potential escalations involving international actors, including the U.S. and Iran, as the Houthis enhance their military capabilities with foreign technology.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What specific locations are affected by the Houthi attacks?
What is the current travel advisory for Saudi Arabia?
How many casualties resulted from the recent attacks?
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Critical Zero-Day Exploit Found in BeyondTrust Remote Support BeyondTrust disclosed a critical vulnerability, CVE-2026-102764, in its Remote Support product, exploited by the suspected China-linked group ARMORY CASTLE since August 2026. This flaw, with a CVSS score of 9.3, allows attackers to perform arbitrary file uploads and gain host-level control without requiring…