 Amnesty
Huthis Prosecute UN and Civil Society Workers in Yemen
Article Content

- •At least eight UN and civil society workers face espionage charges in Yemen.
- •The Huthis have detained over 100 humanitarian workers since May 2024.
- •Detainees report being tortured to obtain confessions.
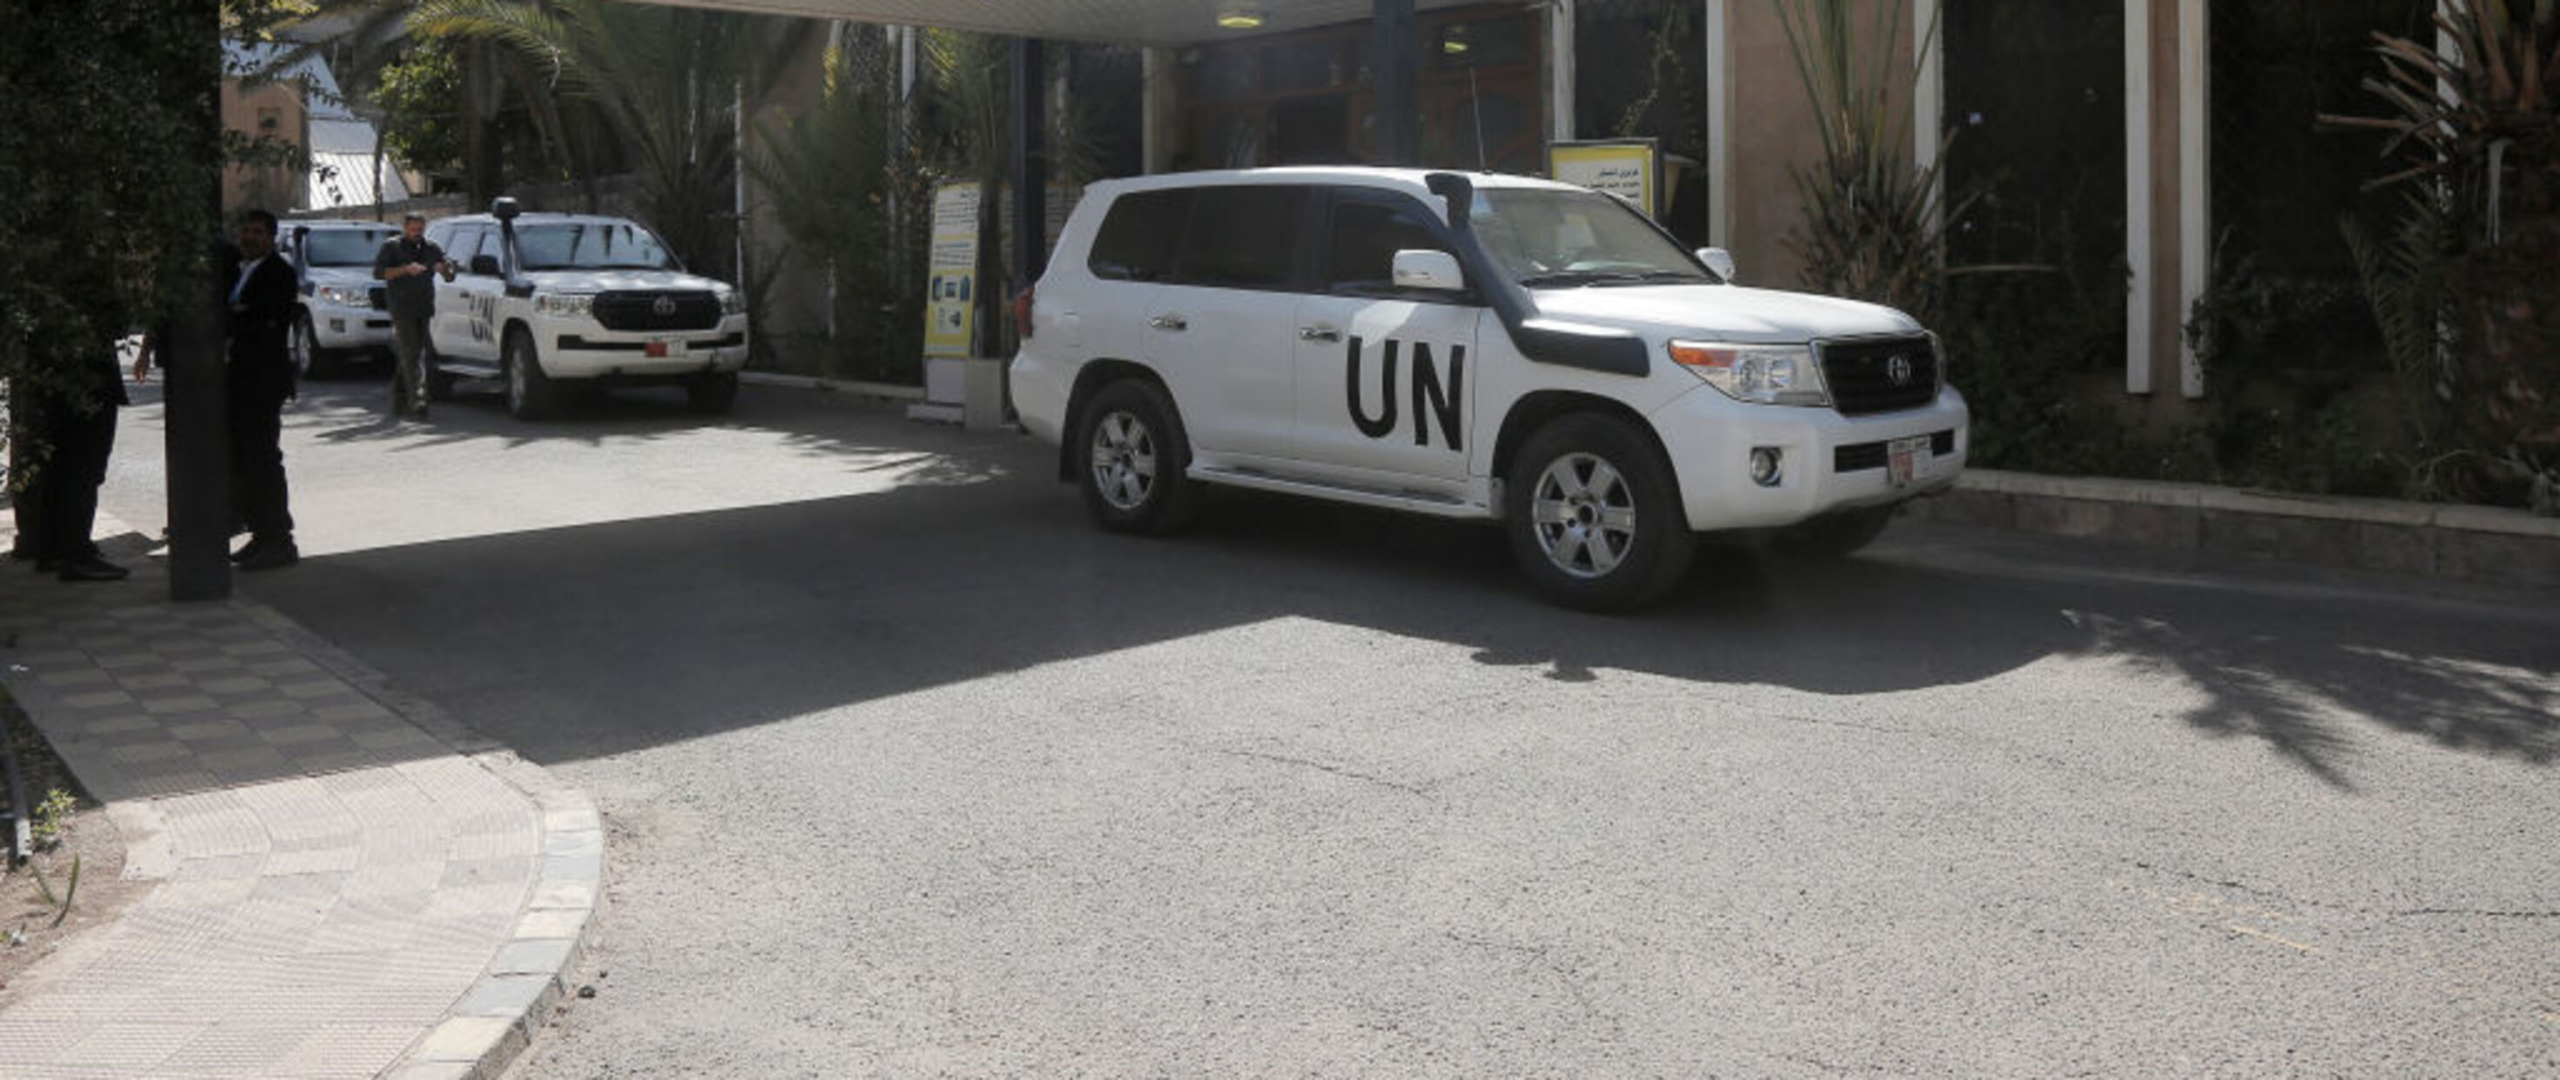
The Huthi authorities in Yemen have initiated criminal prosecutions against at least eight individuals involved in human rights and humanitarian work, including two UN employees and five civil society workers, on espionage charges that could lead to the death penalty. This action is part of a broader crackdown on civil society, with over 100 UN and civil society workers reportedly detained without charge since May 2024. The detainees, including those with serious health conditions, have allegedly been coerced into confessing under torture. Human Rights Watch and Amnesty International have called for their immediate release, emphasizing the deteriorating health of those detained. The situation reflects a significant escalation in the Huthis' efforts to silence dissent and target humanitarian efforts in the region.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Amnesty International in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How many workers are currently detained?
What charges are the detainees facing?
What has been the response from international organizations?
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…