 Amaniafrica-Et
Information Disorder Threatens Peace and Security in Africa
Article Content

- •Amani Africa warns of severe risks from information disorder impacting peace and security.
- •Disinformation is linked to rights violations, violence, and erosion of democratic governance.
- •The UN stresses the urgent need for strengthening information integrity in the digital age.
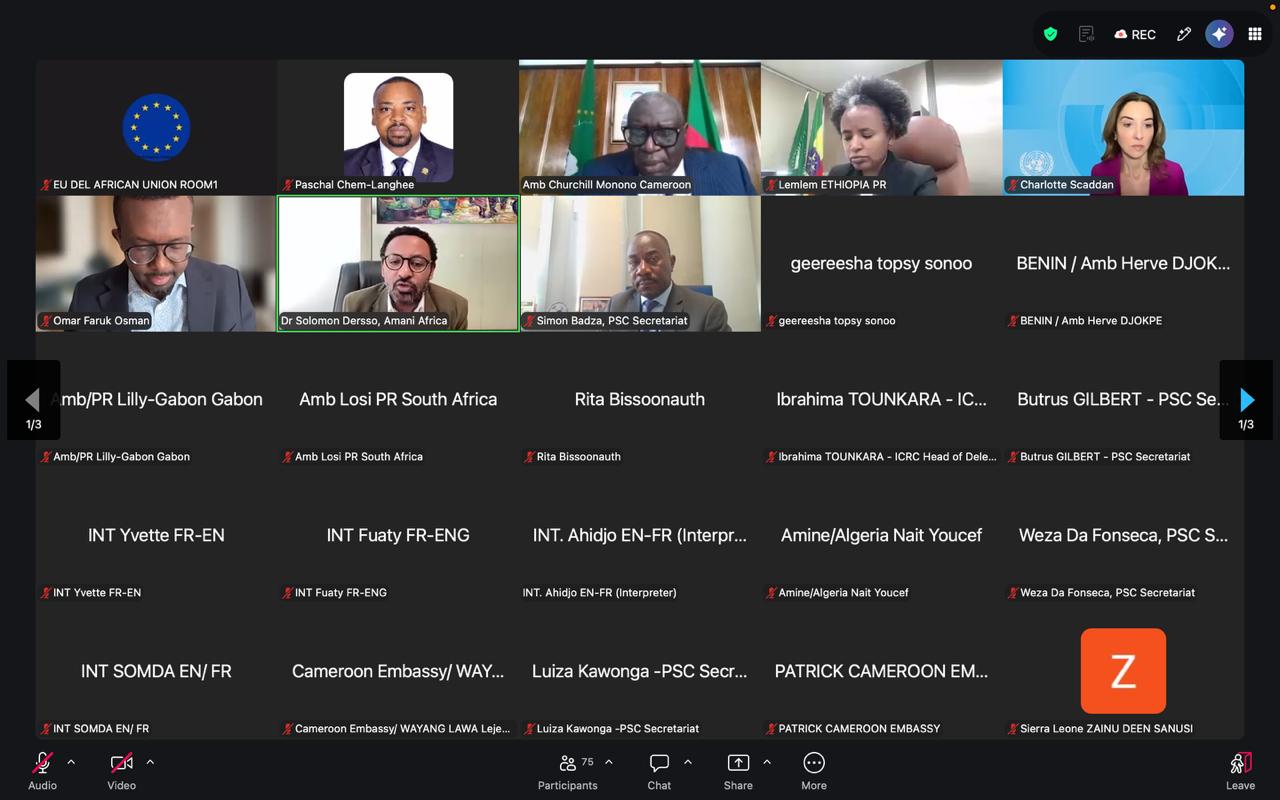
Amani Africa addressed the African Union Peace and Security Council on 9 October 2026, highlighting the severe risks posed by information disorder to stability, peace, and security across the continent. The organization cited a report from South Africa's Human Rights Commission, which noted that disinformation contributes to rights violations, including violence and discrimination. The UN has emphasized the urgent need to strengthen information integrity, as the absence of truth undermines trust and exacerbates conflict. The session underscored that disinformation particularly impacts political stability and democratic governance in Africa. Amani Africa's insights indicate that without addressing information integrity, the pursuit of peace will be significantly hindered. The ongoing digital and AI advancements further complicate this challenge, making it a critical issue for the continent's future.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Twitter in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is information disorder?
How does disinformation affect peace?
What actions are being taken to address this issue?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Sets Oct. 11 Deadline for Patching Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog after they were exploited by the China-linked group Flax Typhoon. Federal agencies must patch or retire the affected software by October 11, 2026. The vulnerabilities…