 Theguardian
Iran's Attacks on Shipping in Strait of Hormuz Escalate Amid Ongoing Tensions
Article Content

- •Iran has attacked at least 15 container ships in the Strait of Hormuz in 10 days.
- •CENTCOM reports 97% of vessels have successfully transited despite Iranian threats.
- •The attacks have contributed to rising oil prices, nearing $108 per barrel.
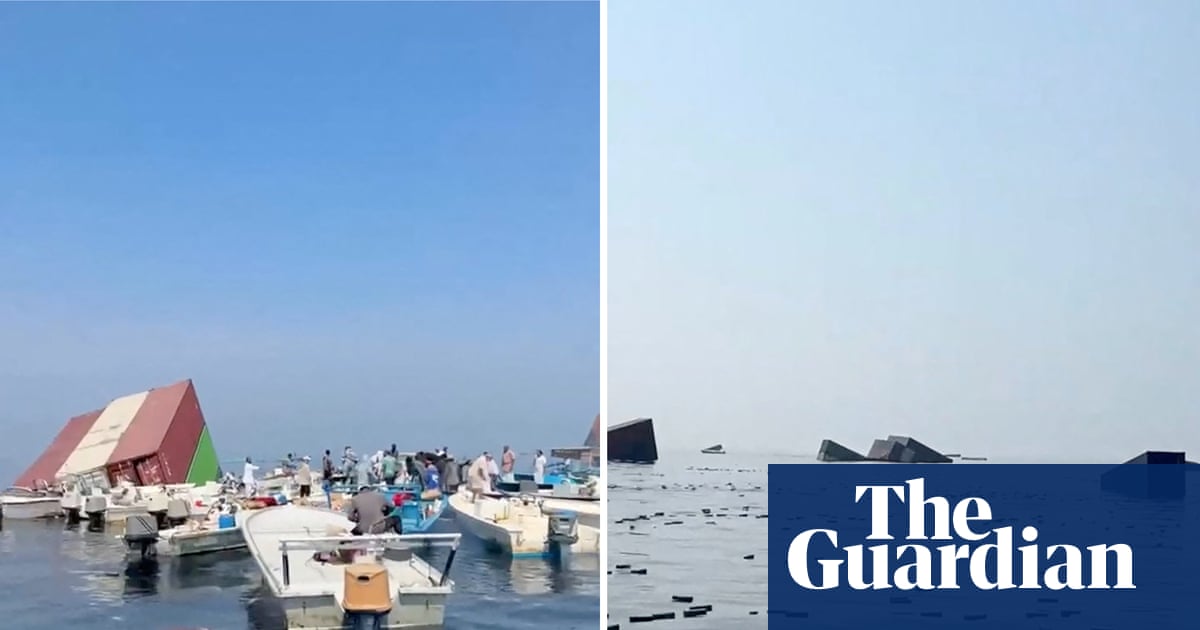
In the past 10 days, Iran has attacked at least 15 container ships in the Strait of Hormuz, employing drones, mines, and rocket-propelled grenades. The attacks have reportedly resulted in the sinking of a Singapore-flagged container ship, the GFS Pride, which was struck by an Iranian projectile. U.S. Central Command (CENTCOM) claims that the majority of these attacks have been unsuccessful, with 97% of vessels transiting the strait remaining unharmed. Despite the attacks, maritime traffic continues, with over 400 merchant ships reported to have sailed through the strait recently. The Islamic Revolutionary Guard Corps (IRGC) asserts its right to target vessels without permission. The situation has led to increased oil prices, with Brent crude nearing $108 per barrel. The Iranian government has warned local fishers against looting the cargo from sunken vessels, claiming the goods belong to the state.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What types of vessels are affected?
How successful are these attacks?
What should shipping companies do?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…