 Time
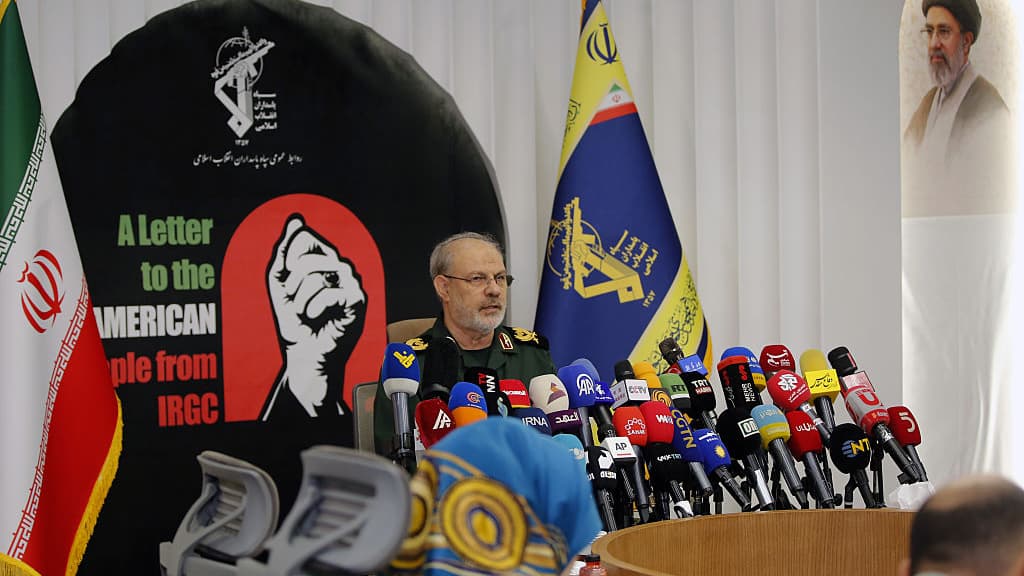
Iran's Revolutionary Guard Appeals to U.S. Voters Amid Ongoing War
Article Content

- •The IRGC's letter urges U.S. voters to reject politicians supporting military intervention.
- •The letter claims Iran has retained control over the Strait of Hormuz despite U.S. actions.
- •The U.S. withdrawal from Iraq is seen by Iran as a victory for its regional influence.
Iran's Islamic Revolutionary Guard Corps (IRGC) issued a 26-page open letter to American voters, urging them to remove U.S. politicians supporting military intervention and the war against Iran. The letter was published as U.S. forces withdrew from Iraq, a move celebrated by Tehran. The IRGC claims the U.S. has failed to achieve its objectives in the conflict, which has been ongoing for eight months. The letter accuses the Trump Administration of deceit and calls for political change through voting. It highlights the rising energy prices and inflation as key issues affecting American voters. The IRGC asserts that Iran has maintained control over the Strait of Hormuz and gained cultural influence despite U.S. military actions. The letter's impact on U.S. elections remains uncertain, as it may not reach a significant portion of the electorate. The ongoing conflict has drawn in Iranian allies and exacerbated tensions in the region.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Common questions
What does the IRGC's letter call for?
How has the U.S. withdrawal from Iraq been perceived?
What are the implications of the ongoing war for U.S. voters?
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…