 Recordedfuture
IRGC-linked GreenJuliett Uses AI in Industrial Attacks on OT and PLCs
Article Content

- •France attributed the October 2026 refrigeration controller attacks at 700+ retail sites to Shahid Kaveh, an IRGC-CEC unit; Recorded Future has not tied GreenJuliett directly to them.
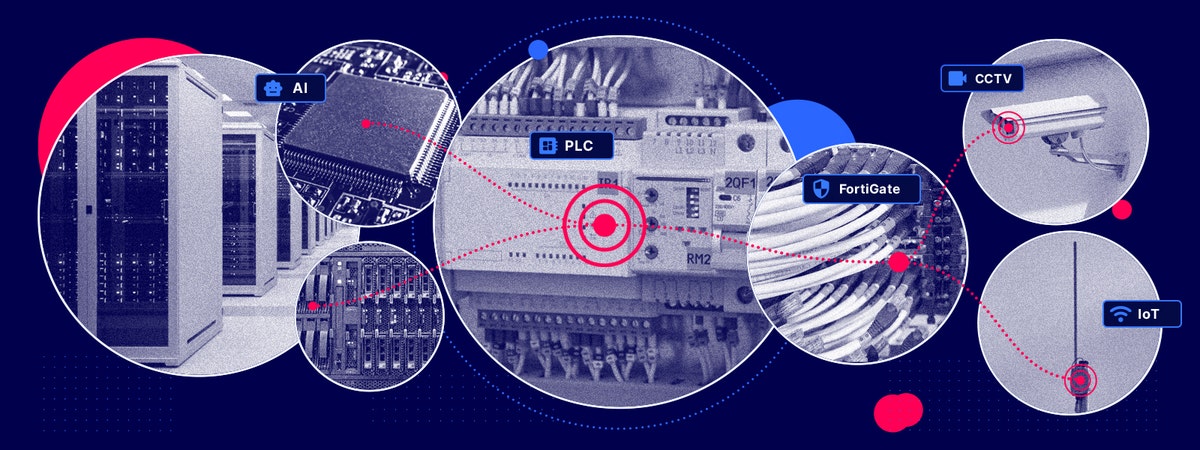
- •GreenJuliett-linked infrastructure scanned or attempted exploitation of Fortinet FortiGate firewalls in six Middle Eastern countries between August and October.
- •Recorded Future observed LiteLLM configurations and Claude-hosting communications on GreenJuliett-linked infrastructure, but has not confirmed specific AI misuse.
- •The group continues to target internet-exposed PLCs, similar to the controllers affected in France.
- •Recorded Future says AI-driven offensive frameworks such as ARTEX AI are already deployed at scale.
Recorded Future reports that on October 11 and 12, 2026, someone changed defrost settings on refrigeration controllers at more than 700 retail locations in France, causing fires, equipment damage and food losses estimated in the tens of millions of euros. On November 9, France attributed the attack to Shahid Kaveh, a unit of Iran's IRGC Cyber Electronic Command. Recorded Future tracks activity likely belonging to Shahid Kaveh as GreenJuliett (also known as CyberAv3ngers and Bauxite), which it says builds infrastructure aimed at internet-facing PLCs. Recorded Future states it has not independently tied GreenJuliett infrastructure to the refrigeration attacks. Between August and October, GreenJuliett-linked infrastructure was observed scanning or attempting to exploit Fortinet FortiGate firewalls in Bahrain, Israel, Jordan, Kuwait, Saudi Arabia and Qatar, and network data suggests the group is working to add IoT and CCTV devices. In October 2024, OpenAI banned accounts it assessed as belonging to CyberAv3ngers, which had used ChatGPT for PLC default-credential research and Modbus TCP scripts. In October 2026, Recorded Future found a LiteLLM configuration and Persian-language chat applications on infrastructure it assessed as likely GreenJuliett-linked, and observed anonymization-network servers communicating with infrastructure hosting Anthropic's Claude. Recorded Future has not confirmed specific AI misuse in this research. The report also describes ARTEX AI as one of eight offensive AI frameworks it tracked, deployed at scale as an autonomous operator rather than an assistant.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track CyberAv3ngers, Chisel and Shahid Kaveh in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Are we affected by the FortiGate scanning?
Has the group's AI use been confirmed?
What should OT operators do first?
Continue Reading
 Cyberwarfare Threats Targeting U.S. Critical Infrastructure Rise Recent reports indicate an increase in cyberwarfare activities targeting U.S. critical infrastructure, particularly from state-linked groups. Notably, Iranian hackers have been linked to cyberattacks on water systems, including a significant incident in Atlanta where a water pump station malfunctioned. Additionally, a…