 Jcfa
IRGC's Exploitation of Children and Human Trafficking in Iran
Article Content

- •IRGC exploits Iranian and migrant children as soldiers, according to the U.S. State Department.
- •The recruitment of minors for military purposes constitutes a severe violation of child rights.
- •The Iranian regime faces little accountability for its human trafficking and exploitation practices.
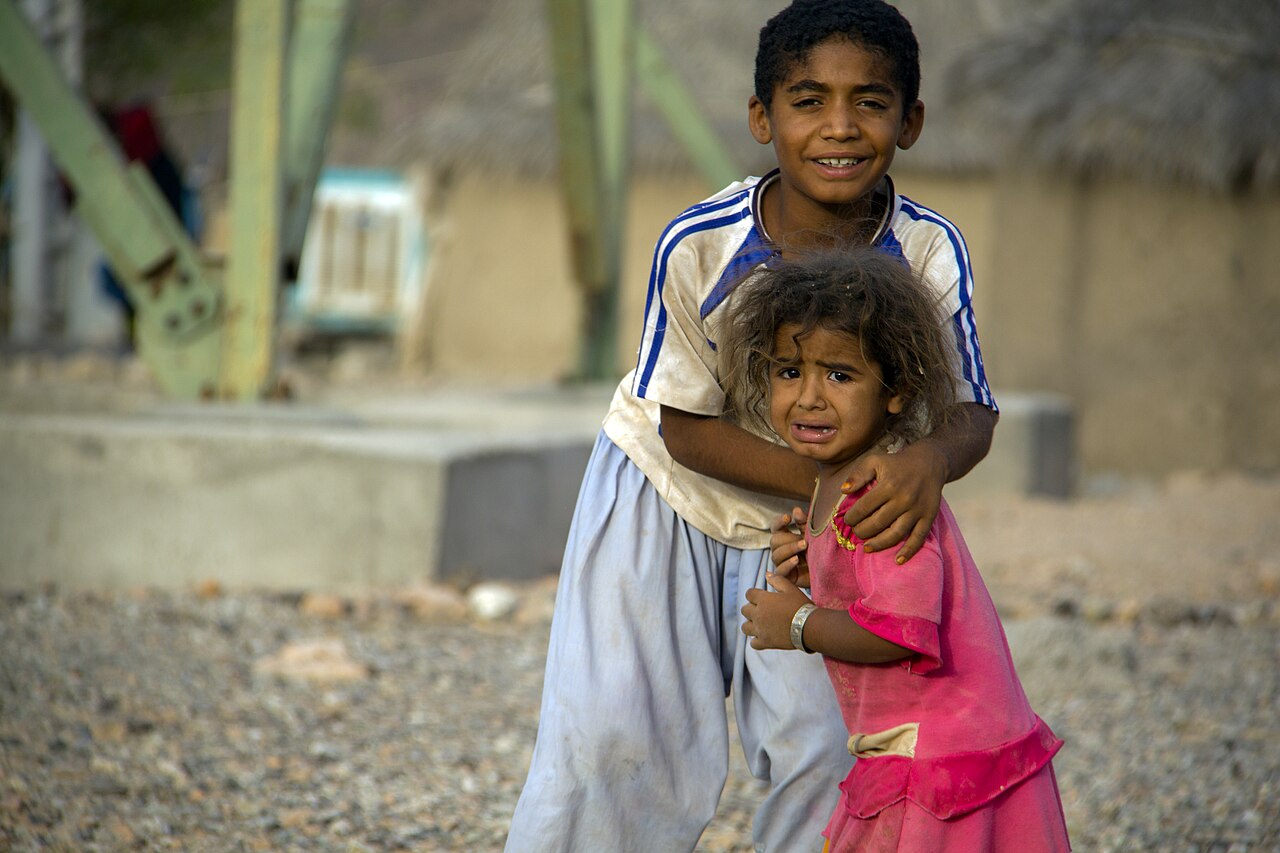
The U.S. State Department's 2026 Trafficking in Persons report reveals that the Islamic Revolutionary Guard Corps (IRGC) has exploited Iranian and migrant children as soldiers. The report documents the IRGC's recruitment of minors for military operations, including the deployment of Afghan, Pakistani, and Syrian children. This exploitation is part of a broader pattern of human trafficking facilitated by the Iranian regime, which uses vulnerable populations for military and economic gain. The IRGC's actions include forcibly recruiting children and providing support to non-state armed groups that also utilize child soldiers. The report highlights the impunity enjoyed by Iranian officials involved in these trafficking crimes. The situation reflects a severe violation of child rights and international law, with the recruitment of children under 15 classified as a war crime. Despite international condemnation, the Iranian regime continues these practices with little accountability.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What specific actions are documented in the TIP report?
What are the implications of these findings?
How can this situation be addressed?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…