 Theregister
Ivanti Releases Patch for Active Zero-Day Vulnerability in Connect Secure
Article Content

- •Ivanti's Connect Secure VPN is affected by a zero-day vulnerability.
- •Researchers confirmed in-the-wild exploitation of this flaw.
- •A patch has been released, and organizations are urged to apply it immediately.
Ivanti has released a patch for a zero-day vulnerability in its Connect Secure VPN product after researchers confirmed. The flaw, which affects multiple versions of Connect Secure, allows unauthorized access to sensitive systems. Ivanti is also addressing a separate privilege escalation issue, with a fix expected in the coming weeks. The company has not disclosed specific details about the attack vector or the number of affected users. Organizations using Connect Secure are urged to apply the patch immediately to mitigate risks. This incident highlights the ongoing threat posed by zero-day vulnerabilities in widely used software.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Shai-Hulud Worm in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What versions of Connect Secure are affected?
How urgent is it to apply the patch?
Are there any known attack vectors?
Continue Reading
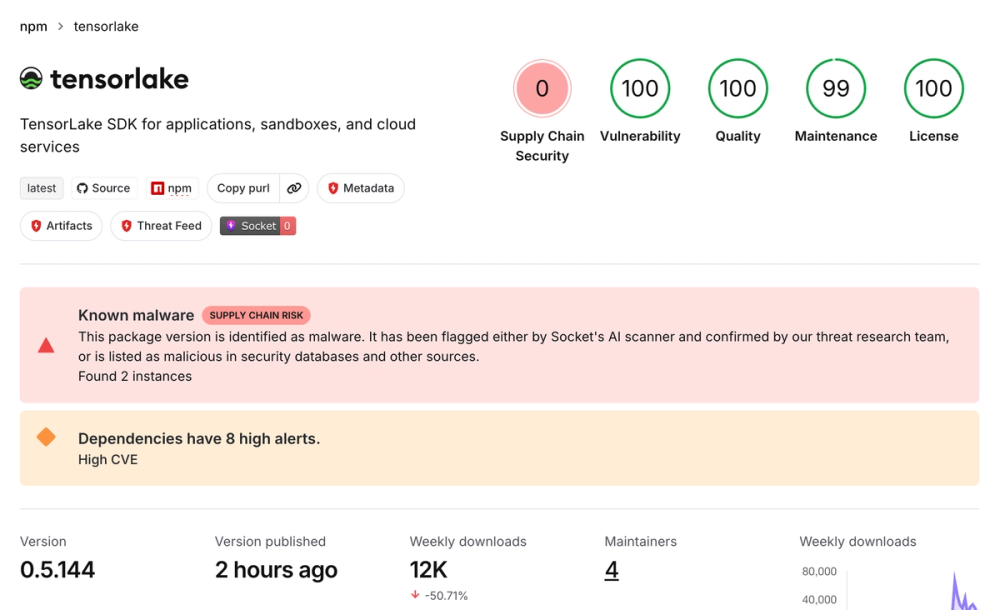 Tensorlake npm Package Compromised by Shai-Hulud Worm On October 8, 2026, the Tensorlake npm package version 0.5.144 was compromised, delivering a credential-stealing worm known as Shai-Hulud. The malware, which was published through a compromised maintainer account, executes a preinstall hook that runs an obfuscated loader to harvest credentials from local files and CI…
 Ransomware Threats Intensify with Personal Targeting Tactics A recent global survey revealed that 37% of ransomware attacks now involve psychological or physical threats, indicating a shift towards more personal and aggressive tactics by cybercriminals. This trend is raising alarms among security professionals as attackers leverage personal information to intimidate victims.…