 Nippon
Japanese Lawyers Petition Against US Sanctions on ICC President
Article Content

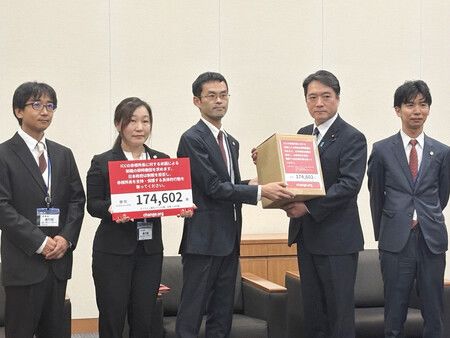
- •A group of lawyers in Japan submitted a petition with over 174,600 signatures against U.S. sanctions.
- •The sanctions target ICC President Akane Tomoko, freezing her assets in the U.S.
- •Deputy Chief Cabinet Secretary Masanao Ozaki affirmed Japan's support for the ICC during discussions.
A group of Japanese lawyers has submitted a petition to the government, urging action against U.S. sanctions imposed on Akane Tomoko, the President of the International Criminal Court (ICC). The sanctions, announced by the Trump administration in August, accuse the ICC's leadership of abusing authority and include asset freezes. The lawyers, former students of Akane, collected over 174,600 signatures online in support of their petition. They met with Deputy Chief Cabinet Secretary Masanao Ozaki, who reiterated Japan's support for the ICC. The petition calls for Japan to engage in discussions with the U.S. to lift the sanctions, emphasizing the importance of the ICC's independence. The lawyers argue that Japan's relationship with the U.S. positions it to advocate for the ICC effectively.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track International Criminal Court in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What are the U.S. sanctions about?
How many signatures were collected for the petition?
What is Japan's response to the sanctions?
Continue Reading
 Citrix NetScaler Critical Vulnerabilities Exploited: Urgent Patching Required Citrix NetScaler ADC and Gateway products are affected by critical vulnerabilities CVE-2026-88771 and CVE-2026-88772, both assigned a CVSS score of 9.5. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on September 27, 2026, and mandated…
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…