 Hackread
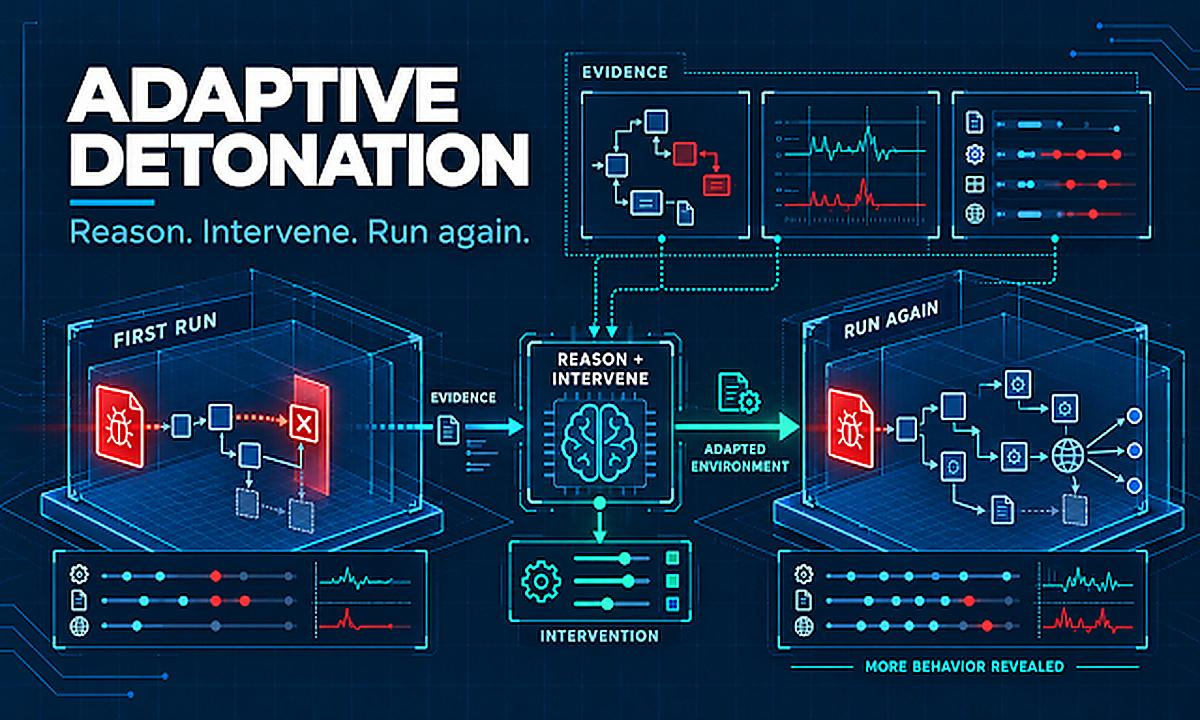
Joe Security Launches Adaptive Detonation for Enhanced Malware Analysis
Article Content

- •Adaptive Detonation enhances malware analysis by overcoming evasion techniques.
- •AI agents identify and address execution obstacles to reveal hidden malware behavior.
- •The new feature is part of Joe Sandbox AI and available for testing in Joe Sandbox Cloud.
Joe Security has introduced Adaptive Detonation, a new feature in Joe Sandbox AI designed to improve malware analysis by utilizing AI agents. This technology allows security teams to investigate evasive malware that may not reveal its behavior during initial sandbox execution. By identifying and addressing specific execution obstacles, such as missing dependencies or environmental checks, Adaptive Detonation enables deeper visibility into malware activities. The tool is aimed at enhancing the effectiveness of dynamic malware analysis and is available as part of Joe Sandbox Cloud. Security teams can register for a free community version to test the new feature. Joe Security, based in Switzerland, has been developing malware analysis technologies since 2011.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Following this threat?
Track Joe Security in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How does Adaptive Detonation work?
Is there a cost to use Adaptive Detonation?
What types of malware can Adaptive Detonation analyze?
Continue Reading
 Critical RCE Vulnerability in Confection WordPress Plugin (CVE-2026-115252) A critical vulnerability, CVE-2026-115252, has been identified in the Confection WordPress Cable plugin, affecting versions 0.4.0 to 0.4.7. This flaw allows unauthenticated attackers to execute arbitrary PHP code on the server by writing unmodified settings into a PHP file without proper checks. The vulnerability has…
 Critical RCE and LPE Vulnerabilities in Quest Foglight for Databases On November 3, 2026, the Zero Day Initiative disclosed multiple critical vulnerabilities in Quest Foglight for Databases, including six remote code execution (RCE) flaws and two local privilege escalation (LPE) vulnerabilities. The most severe RCE vulnerabilities, CVE-2026-92189 and CVE-2026-92190, allow…