 Kyivindependent
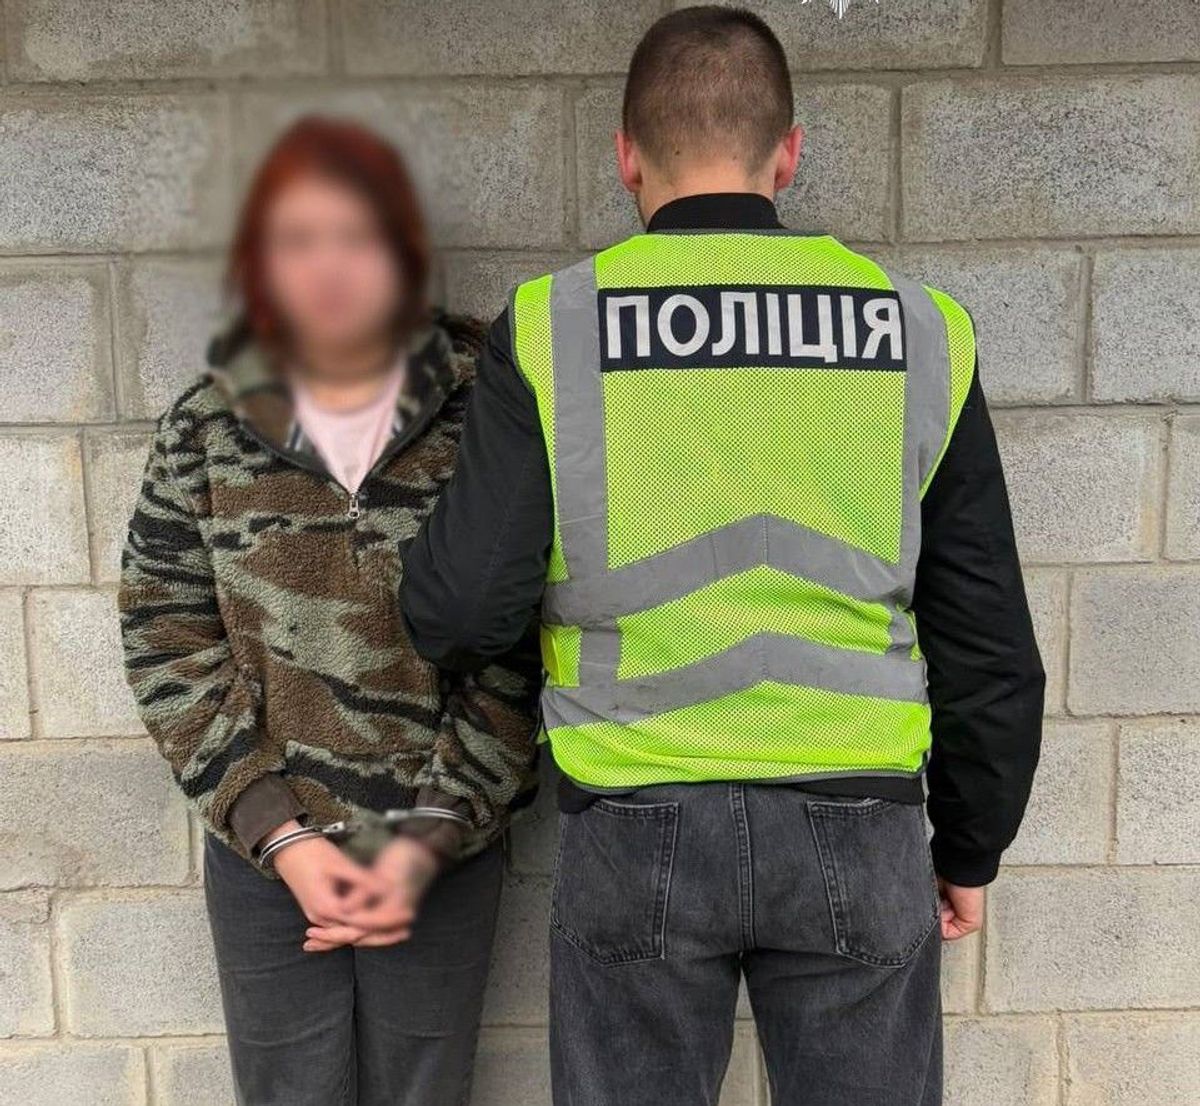
Kyiv Woman Arrested for Poisoning Colombian Veteran on Russian Orders
Article Content

- •A 19-year-old Kyiv woman is accused of poisoning a Colombian veteran on Russian orders.
- •The alleged murder involved a month-long relationship facilitated by a Russian intelligence handler.
- •Ukrainian authorities have identified a pattern of similar attacks targeting military personnel.
A 19-year-old woman from Kyiv has been arrested for allegedly poisoning a 32-year-old Colombian veteran of Ukraine's Armed Forces during a date. The incident, which occurred in a rented apartment in Kyiv's Obolonskyi district, is believed to have been orchestrated by a Russian intelligence handler who contacted the woman through a messaging app. The handler reportedly offered her $1,000 to carry out the murder, building a relationship with the victim over a month before the meeting. During the date, the woman allegedly added a toxic substance to the man's drink, leading to his death within an hour. Afterward, she reportedly filmed the aftermath and fled with money from the victim's pockets. The woman has been charged with premeditated murder and could face life imprisonment if convicted. This case is part of a broader pattern of Russian operatives using civilians to target military personnel in Ukraine.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What was the motive behind the poisoning?
How did the Russian handler communicate with the victim?
What charges does the suspect face?
Continue Reading
 Lazarus Group Targets 30 South Korean Servers Using PHP Vulnerabilities North Korea-linked Lazarus Group has targeted 30 servers in South Korea as part of a larger cyber operation involving 581 servers across 10 countries. The attacks exploit two critical remote code execution vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619), allowing unauthorized server command execution. The…
 Critical CVE-2026 Flaws in Control Web Panel Lead to Account Takeover Risks Control Web Panel (CWP) versions prior to 1.30.6 are affected by two critical vulnerabilities, CVE-2026-124020 and CVE-2026-124021, both disclosed on 2026-11-13. CVE-2026-124020 allows attackers to exploit a host header injection in the password recovery process, potentially leading to account takeover via a poisoned…