 Bloomberg
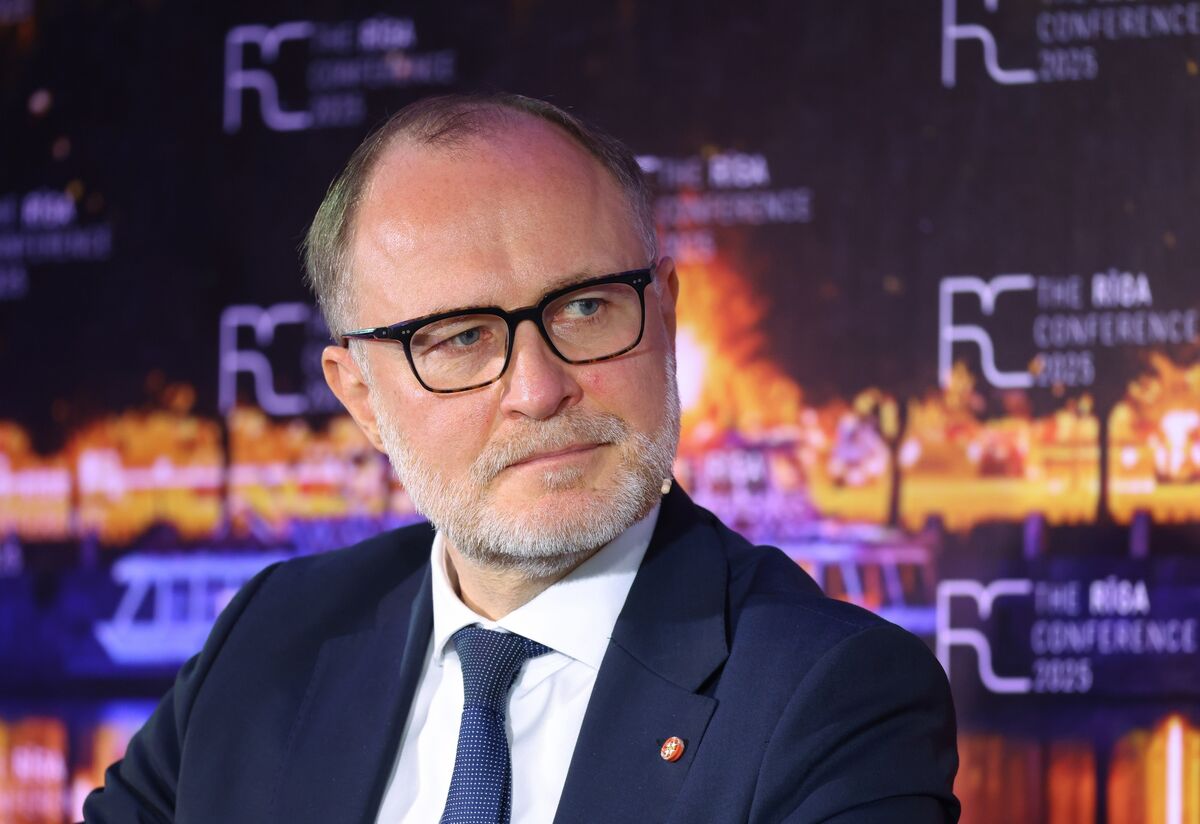
Latvian Defense Minister Resigns After Drone Incursions
Article Content

- •Latvian Defense Minister Andris Spruds resigned due to drone incursions from Ukraine.
- •The drones were reportedly diverted by Russian electronic warfare tactics.
- •Latvia's defense sector is committed to enhancing airspace security and public safety.
Latvian Defense Minister Andris Spruds resigned on May 10, 2026, following drone incursions that violated the country's airspace. Two Ukrainian drones, reportedly diverted by Russian electronic warfare, struck oil storage facilities in Latvia earlier that week. Prime Minister Evika Silina stated that Spruds had lost her trust and that of the public, prompting her request for his resignation. Colonel Raivis Melnis has been appointed as the new defense minister. Spruds emphasized the need to protect the military from political disputes and reaffirmed the commitment of the defense sector to ensure public safety. Ukrainian Foreign Minister Andrii Sybiha confirmed discussions with Latvia regarding the incidents and expressed Ukraine's willingness to cooperate with Baltic nations to prevent future occurrences. The situation highlights ongoing tensions in the region amid concerns over Russian aggression.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (8)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…