 Nbcconnecticut
Ledyard Terminates Flock Camera Use After Data Breach
Article Content

- •Ledyard terminated its contract with Flock due to a data breach.
- •Sensitive customer information was exposed, raising privacy concerns.
- •The town council unanimously voted to stop data collection from Flock cameras.
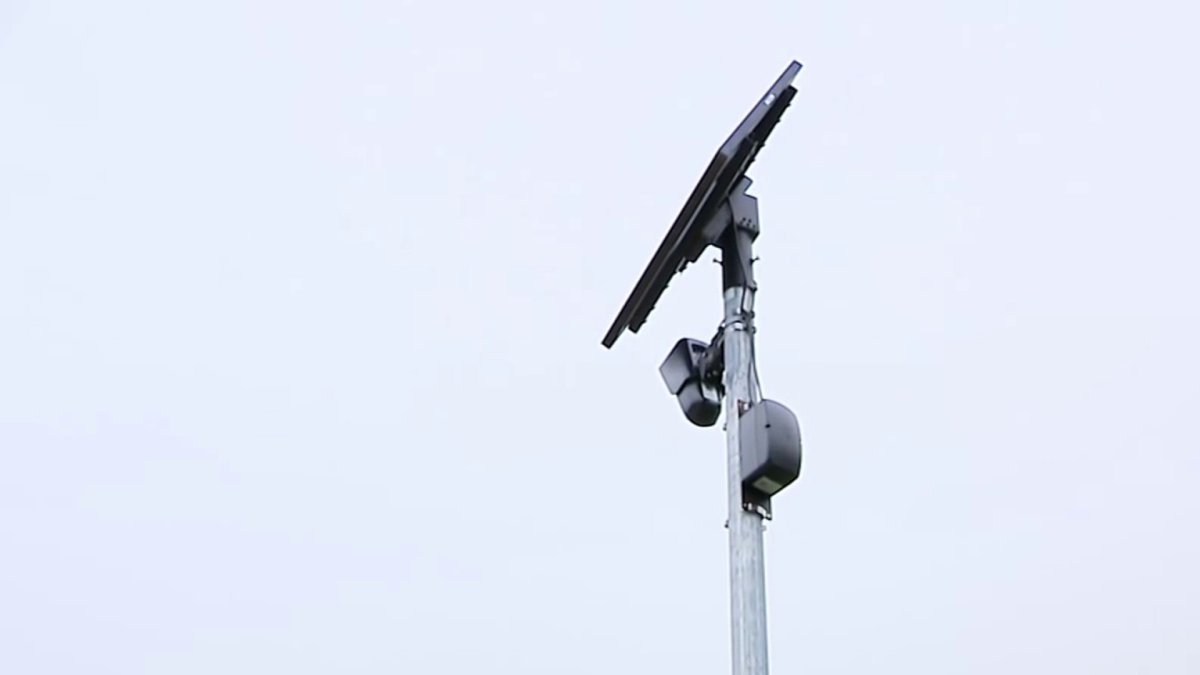
The Town of Ledyard, Connecticut, has decided to terminate its relationship with Flock after a security incident involving a data breach. Flock informed Ledyard Police Chief Ken Creutz that a malicious actor published a website containing sensitive customer device information, including device names, locations, and types. This breach raised significant concerns regarding privacy, security, and transparency. In light of these developments, Chief Creutz recommended that the town cease using Flock cameras, which had been installed to assist in crime-solving. The town council unanimously voted to stop data collection and sharing by the cameras. Ledyard had four Flock cameras, which have now been covered, and the town is willing to pay approximately $12,000 to exit the contract with Flock. The police chief has requested that the cameras be removed but has not received a response from Flock.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Flock in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…