 Bbc
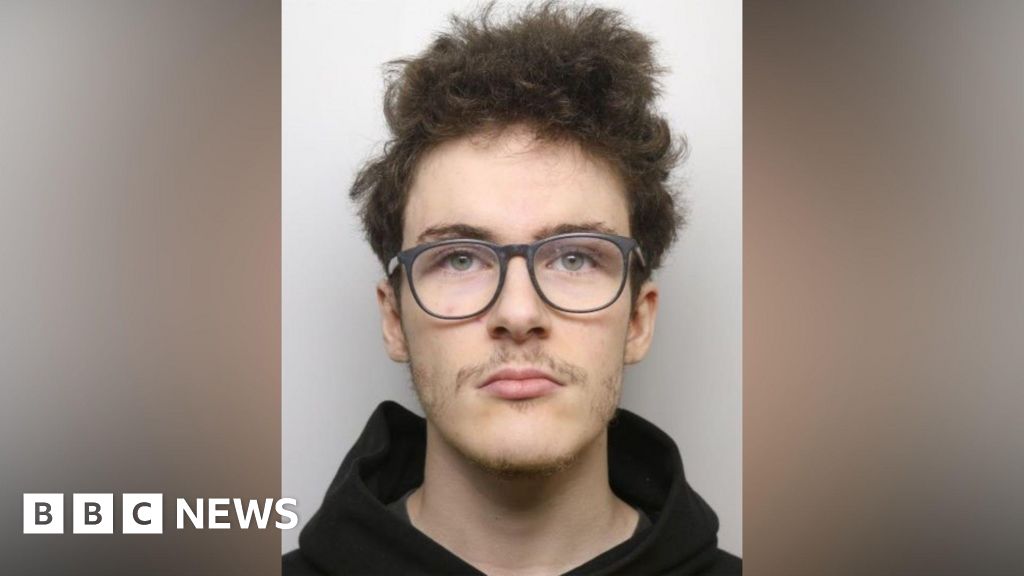
Leeds Man Jailed for Online Child Exploitation and Blackmail
Article Content

- •Justin Swaddle exploited over 100 young victims globally, coercing them into self-harm.
- •He was part of 'The Com,' an online group that uses social media for child exploitation.
- •Swaddle received a two-year prison sentence and will face a 10-year Sexual Harm Prevention Order.
Justin Swaddle, a 20-year-old from Leeds, has been sentenced to two years in prison for blackmail and sexual exploitation of over 100 young victims aged 13 to 17. He was part of 'The Com,' an online cybercrime group that coerced victims into self-harm and sexual acts. Swaddle used platforms like Snapchat, Telegram, and Discord under aliases such as 'Epstein' and 'Rugen.' His arrest followed an investigation by the National Crime Agency (NCA) that began in January 2024, revealing that he had collected private information to blackmail victims. The NCA identified 117 victims globally, with evidence of self-harm and indecent images found on his devices. Swaddle will be subject to a Sexual Harm Prevention Order for 10 years and must register as a sex offender. His actions highlight the dangers of online grooming and exploitation within secretive communities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Co-op in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…
 GitLab Issues Emergency Patch for Critical RCE Vulnerability GitLab has released emergency patches for a critical remote code execution vulnerability, CVE-2026-97229, affecting its Community and Enterprise Editions. This flaw, stemming from an integer overflow in the CI/CD regular expression compiler, allows unauthenticated attackers to execute arbitrary code via specially…