 Trend.Az
Luis Ocampo's Disinformation Campaign Against Azerbaijan Exposed
Article Content

- •Luis Ocampo is linked to a disinformation campaign against Azerbaijan involving EU influence.
- •Financial support for the campaign includes contributions from Armenian sources and Russian diaspora.
- •Official inquiries to European institutions regarding Ocampo's activities have received no response.
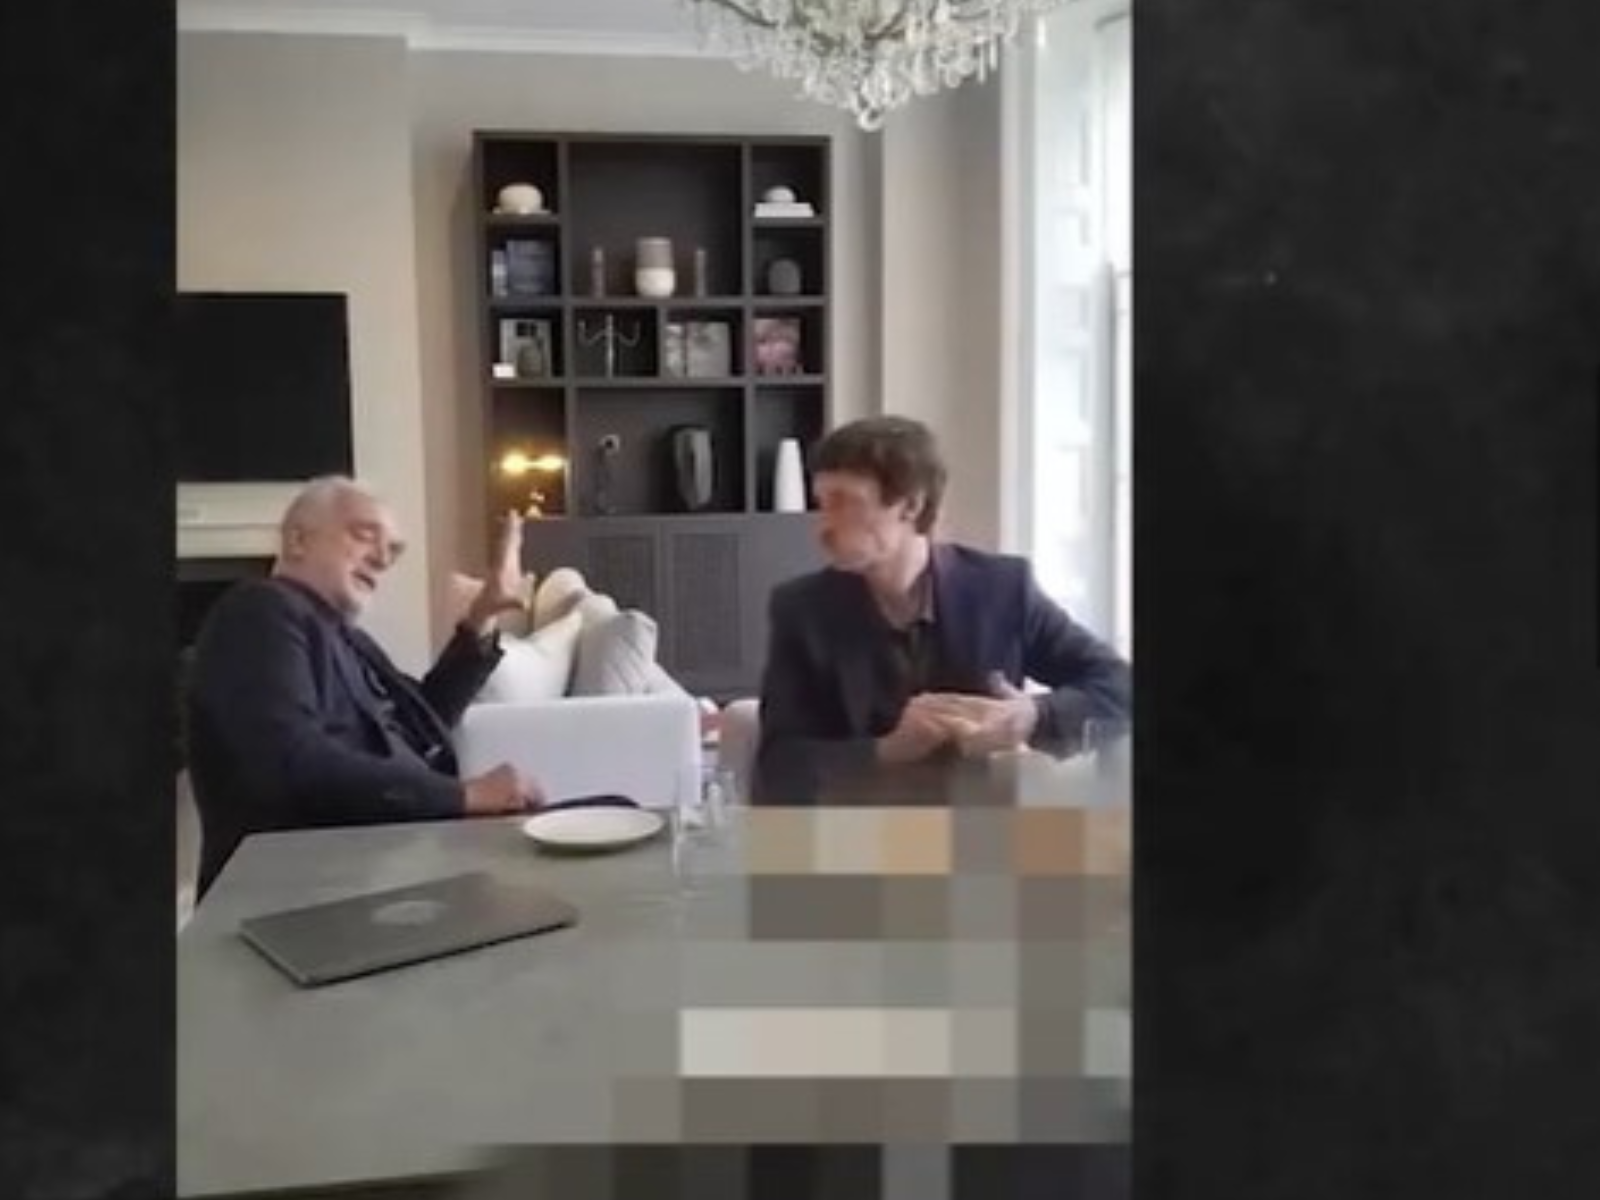
Luis Moreno Ocampo, former prosecutor of the International Criminal Court, has been implicated in a large-scale disinformation campaign against Azerbaijan, as revealed through a series of video recordings. The campaign is characterized as a systematic pressure mechanism involving the Armenian lobby, European politicians, and financial flows from Russian-Armenian business circles. Ocampo discusses his connections within the European Parliament and outlines methods to influence EU decisions, including potential pressure on the European Commission. Financial backing for the campaign reportedly comes from Armenian sources and wealthy diaspora members, including Samvel Karapetyan and Ruben Vardanyan. The operation is described as multi-faceted, targeting both Azerbaijan and regional stability. Official inquiries have been sent to European institutions regarding Ocampo's connections, but there has been no response. New video footage continues to emerge, further detailing Ocampo's plans to utilize artificial intelligence in this campaign. The situation remains unresolved as inquiries are ongoing.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…