 abc7news.com
AI Account Hacked: Unauthorized Charges in Euros Linked to Claude App
Article Content

- •Unauthorized charges of approximately $315 were made on a user's Anthropic Claude account.
- •The issue was linked to a compromised device rather than a flaw in the Claude app itself.
- •User support from Anthropic failed until media intervention prompted resolution and a refund.
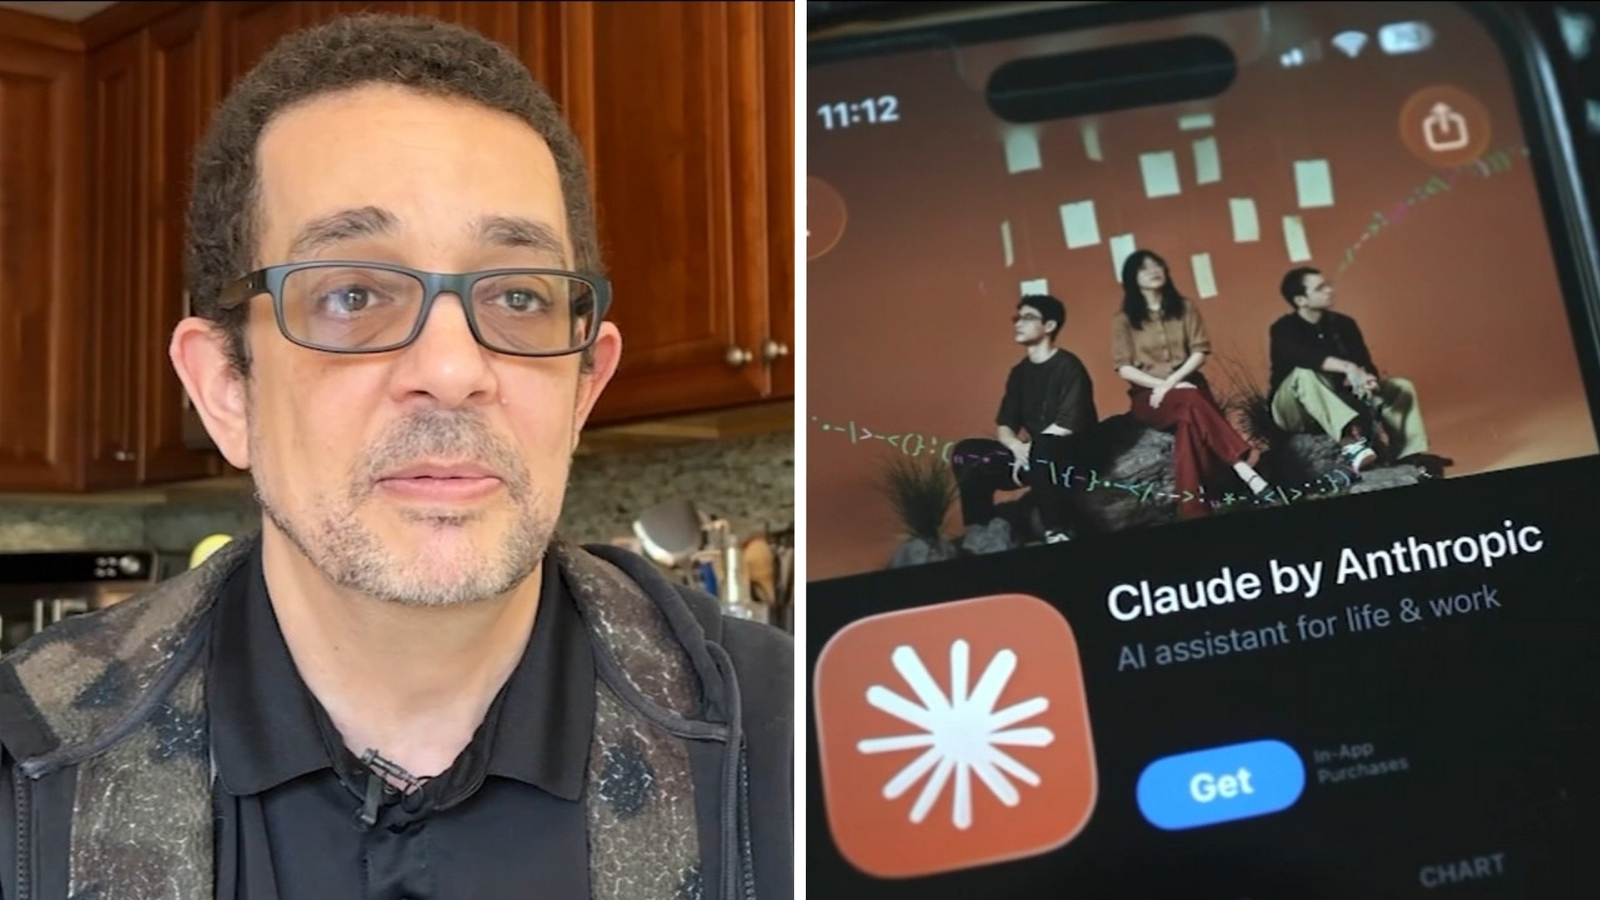
A Bay Area man, Jason Weitzman, reported unauthorized charges totaling around $315 on his Anthropic Claude account, which he claims were made without his consent. The charges were flagged by Chase Bank, prompting Weitzman to investigate. He discovered a problematic add-on, or 'skill', connected to Claude that used his stored payment information to make purchases. Anthropic stated that the issue stemmed from a compromise of Weitzman's device, not the Claude app itself. After multiple attempts to resolve the issue with Anthropic, Weitzman sought help from 7 On Your Side, which facilitated a resolution. Anthropic later refunded Weitzman and restored his access to Claude. The incident highlights potential vulnerabilities in AI applications and user device security.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Anthropic in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…