 ny1.com
Meloni Files EU Sound Mark for Her Voice to Counter AI Deepfakes
Article Content

- •Meloni personally applied to the EUIPO for a sound mark of a four-second recording of her voice on 5 October 2026.
- •The application is still under examination and has not been granted.
- •The filing is aimed at protecting against AI-generated voice and image deepfakes, per AP reporting.
- •Analysts note a voice trade mark is not a direct protection against deepfakes.
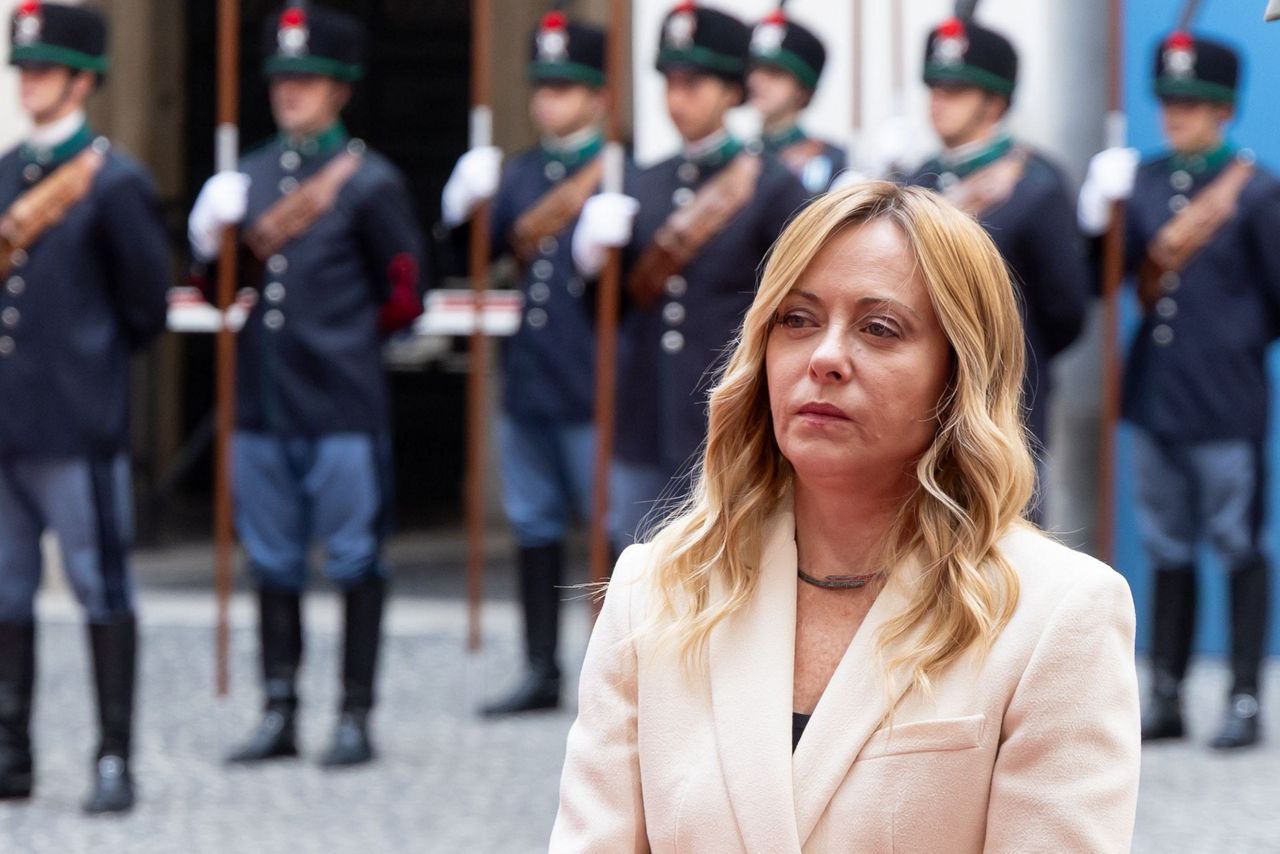
Italian Prime Minister Giorgia Meloni applied on 5 October 2026 to register a four-second audio recording of her saying "Io sono Giorgia Meloni" as a sound trade mark with the EU Intellectual Property Office (EUIPO), file EUTM 019431219, according to the EUIPO register and AP reporting. The filing was first reported by Italian daily La Repubblica and confirmed by an Italian official speaking anonymously. The application is filed by Meloni personally rather than by a government body, and is described as under examination, not a granted right. Its stated purpose, per AP, is to protect against AI-generated deepfakes; Meloni has said manipulated images of her have circulated online and that "I can defend myself, but many others cannot." One Iplink-Asia analysis argues a voice trade mark is a helpful tool but does not by itself protect against deepfakes, and questions whether trade mark law can fill gaps left by privacy, personality and copyright law. No attacks, breaches or vulnerabilities are involved; the story concerns a legal and policy response to AI voice cloning.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Euipo in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Does this trademark stop deepfakes?
Who filed the application?
What does the filing cover?
Continue Reading
 Critical Apache Roller RCE Vulnerability Actively Exploited in the Wild Apache has issued a warning regarding a critical remote code execution (RCE) vulnerability in Apache Roller, tracked as CVE-2026-129448, which is actively being exploited. This flaw affects versions 4.0.0 through 6.1.4 and allows unauthenticated attackers to execute arbitrary code via the XML-RPC endpoint. The…