 Adsadvance
MI5 Warns of Escalating State Threats to UK Defence Sector
Article Content

- •MI5 reports a quadrupling of state-threat cases in the last decade.
- •Russia is identified as the primary aggressor in hybrid warfare tactics.
- •Defence suppliers are urged to strengthen security against sabotage and drone threats.
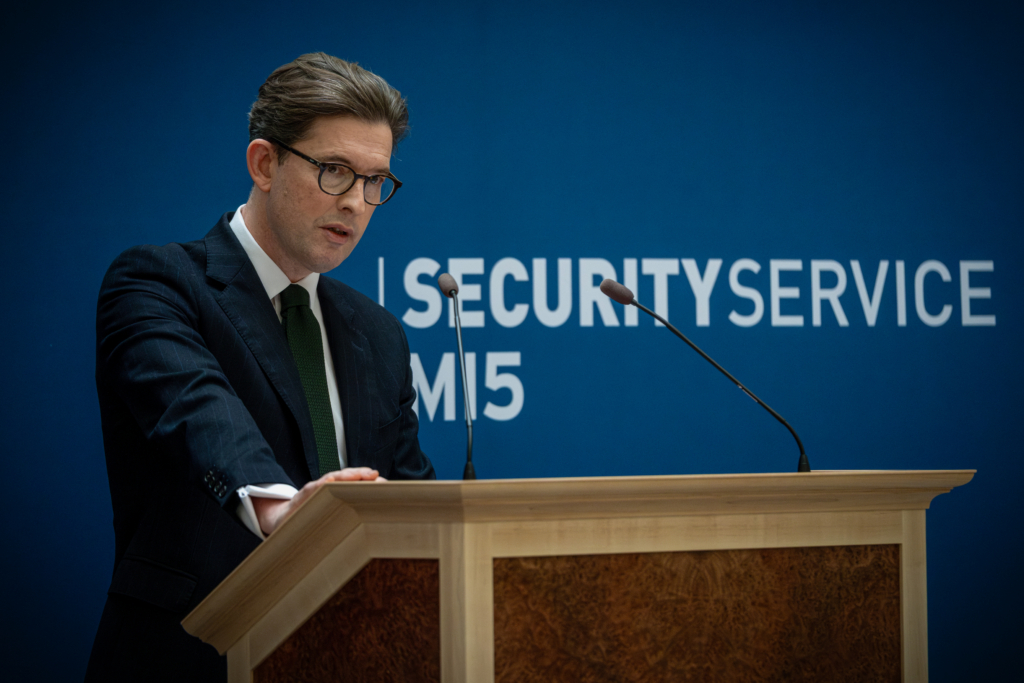
MI5's Director General, Sir Ken McCallum, announced that the agency is allocating more resources to counter state threats than during the Cold War. He reported a quadrupling of state-threat cases in the past decade, with Russia identified as the primary aggressor. Hybrid warfare tactics, including sabotage and drone threats, are increasingly targeting UK businesses, critical infrastructure, and supply chains. McCallum urged defence suppliers to enhance their security measures against these threats. He highlighted that hostile actors are focusing on non-governmental targets, aiming to intimidate and disrupt. The intelligence chief also noted the potential misuse of AI by extremist groups to enhance bioweapons and attack methodologies. MI5 has identified a growing number of incidents involving sabotage and hostile reconnaissance, particularly against energy and defence sectors. The agency has expelled nearly 1,000 Russian spies since the invasion of Ukraine, weakening Russia's covert operations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What specific threats should defence suppliers be aware of?
How has MI5's focus changed in recent years?
What actions does MI5 recommend for resilience?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…