 Thurrott
Microsoft Edge Enhances Update Process to Minimize Disruption
Article Content

- •Microsoft Edge introduces a seamless update prototype to minimize user disruptions.
- •The 'Restart to update on idle' feature is currently available for users to opt-in.
- •A new Security Updates Alert feature will help organizations manage critical updates.
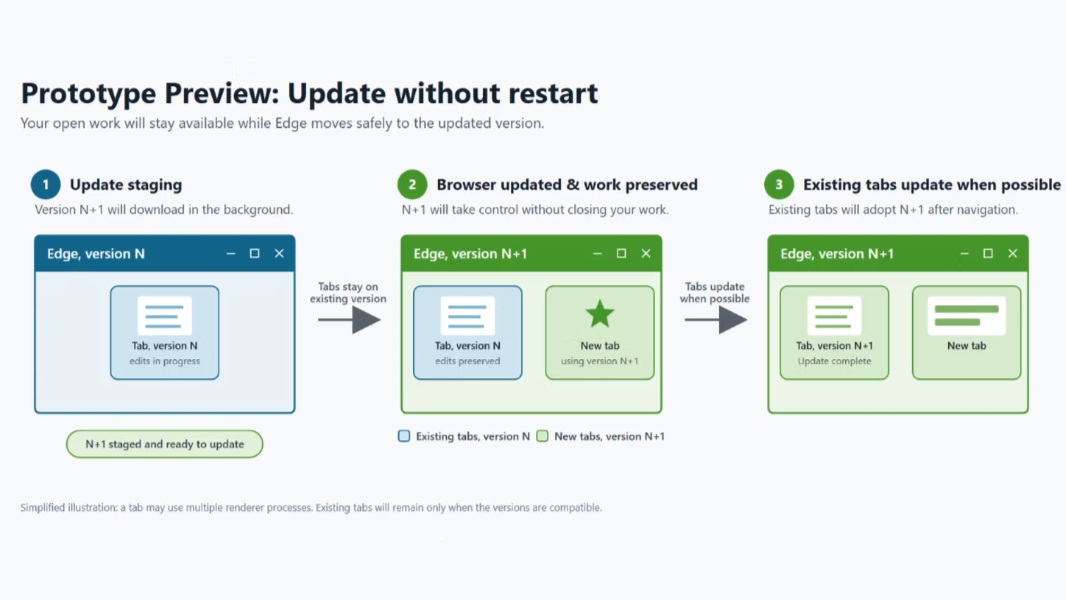
Microsoft Edge is introducing a new update mechanism aimed at reducing interruptions during security updates. The 'seamless updates' prototype allows the browser to transition to a more secure version while users continue working, eliminating the need for restart prompts. Currently, an opt-in feature called 'Restart to update on idle' is available, which relaunches Edge when the device is idle to apply pending updates. This feature aims to address the inconvenience of manual updates that often lead to users delaying necessary security patches. Additionally, a new Security Updates Alert feature for businesses will notify admins of critical updates. These changes come in response to the increasing pace of security threats, particularly those accelerated by AI. The seamless updates prototype is still under development and not yet part of the production code.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
What is the seamless updates prototype?
How does Restart to update on idle work?
What benefits does the Security Updates Alert provide?
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…