 www.windowscentral.com
Microsoft Ends Copilot Support on Smart TVs Amid User Backlash
Article Content

- •Microsoft is ending Copilot support on all smart TVs due to user backlash.
- •The discontinuation affects LG and Samsung TVs with the Copilot feature.
- •The decision reflects a strategic shift towards business applications for Copilot.
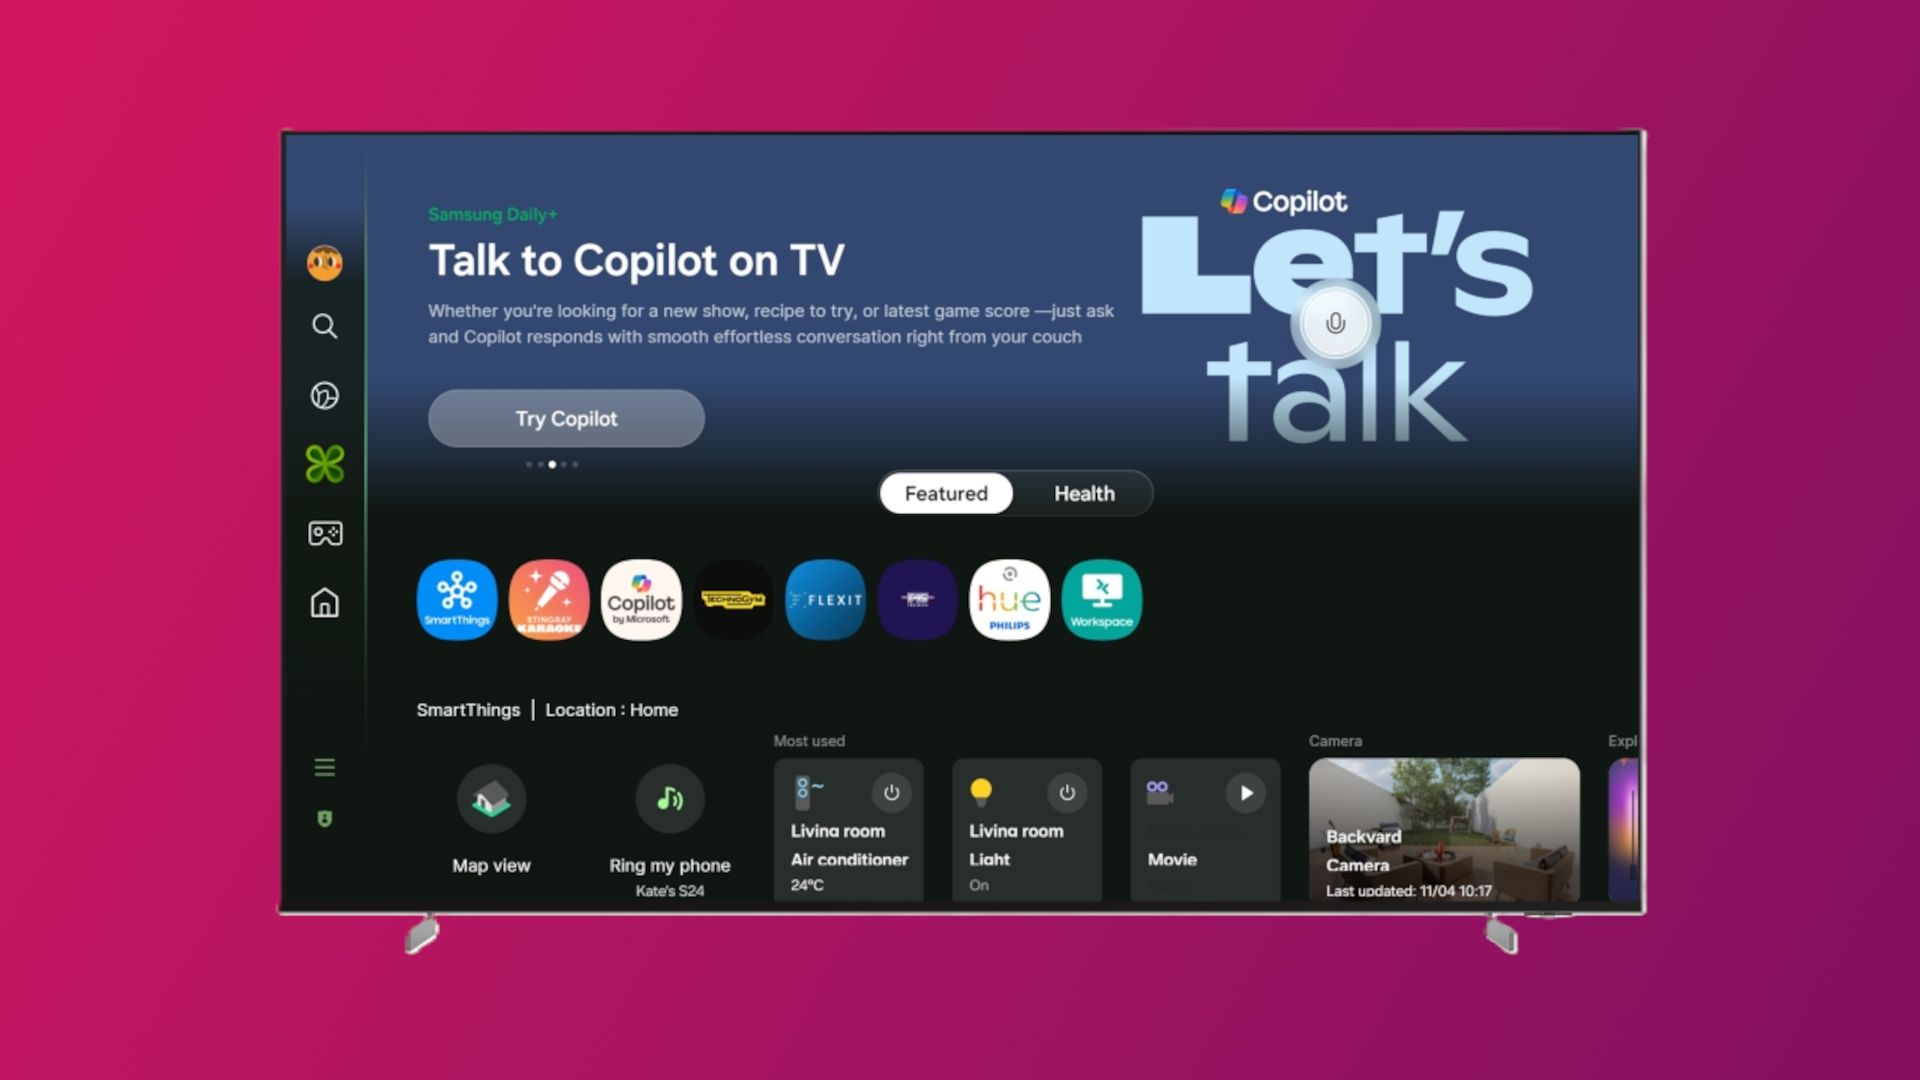
Microsoft is discontinuing support for its Copilot AI assistant on all smart TVs, including those from LG and Samsung, as confirmed by a notification on LG TVs. The decision follows user dissatisfaction with the unremovable Copilot shortcut added to LG TVs last year. The feature, which allowed users to interact with an AI companion for content recommendations, will cease functioning sometime in 2026, although a specific date has not been provided. This shift aligns with Microsoft's new strategy to focus Copilot on business and productivity applications rather than personal use. The announcement was not made through official channels but was revealed via an on-screen notification. Users had previously expressed frustration over the forced installation of the Copilot feature, leading to significant backlash. Microsoft has not disclosed the exact timeline for the discontinuation of the service, but it is expected to happen before the end of the year.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track LG in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
When will Copilot stop working?
Why is Microsoft discontinuing Copilot on TVs?
Which TVs are affected by this change?
Continue Reading
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…
 GitLab Issues Emergency Patch for Critical RCE Vulnerability GitLab has released emergency patches for a critical remote code execution vulnerability, CVE-2026-97229, affecting its Community and Enterprise Editions. This flaw, stemming from an integer overflow in the CI/CD regular expression compiler, allows unauthenticated attackers to execute arbitrary code via specially…